Intel 64 and IA-32 Architectures. Software Developer’s Manual (2026) - page 68
INTEL® SGX INSTRUCTION REFERENCES
Flags Affected
Sets ZF if page is not modifiable, otherwise cleared. Clears CF, PF, AF, OF, SF.
Protected Mode Exceptions
#GP(0)
If executed outside an enclave.
If a memory operand effective address is outside the DS segment limit.
If a memory operand is not properly aligned.
If a memory operand is locked.
#PF(error code)
If a page fault occurs in accessing memory operands.
If a memory operand is not an EPC page.
If EPC page has incorrect page type or security attributes.
64-Bit Mode Exceptions
#GP(0)
If executed outside an enclave.
If a memory operand is non-canonical form.
If a memory operand is not properly aligned.
If a memory operand is locked.
#PF(error code)
If a page fault occurs in accessing memory operands.
If a memory operand is not an EPC page.
If EPC page has incorrect page type or security attributes.
41-82
Vol. 3D
EACCEPTCOPY-Initialize a Pending Page
INTEL® SGX INSTRUCTION REFERENCES
EDECCSSA-Decrements TCS.CSSA
Opcode/
Op/En
64/32
CPUID
Description
Instruction
bit Mode
Feature
Support
Flag
EAX = 09H
IR
V/V
EDECCSSA
This leaf function decrements TCS.CSSA.
ENCLU[EDECCSSA]
Instruction Operand Encoding
Op/En
EAX
IR
EDECCSSA (In)
Description
This leaf function changes the current SSA frame by decrementing TCS.CSSA for the current enclave thread. If the
enclave has enabled CET shadow stacks or indirect branch tracking, then EDECCSSA also changes the current CET
state save frame. This instruction leaf can only be executed inside an enclave.
EDECCSSA Memory Parameter Semantics
TCS
Read/Write access by Enclave
The instruction faults if any of the following:
EDECCSSA Faulting Conditions
TCS.CSSA is 0.
TCS is not valid or available or locked.
The SSA frame is not valid or in use.
Concurrency Restrictions
Table 41-56. Base Concurrency Restrictions of EDECCSSA
Base Concurrency Restrictions
Leaf
Parameter
Access
On Conflict
EDECCSSA
TCS [CR_TCS_PA]
Shared
#GP
Table 41-57. Additional Concurrency Restrictions of EDECCSSA
Additional Concurrency Restrictions
vs. EACCEPT, EACCEPTCOPY,
Leaf
Parameter
vs. EADD, EEXTEND, EINIT
vs. ETRACK
EMODPE, EMODPR, EMODT
Access
On Conflict
Access
On Conflict
Access
On Conflict
EDECCSSA
TCS [CR_TCS_PA]
Concurrent
Concurrent
Concurrent
EDECCSSA-Decrements TCS.CSSA
Vol. 3D
41-83

INTEL® SGX INSTRUCTION REFERENCES
Operation
Temp Variables in EDECCSSA Operational Flow
Name
Type
Size (bits)
Description
TMP_SSA
Effective
32/64
Address of current SSA frame.
Address
TMP_XSIZE
Integer
64
Size of XSAVE area based on SECS.ATTRIBUTES.XFRM.
TMP_SSA_PAGE
Effective
32/64
Pointer used to iterate over the SSA pages in the target frame.
Address
TMP_GPR
Effective
32/64
Address of the GPR area within the target SSA frame.
Address
TMP_XSAVE_PAGE_PA_n
Physical
32/64
Physical address of the nth page within the target SSA frame.
Address
TMP_CET_SAVE_AREA
Effective
32/64
Address of the current CET save area.
Address
TMP_CET_SAVE_PAGE
Effective
32/64
Address of the current CET save area page.
Address
(* Check concurrency of TCS operation *)
IF (Other Intel SGX instructions are operating on TCS)
THEN #GP(0); FI;
IF (CR_TCS_PA.CSSA = 0)
THEN #GP(0); FI;
(* Compute linear address of SSA frame *)
TMP_SSA := CR_TCS_PA.OSSA + CR_ACTIVE_SECS.BASEADDR + 4096 * CR_ACTIVE_SECS.SSAFRAMESIZE * (CR_TCS_PA.CSSA - 1);
TMP_XSIZE := compute_XSAVE_frame_size(CR_ACTIVE_SECS.ATTRIBUTES.XFRM);
FOR EACH TMP_SSA_PAGE = TMP_SSA to TMP_SSA + TMP_XSIZE
(* Check page is read/write accessible *)
Check that DS:TMP_SSA_PAGE is read/write accessible;
If a fault occurs, release locks, abort and deliver that fault;
IF (DS:TMP_SSA_PAGE does not resolve to EPC page)
THEN #PF(DS:TMP_SSA_PAGE); FI;
IF (EPCM(DS:TMP_SSA_PAGE).VALID = 0)
THEN #PF(DS:TMP_SSA_PAGE); FI;
IF (EPCM(DS:TMP_SSA_PAGE).BLOCKED = 1)
THEN #PF(DS:TMP_SSA_PAGE); FI;
IF ((EPCM(DS:TMP_SSA_PAGE).PENDING = 1) or (EPCM(DS:TMP_SSA_PAGE_.MODIFIED = 1))
THEN #PF(DS:TMP_SSA_PAGE); FI;
IF ( ( EPCM(DS:TMP_SSA_PAGE).ENCLAVEADDRESS ≠ DS:TMPSSA_PAGE) or
(EPCM(DS:TMP_SSA_PAGE).PT ≠ PT_REG) or
(EPCM(DS:TMP_SSA_PAGE).ENCLAVESECS ≠ EPCM(CR_TCS_PA).ENCLAVESECS) or
(EPCM(DS:TMP_SSA_PAGE).R = 0) or (EPCM(DS:TMP_SSA_PAGE).W = 0))
THEN #PF(DS:TMP_SSA_PAGE); FI;
TMP_XSAVE_PAGE_PA_n := Physical_Address(DS:TMP_SSA_PAGE);
ENDFOR
(* Compute address of GPR area*)
TMP_GPR := TMP_SSA + 4096 * CR_ACTIVE_SECS.SSAFRAMESIZE - sizeof(GPRSGX_AREA);
41-84
Vol. 3D
EDECCSSA-Decrements TCS.CSSA
INTEL® SGX INSTRUCTION REFERENCES
Check that DS:TMP_SSA_PAGE is read/write accessible;
If a fault occurs, release locks, abort and deliver that fault;
IF (DS:TMP_GPR does not resolve to EPC page)
THEN #PF(DS:TMP_GPR); FI;
IF (EPCM(DS:TMP_GPR).VALID = 0)
THEN #PF(DS:TMP_GPR); FI;
IF (EPCM(DS:TMP_GPR).BLOCKED = 1)
THEN #PF(DS:TMP_GPR); FI;
IF ((EPCM(DS:TMP_GPR).PENDING = 1) or (EPCM(DS:TMP_GPR).MODIFIED = 1))
THEN #PF(DS:TMP_GPR); FI;
IF ( ( EPCM(DS:TMP_GPR).ENCLAVEADDRESS ≠ DS:TMP_GPR) or
(EPCM(DS:TMP_GPR).PT ≠ PT_REG) or
(EPCM(DS:TMP_GPR).ENCLAVESECS ≠ EPCM(CR_TCS_PA).ENCLAVESECS) or
(EPCM(DS:TMP_GPR).R = 0) or (EPCM(DS:TMP_GPR).W = 0) )
THEN #PF(DS:TMP_GPR); FI;
IF (TMP_MODE64 = 0)
THEN
IF (TMP_GPR + (sizeof(GPRSGX_AREA) -1) is not in DS segment)
THEN #GP(0); FI;
FI;
IF (CPUID.12H.01H:EAX[6] = 1)
THEN
IF ((CR_ACTIVE_SECS.CET_ATTRIBUTES.SH_STK_EN == 1) OR (CR_ACTIVE_SECS.CET_ATTRIBUTES.ENDBR_EN == 1))
THEN
(* Compute linear address of what will become new CET state save area and cache its PA *)
TMP_CET_SAVE_AREA := CR_TCS_PA.OCETSSA + CR_ACTIVE_SECS.BASEADDR + (CR_TCS_PA.CSSA - 1) * 16;
TMP_CET_SAVE_PAGE := TMP_CET_SAVE_AREA & ~0xFFF;
Check the TMP_CET_SAVE_PAGE page is read/write accessible
If fault occurs release locks, abort and deliver fault
(* read the EPCM VALID, PENDING, MODIFIED, BLOCKED and PT fields atomically *)
IF ((DS:TMP_CET_SAVE_PAGE Does NOT RESOLVE TO EPC PAGE) OR
(EPCM(DS:TMP_CET_SAVE_PAGE).VALID = 0) OR
(EPCM(DS:TMP_CET_SAVE_PAGE).PENDING = 1) OR
(EPCM(DS:TMP_CET_SAVE_PAGE).MODIFIED = 1) OR
(EPCM(DS:TMP_CET_SAVE_PAGE).BLOCKED = 1) OR
(EPCM(DS:TMP_CET_SAVE_PAGE).R = 0) OR
(EPCM(DS:TMP_CET_SAVE_PAGE).W = 0) OR
(EPCM(DS:TMP_CET_SAVE_PAGE).ENCLAVEADDRESS ≠ DS:TMP_CET_SAVE_PAGE) OR
(EPCM(DS:TMP_CET_SAVE_PAGE).PT ≠ PT_SS_REST) OR
(EPCM(DS:TMP_CET_SAVE_PAGE).ENCLAVESECS ≠ EPCM(CR_TCS_PA).ENCLAVESECS))
THEN #PF(DS:TMP_CET_SAVE_PAGE); FI;
FI;
FI;
(* At this point, the instruction is guaranteed to complete *)
CR_TCS_PA.CSSA := CR_TCS_PA.CSSA - 1;
CR_GPR_PA := Physical_Address(DS:TMP_GPR);
FOR EACH TMP_XSAVE_PAGE_n
CR_XSAVE_PAGE_n := TMP_XSAVE_PAGE_PA_n;
EDECCSSA-Decrements TCS.CSSA
Vol. 3D
41-85
INTEL® SGX INSTRUCTION REFERENCES
ENDFOR
IF (CPUID.12H.01H:EAX[6] = 1)
THEN
IF ((TMP_SECS.CET_ATTRIBUTES.SH_STK_EN == 1) OR
(TMP_SECS.CET_ATTRIBUTES.ENDBR_EN == 1))
THEN
CR_CET_SAVE_AREA_PA := Physical_Address(DS:TMP_CET_SAVE_AREA);
FI;
FI;
Flags Affected
None
Protected Mode Exceptions
#GP(0)
If executed outside an enclave.
If CR_TCS_PA.CSSA = 0.
#PF(error code)
If a page fault occurs in accessing memory.
If one or more pages of the target SSA frame are not readable/writable, or do not resolve to a
valid PT_REG EPC page.
If CET is enabled for the enclave and the target CET SSA frame is not readable/writable, or
does not resolve to a valid PT_REG EPC page.
64-Bit Mode Exceptions
#GP(0)
If executed outside an enclave.
If CR_TCS_PA.CSSA = 0.
#PF(error code)
If a page fault occurs in accessing memory.
If one or more pages of the target SSA frame are not readable/writable, or do not resolve to a
valid PT_REG EPC page.
If CET is enabled for the enclave and the target CET SSA frame is not readable/writable, or
does not resolve to a valid PT_REG EPC page.
41-86
Vol. 3D
EDECCSSA-Decrements TCS.CSSA
INTEL® SGX INSTRUCTION REFERENCES
EENTER-Enters an Enclave
Opcode/
Op/En
64/32
CPUID
Description
Instruction
bit Mode
Feature
Support
Flag
EAX = 02H
IR
V/V
SGX1
This leaf function is used to enter an enclave.
ENCLU[EENTER]
Instruction Operand Encoding
Op/En
EAX
RBX
RCX
Content of RBX.CSSA
Address of IP following
IR
EENTER (In)
Address of a TCS (In)
Address of AEP (In)
(Out)
EENTER (Out)
Description
The ENCLU[EENTER] instruction transfers execution to an enclave. At the end of the instruction, the logical
processor is executing in enclave mode at the RIP computed as EnclaveBase + TCS.OENTRY. If the target address
is not within the CS segment (32-bit) or is not canonical (64-bit), a #GP(0) results.
EENTER Memory Parameter Semantics
TCS
Enclave access
EENTER is a serializing instruction. The instruction faults if any of the following occurs:
Address in RBX is not properly aligned.
Any TCS.FLAGS’s must-be-zero bit is not zero.
TCS pointed to by RBX is not valid or available or locked.
Current 32/64 mode does not match the enclave mode in
SECS.ATTRIBUTES.MODE64.
The SECS is in use.
Either of TCS-specified FS and GS segment is not a subsets of the
current DS segment.
Any one of DS, ES, CS, SS is not zero.
If XSAVE available, CR4.OSXSAVE = 0, but
SECS.ATTRIBUTES.XFRM ≠ 3.
CR4.OSFXSR ≠ 1.
If CR4.OSXSAVE = 1, SECS.ATTRIBUTES.XFRM is not a subset of
XCR0.
If SECS.ATTRIBUTES.AEXNOTIFY ≠ TCS.FLAGS.AEXNOTIFY and
TCS.FLAGS.DBGOPTIN = 0.
The following operations are performed by EENTER:
• RSP and RBP are saved in the current SSA frame on EENTER and are automatically restored on EEXIT or
interrupt.
• The AEP contained in RCX is stored into the TCS for use by AEXs.FS and GS (including hidden portions) are
saved and new values are constructed using TCS.OFSBASE/GSBASE (32 and 64-bit mode) and
TCS.OFSLIMIT/GSLIMIT (32-bit mode only). The resulting segments must be a subset of the DS segment.
• If CR4.OSXSAVE == 1, XCR0 is saved and replaced by SECS.ATTRIBUTES.XFRM. The effect of RFLAGS.TF
depends on whether the enclave entry is opt-in or opt-out (see Section 43.1.2):
- On opt-out entry, TF is saved and cleared (it is restored on EEXIT or AEX). Any attempt to set TF via a POPF
instruction while inside the enclave clears TF (see Section 43.2.5).
- On opt-in entry, a single-step debug exception is pended on the instruction boundary immediately after
EENTER (see Section 43.2.2).
EENTER-Enters an Enclave
Vol. 3D
41-87
INTEL® SGX INSTRUCTION REFERENCES
• All code breakpoints that do not overlap with ELRANGE are also suppressed. If the entry is an opt-out entry, all
code and data breakpoints that overlap with the ELRANGE are suppressed.
• On opt-out entry, a number of performance monitoring counters and behaviors are modified or suppressed (see
Section 43.2.3):
- All performance monitoring activity on the current thread is suppressed except for incrementing and firing
of FIXED_CTR1 and FIXED_CTR2.
- PEBS is suppressed.
- AnyThread counting on other threads is demoted to MyThread mode and IA32_PERF_GLOBAL_STATUS[60]
on that thread is set
- If the opt-out entry on a hardware thread results in suppression of any performance monitoring, then the
processor sets IA32_PERF_GLOBAL_STATUS[60] and IA32_PERF_GLOBAL_STATUS[63].
Concurrency Restrictions
Table 41-58. Base Concurrency Restrictions of EENTER
Base Concurrency Restrictions
Leaf
Parameter
Access
On Conflict
EENTER
TCS [DS:RBX]
Shared
#GP
Table 41-59. Additional Concurrency Restrictions of EENTER
Additional Concurrency Restrictions
vs. EACCEPT, EACCEPTCOPY,
Leaf
Parameter
vs. EADD, EEXTEND, EINIT
vs. ETRACK
EMODPE, EMODPR, EMODT
Access
On Conflict
Access
On Conflict
Access
On Conflict
EENTER
TCS [DS:RBX]
Concurrent
Concurrent
Concurrent
Operation
Temp Variables in EENTER Operational Flow
Name
Type
Size (Bits)
Description
TMP_FSBASE
Effective Address
32/64
Proposed base address for FS segment.
TMP_GSBASE
Effective Address
32/64
Proposed base address for FS segment.
TMP_FSLIMIT
Effective Address
32/64
Highest legal address in proposed FS segment.
TMP_GSLIMIT
Effective Address
32/64
Highest legal address in proposed GS segment.
TMP_XSIZE
integer
64
Size of XSAVE area based on SECS.ATTRIBUTES.XFRM.
TMP_SSA_PAGE
Effective Address
32/64
Pointer used to iterate over the SSA pages in the current frame.
TMP_GPR
Effective Address
32/64
Address of the GPR area within the current SSA frame.
TMP_MODE64 := ((IA32_EFER.LMA = 1) && (CS.L = 1));
(* Make sure DS is usable, expand up *)
IF (TMP_MODE64 = 0 and (DS not usable or DS[bits 11:9] != 001B))
THEN #GP(0); FI;
(* Check that CS, SS, DS, ES.base is 0 *)
IF (TMP_MODE64 = 0)
THEN
41-88
Vol. 3D
EENTER-Enters an Enclave
INTEL® SGX INSTRUCTION REFERENCES
IF(CS.base ≠ 0 or DS.base ≠ 0) #GP(0); FI;
IF(ES usable and ES.base ≠ 0) #GP(0); FI;
IF(SS usable and SS.base ≠ 0) #GP(0); FI;
IF(SS usable and SS.B = 0) #GP(0); FI;
FI;
IF (DS:RBX is not 4KByte Aligned)
THEN #GP(0); FI;
IF (DS:RBX does not resolve within an EPC)
THEN #PF(DS:RBX); FI;
(* Check AEP is canonical*)
IF (TMP_MODE64 = 1 and (CS:RCX is not canonical) )
THEN #GP(0); FI;
(* Check concurrency of TCS operation*)
IF (Other Intel SGX instructions are operating on TCS)
THEN #GP(0); FI;
(* TCS verification *)
IF (EPCM(DS:RBX).VALID = 0)
THEN #PF(DS:RBX); FI;
IF (EPCM(DS:RBX).BLOCKED = 1)
THEN #PF(DS:RBX); FI;
IF ( (EPCM(DS:RBX).ENCLAVEADDRESS ≠ DS:RBX) or (EPCM(DS:RBX).PT ≠ PT_TCS) )
THEN #PF(DS:RBX); FI;
IF ((EPCM(DS:RBX).PENDING = 1) or (EPCM(DS:RBX).MODIFIED = 1))
THEN #PF(DS:RBX); FI;
IF ( (DS:RBX).OSSA is not 4KByte Aligned)
THEN #GP(0); FI;
(* Check proposed FS and GS *)
IF ( ( (DS:RBX).OFSBASE is not 4KByte Aligned) or ( (DS:RBX).OGSBASE is not 4KByte Aligned) )
THEN #GP(0); FI;
(* Get the SECS for the enclave in which the TCS resides *)
TMP_SECS := Address of SECS for TCS;
(* Ensure that the FLAGS field in the TCS does not have any reserved bits set *)
IF ( ( (DS:RBX).FLAGS & FFFFFFFFFFFFFFFCH) ≠ 0)
THEN #GP(0); FI;
(* SECS must exist and enclave must have previously been EINITted *)
IF (the enclave is not already initialized)
THEN #GP(0); FI;
(* make sure the logical processor’s operating mode matches the enclave *)
IF ( (TMP_MODE64 ≠ TMP_SECS.ATTRIBUTES.MODE64BIT) )
THEN #GP(0); FI;
EENTER-Enters an Enclave
Vol. 3D
41-89
INTEL® SGX INSTRUCTION REFERENCES
IF (CR4.OSFXSR = 0)
THEN #GP(0); FI;
(* Check for legal values of SECS.ATTRIBUTES.XFRM *)
IF (CR4.OSXSAVE = 0)
THEN
IF (TMP_SECS.ATTRIBUTES.XFRM ≠ 03H) THEN #GP(0); FI;
ELSE
IF ( (TMP_SECS.ATTRIBUTES.XFRM & XCR0) ≠ TMP_SECS.ATTRIBUES.XFRM) THEN #GP(0); FI;
FI;
IF ((DS:RBX).CSSA.FLAGS.DBGOPTIN = 0) and (DS:RBX).CSSA.FLAGS.AEXNOTIFY ≠ TMP_SECS.ATTRIBUTES.AEXNOTIFY))
THEN #GP(0); FI;
(* Make sure the SSA contains at least one more frame *)
IF ( (DS:RBX).CSSA ≥ (DS:RBX).NSSA)
THEN #GP(0); FI;
(* Compute linear address of SSA frame *)
TMP_SSA := (DS:RBX).OSSA + TMP_SECS.BASEADDR + 4096 * TMP_SECS.SSAFRAMESIZE * (DS:RBX).CSSA;
TMP_XSIZE := compute_XSAVE_frame_size(TMP_SECS.ATTRIBUTES.XFRM);
FOR EACH TMP_SSA_PAGE = TMP_SSA to TMP_SSA + TMP_XSIZE
(* Check page is read/write accessible *)
Check that DS:TMP_SSA_PAGE is read/write accessible;
If a fault occurs, release locks, abort, and deliver that fault;
IF (DS:TMP_SSA_PAGE does not resolve to EPC page)
THEN #PF(DS:TMP_SSA_PAGE); FI;
IF (EPCM(DS:TMP_SSA_PAGE).VALID = 0)
THEN #PF(DS:TMP_SSA_PAGE); FI;
IF (EPCM(DS:TMP_SSA_PAGE).BLOCKED = 1)
THEN #PF(DS:TMP_SSA_PAGE); FI;
IF ((EPCM(DS:TMP_SSA_PAGE).PENDING = 1) or (EPCM(DS:TMP_SSA_PAGE).MODIFIED = 1))
THEN #PF(DS:TMP_SSA_PAGE); FI;
IF ( ( EPCM(DS:TMP_SSA_PAGE).ENCLAVEADDRESS ≠ DS:TMP_SSA_PAGE) or (EPCM(DS:TMP_SSA_PAGE).PT ≠ PT_REG) or
(EPCM(DS:TMP_SSA_PAGE).ENCLAVESECS ≠ EPCM(DS:RBX).ENCLAVESECS) or
(EPCM(DS:TMP_SSA_PAGE).R = 0) or (EPCM(DS:TMP_SSA_PAGE).W = 0) )
THEN #PF(DS:TMP_SSA_PAGE); FI;
CR_XSAVE_PAGE_n := Physical_Address(DS:TMP_SSA_PAGE);
ENDFOR
(* Compute address of GPR area*)
TMP_GPR := TMP_SSA + 4096 * DS:TMP_SECS.SSAFRAMESIZE - sizeof(GPRSGX_AREA);
If a fault occurs; release locks, abort, and deliver that fault;
IF (DS:TMP_GPR does not resolve to EPC page)
THEN #PF(DS:TMP_GPR); FI;
IF (EPCM(DS:TMP_GPR).VALID = 0)
THEN #PF(DS:TMP_GPR); FI;
IF (EPCM(DS:TMP_GPR).BLOCKED = 1)
THEN #PF(DS:TMP_GPR); FI;
IF ((EPCM(DS:TMP_GPR).PENDING = 1) or (EPCM(DS:TMP_GPR).MODIFIED = 1))
THEN #PF(DS:TMP_GPR); FI;
41-90
Vol. 3D
EENTER-Enters an Enclave
INTEL® SGX INSTRUCTION REFERENCES
IF ( ( EPCM(DS:TMP_GPR).ENCLAVEADDRESS ≠ DS:TMP_GPR) or (EPCM(DS:TMP_GPR).PT ≠ PT_REG) or
(EPCM(DS:TMP_GPR).ENCLAVESECS EPCM(DS:RBX).ENCLAVESECS) or
(EPCM(DS:TMP_GPR).R = 0) or (EPCM(DS:TMP_GPR).W = 0) )
THEN #PF(DS:TMP_GPR); FI;
IF (TMP_MODE64 = 0)
THEN
IF (TMP_GPR + (GPR_SIZE -1) is not in DS segment) THEN #GP(0); FI;
FI;
CR_GPR_PA := Physical_Address (DS: TMP_GPR);
(* Validate TCS.OENTRY *)
TMP_TARGET := (DS:RBX).OENTRY + TMP_SECS.BASEADDR;
IF (TMP_MODE64 = 1)
THEN
IF (TMP_TARGET is not canonical) THEN #GP(0); FI;
ELSE
IF (TMP_TARGET > CS limit) THEN #GP(0); FI;
FI;
(* Check proposed FS/GS segments fall within DS *)
IF (TMP_MODE64 = 0)
THEN
TMP_FSBASE := (DS:RBX).OFSBASE + TMP_SECS.BASEADDR;
TMP_FSLIMIT := (DS:RBX).OFSBASE + TMP_SECS.BASEADDR + (DS:RBX).FSLIMIT;
TMP_GSBASE := (DS:RBX).OGSBASE + TMP_SECS.BASEADDR;
TMP_GSLIMIT := (DS:RBX).OGSBASE + TMP_SECS.BASEADDR + (DS:RBX).GSLIMIT;
(* if FS wrap-around, make sure DS has no holes*)
IF (TMP_FSLIMIT < TMP_FSBASE)
THEN
IF (DS.limit < 4GB) THEN #GP(0); FI;
ELSE
IF (TMP_FSLIMIT > DS.limit) THEN #GP(0); FI;
FI;
(* if GS wrap-around, make sure DS has no holes*)
IF (TMP_GSLIMIT < TMP_GSBASE)
THEN
IF (DS.limit < 4GB) THEN #GP(0); FI;
ELSE
IF (TMP_GSLIMIT > DS.limit) THEN #GP(0); FI;
FI;
ELSE
TMP_FSBASE := (DS:RBX).OFSBASE + TMP_SECS.BASEADDR;
TMP_GSBASE := (DS:RBX).OGSBASE + TMP_SECS.BASEADDR;
IF ( (TMP_FSBASE is not canonical) or (TMP_GSBASE is not canonical))
THEN #GP(0); FI;
FI;
(* Ensure the enclave is not already active and this thread is the only one using the TCS*)
IF (DS:RBX.STATE = ACTIVE)
THEN #GP(0); FI;
TMP_IA32_U_CET := 0
EENTER-Enters an Enclave
Vol. 3D
41-91
INTEL® SGX INSTRUCTION REFERENCES
TMP_SSP : = 0
IF CPUID.12H.01H:EAX[6] = 1
THEN
IF ( CR4.CET = 0 )
THEN
(* If part does not support CET or CET has not been enabled and enclave requires CET then fail *)
IF ( TMP_SECS.CET_ATTRIBUTES ≠ 0 OR TMP_SECS.CET_LEG_BITMAP_OFFSET ≠ 0 ) #GP(0); FI;
FI;
(* If indirect branch tracking or shadow stacks enabled but CET state save area is not 16B aligned then fail EENTER *)
IF ( TMP_SECS.CET_ATTRIBUTES.SH_STK_EN = 1 OR TMP_SECS.CET_ATTRIBUTES.ENDBR_EN = 1 )
THEN
IF (DS:RBX.OCETSSA is not 16B aligned) #GP(0); FI;
FI;
IF (TMP_SECS.CET_ATTRIBUTES.SH_STK_EN OR TMP_SECS.CET_ATTRIBUTES.ENDBR_EN)
THEN
(* Setup CET state from SECS, note tracker goes to IDLE *)
TMP_IA32_U_CET = TMP_SECS.CET_ATTRIBUTES;
IF (TMP_IA32_U_CET.LEG_IW_EN = 1 AND TMP_IA32_U_CET.ENDBR_EN = 1 )
THEN
TMP_IA32_U_CET := TMP_IA32_U_CET + TMP_SECS.BASEADDR;
TMP_IA32_U_CET := TMP_IA32_U_CET + TMP_SECS.CET_LEG_BITMAP_BASE;
FI;
(* Compute linear address of what will become new CET state save area and cache its PA *)
TMP_CET_SAVE_AREA = DS:RBX.OCETSSA + TMP_SECS.BASEADDR + (DS:RBX.CSSA) * 16
TMP_CET_SAVE_PAGE = TMP_CET_SAVE_AREA & ~0xFFF;
Check the TMP_CET_SAVE_PAGE page is read/write accessible
If fault occurs release locks, abort, and deliver fault
(* Read the EPCM VALID, PENDING, MODIFIED, BLOCKED, and PT fields atomically *)
IF ((DS:TMP_CET_SAVE_PAGE Does NOT RESOLVE TO EPC PAGE) OR
(EPCM(DS:TMP_CET_SAVE_PAGE).VALID = 0) OR
(EPCM(DS:TMP_CET_SAVE_PAGE).PENDING = 1) OR
(EPCM(DS:TMP_CET_SAVE_PAGE).MODIFIED = 1) OR
(EPCM(DS:TMP_CET_SAVE_PAGE).BLOCKED = 1) OR
(EPCM(DS:TMP_CET_SAVE_PAGE).R = 0) OR
(EPCM(DS:TMP_CET_SAVE_PAGE).W = 0) OR
(EPCM(DS:TMP_CET_SAVE_PAGE).ENCLAVEADDRESS ≠ DS:TMP_CET_SAVE_PAGE) OR
(EPCM(DS:TMP_CET_SAVE_PAGE).PT ≠ PT_SS_REST) OR
(EPCM(DS:TMP_CET_SAVE_PAGE).ENCLAVESECS ≠ EPCM(DS:RBX).ENCLAVESECS))
THEN
#PF(DS:TMP_CET_SAVE_PAGE);
FI;
CR_CET_SAVE_AREA_PA := Physical address(DS:TMP_CET_SAVE_AREA)
IF TMP_IA32_U_CET.SH_STK_EN = 1
THEN
TMP_SSP = TCS.PREVSSP;
FI;
FI;
41-92
Vol. 3D
EENTER-Enters an Enclave
INTEL® SGX INSTRUCTION REFERENCES
FI;
CR_ENCLAVE_MODE := 1;
CR_ACTIVE_SECS := TMP_SECS;
CR_ELRANGE := (TMPSECS.BASEADDR, TMP_SECS.SIZE);
(* Save state for possible AEXs *)
CR_TCS_PA := Physical_Address (DS:RBX);
CR_TCS_LA := RBX;
CR_TCS_LA.AEP := RCX;
(* Save the hidden portions of FS and GS *)
CR_SAVE_FS_selector := FS.selector;
CR_SAVE_FS_base := FS.base;
CR_SAVE_FS_limit := FS.limit;
CR_SAVE_FS_access_rights := FS.access_rights;
CR_SAVE_GS_selector := GS.selector;
CR_SAVE_GS_base := GS.base;
CR_SAVE_GS_limit := GS.limit;
CR_SAVE_GS_access_rights := GS.access_rights;
(* If XSAVE is enabled, save XCR0 and replace it with SECS.ATTRIBUTES.XFRM*)
IF (CR4.OSXSAVE = 1)
CR_SAVE_XCR0 := XCR0;
XCR0 := TMP_SECS.ATTRIBUTES.XFRM;
FI;
RCX := RIP;
RIP := TMP_TARGET;
RAX := (DS:RBX).CSSA;
(* Save the outside RSP and RBP so they can be restored on interrupt or EEXIT *)
DS:TMP_SSA.U_RSP := RSP;
DS:TMP_SSA.U_RBP := RBP;
(* Do the FS/GS swap *)
FS.base := TMP_FSBASE;
FS.limit := DS:RBX.FSLIMIT;
FS.type := 0001b;
FS.W := DS[bit 9];
FS.S := 1;
FS.DPL := DS.DPL;
FS.G := 1;
FS.B := 1;
FS.P := 1;
FS.AVL := DS.AVL;
FS.L := DS[bit 21];
FS.unusable := 0;
FS.selector := 0BH;
GS.base := TMP_GSBASE;
GS.limit := DS:RBX.GSLIMIT;
GS.type := 0001b;
GS.W := DS[bit 9];
GS.S := 1;
EENTER-Enters an Enclave
Vol. 3D
41-93
INTEL® SGX INSTRUCTION REFERENCES
GS.DPL := DS.DPL;
GS.G := 1;
GS.B := 1;
GS.P := 1;
GS.AVL := DS.AVL;
GS.L := DS[bit 21];
GS.unusable := 0;
GS.selector := 0BH;
CR_DBGOPTIN := TCS.FLAGS.DBGOPTIN;
Suppress_all_code_breakpoints_that_are_outside_ELRANGE;
IF (CR_DBGOPTIN = 0)
THEN
Suppress_all_code_breakpoints_that_overlap_with_ELRANGE;
CR_SAVE_TF := RFLAGS.TF;
RFLAGS.TF := 0;
Suppress_monitor_trap_flag for the source of the execution of the enclave;
Suppress any pending debug exceptions;
Suppress any pending MTF VM exit;
ELSE
IF RFLAGS.TF = 1
THEN pend a single-step #DB at the end of EENTER; FI;
IF the “monitor trap flag” VM-execution control is set
THEN pend an MTF VM exit at the end of EENTER; FI;
FI;
IF ((CPUID.07H.00H:EDX.CET_IBT = 1) OR (CPUID.07H.00H:ECX.CET_SS = 1)
THEN
(* Save enclosing application CET state into save registers *)
CR_SAVE_IA32_U_CET := IA32_U_CET
(* Setup enclave CET state *)
IF CPUID.07H.00H:ECX.CET_SS = 1
THEN
CR_SAVE_SSP := SSP
SSP := TMP_SSP
FI;
IA32_U_CET := TMP_IA32_U_CET;
FI;
Flush_linear_context;
Allow_front_end_to_begin_fetch_at_new_RIP;
Flags Affected
RFLAGS.TF is cleared on opt-out entry.
41-94
Vol. 3D
EENTER-Enters an Enclave
INTEL® SGX INSTRUCTION REFERENCES
Protected Mode Exceptions
#GP(0)
If DS:RBX is not page aligned.
If the enclave is not initialized.
If part or all of the FS or GS segment specified by TCS is outside the DS segment or not prop-
erly aligned.
If the thread is not in the INACTIVE state.
If CS, DS, ES or SS bases are not all zero.
If executed in enclave mode.
If any reserved field in the TCS FLAG is set.
If the target address is not within the CS segment.
If CR4.OSFXSR = 0.
If CR4.OSXSAVE = 0 and SECS.ATTRIBUTES.XFRM ≠ 3.
If CR4.OSXSAVE = 1and SECS.ATTRIBUTES.XFRM is not a subset of XCR0.
If SECS.ATTRIBUTES.AEXNOTIFY ≠ TCS.FLAGS.AEXNOTIFY and TCS.FLAGS.DBGOPTIN = 0.
#PF(error code)
If a page fault occurs in accessing memory.
If DS:RBX does not point to a valid TCS.
If one or more pages of the current SSA frame are not readable/writable, or do not resolve to
a valid PT_REG EPC page.
64-Bit Mode Exceptions
#GP(0)
If DS:RBX is not page aligned.
If the enclave is not initialized.
If the thread is not in the INACTIVE state.
If CS, DS, ES or SS bases are not all zero.
If executed in enclave mode.
If part or all of the FS or GS segment specified by TCS is outside the DS segment or not prop-
erly aligned.
If the target address is not canonical.
If CR4.OSFXSR = 0.
If CR4.OSXSAVE = 0 and SECS.ATTRIBUTES.XFRM ≠ 3.
If CR4.OSXSAVE = 1and SECS.ATTRIBUTES.XFRM is not a subset of XCR0.
If SECS.ATTRIBUTES.AEXNOTIFY ≠ TCS.FLAGS.AEXNOTIFY and TCS.FLAGS.DBGOPTIN = 0.
#PF(error code)
If a page fault occurs in accessing memory operands.
If DS:RBX does not point to a valid TCS.
If one or more pages of the current SSA frame are not readable/writable, or do not resolve to
a valid PT_REG EPC page.
EENTER-Enters an Enclave
Vol. 3D
41-95
INTEL® SGX INSTRUCTION REFERENCES
EEXIT-Exits an Enclave
Opcode/
Op/En
64/32
CPUID
Description
Instruction
bit Mode
Feature
Support
Flag
EAX = 04H
IR
V/V
SGX1
This leaf function is used to exit an enclave.
ENCLU[EEXIT]
Instruction Operand Encoding
Op/En
EAX
RBX
RCX
IR
EEXIT (In)
Target address outside the enclave (In)
Address of the current AEP (Out)
Description
The ENCLU[EEXIT] instruction exits the currently executing enclave and branches to the location specified in RBX.
RCX receives the current AEP. If RBX is not within the CS (32-bit mode) or is not canonical (64-bit mode) a #GP(0)
results.
EEXIT Memory Parameter Semantics
Target Address
Non-Enclave read and execute access
If RBX specifies an address that is inside the enclave, the instruction will complete normally. The fetch of the next
instruction will occur in non-enclave mode, but will attempt to fetch from inside the enclave. This fetch returns a
fixed data pattern.
If secrets are contained in any registers, it is responsibility of enclave software to clear those registers.
If XCR0 was modified on enclave entry, it is restored to the value it had at the time of the most recent EENTER or
ERESUME.
If the enclave is opt-out, RFLAGS.TF is loaded from the value previously saved on EENTER.
Code and data breakpoints are unsuppressed.
Performance monitoring counters are unsuppressed.
Concurrency Restrictions
Table 41-60. Base Concurrency Restrictions of EEXIT
Base Concurrency Restrictions
Leaf
Parameter
Access
On Conflict
EEXIT
Concurrent
Table 41-61. Additional Concurrency Restrictions of EEXIT
Additional Concurrency Restrictions
vs. EACCEPT, EACCEPTCOPY,
Leaf
Parameter
vs. EADD, EEXTEND, EINIT
vs. ETRACK
EMODPE, EMODPR, EMODT
Access
On Conflict
Access
On Conflict
Access
On Conflict
EEXIT
Concurrent
Concurrent
Concurrent
41-96
Vol. 3D
EEXIT-Exits an Enclave
INTEL® SGX INSTRUCTION REFERENCES
Operation
Temp Variables in EEXIT Operational Flow
Name
Type
Size (Bits)
Description
TMP_RIP
Effective Address
32/64
Saved copy of CRIP for use when creating LBR.
TMP_MODE64 := ((IA32_EFER.LMA = 1) && (CS.L = 1));
IF (TMP_MODE64 = 1)
THEN
IF (RBX is not canonical) THEN #GP(0); FI;
ELSE
IF (RBX > CS limit) THEN #GP(0); FI;
FI;
TMP_RIP := CRIP;
RIP := RBX;
(* Return current AEP in RCX *)
RCX := CR_TCS_PA.AEP;
(* Do the FS/GS swap *)
FS.selector := CR_SAVE_FS.selector;
FS.base := CR_SAVE_FS.base;
FS.limit := CR_SAVE_FS.limit;
FS.access_rights := CR_SAVE_FS.access_rights;
GS.selector := CR_SAVE_GS.selector;
GS.base := CR_SAVE_GS.base;
GS.limit := CR_SAVE_GS.limit;
GS.access_rights := CR_SAVE_GS.access_rights;
(* Restore XCR0 if needed *)
IF (CR4.OSXSAVE = 1)
XCR0 := CR_SAVE__XCR0;
FI;
Unsuppress_all_code_breakpoints_that_are_outside_ELRANGE;
IF (CR_DBGOPTIN = 0)
THEN
UnSuppress_all_code_breakpoints_that_overlap_with_ELRANGE;
Restore suppressed breakpoint matches;
RFLAGS.TF := CR_SAVE_TF;
UnSuppress_montior_trap_flag;
UnSuppress_LBR_Generation;
UnSuppress_performance monitoring_activity;
Restore performance monitoring counter AnyThread demotion to MyThread in enclave back to AnyThread
FI;
IF RFLAGS.TF = 1
THEN Pend Single-Step #DB at the end of EEXIT;
FI;
EEXIT-Exits an Enclave
Vol. 3D
41-97
INTEL® SGX INSTRUCTION REFERENCES
IF the “monitor trap flag” VM-execution control is set
THEN pend a MTF VM exit at the end of EEXIT;
FI;
IF (CPUID.12H.01H:EAX[6] = 1)
THEN
(* Record PREVSSP *)
IF (IA32_U_CET.SH_STK_EN == 1)
THEN CR_TCS_PA.PREVSSP = SSP; FI;
FI;
IF ((CPUID.07H.00H:EDX.CET_IBT = 1) OR (CPUID.07H.00H:ECX.CET_SS = 1)
THEN
(* Restore enclosing app’s CET state from the save registers *)
IA32_U_CET := CR_SAVE_IA32_U_CET;
IF CPUID.07H.00H:ECX.CET_SS = 1
THEN SSP := CR_SAVE_SSP; FI;
(* Update enclosing app’s TRACKER if enclosing app has indirect branch tracking enabled *)
IF (CR4.CET = 1 AND IA32_U_CET.ENDBR_EN = 1)
THEN
IA32_U_CET.TRACKER := WAIT_FOR_ENDBRANCH;
IA32_U_CET.SUPPRESS := 0
FI;
FI;
CR_ENCLAVE_MODE := 0;
CR_TCS_PA.STATE := INACTIVE;
(* Assure consistent translations *)
Flush_linear_context;
Flags Affected
RFLAGS.TF is restored from the value previously saved in EENTER or ERESUME.
Protected Mode Exceptions
#GP(0)
If executed outside an enclave.
If RBX is outside the CS segment.
#PF(error code)
If a page fault occurs in accessing memory.
64-Bit Mode Exceptions
#GP(0)
If executed outside an enclave.
If RBX is not canonical.
#PF(error code)
If a page fault occurs in accessing memory operands.
41-98
Vol. 3D
EEXIT-Exits an Enclave
INTEL® SGX INSTRUCTION REFERENCES
EGETKEY-Retrieves a Cryptographic Key
Opcode/
Op/En
64/32
CPUID
Description
Instruction
bit Mode
Feature
Support
Flag
EAX = 01H
IR
V/V
SGX1
This leaf function retrieves a cryptographic key.
ENCLU[EGETKEY]
Instruction Operand Encoding
Op/En
EAX
RBX
RCX
IR
EGETKEY (In)
Return error code (Out)
Address to a KEYREQUEST (In)
Address of the OUTPUTDATA (In)
Description
The ENCLU[EGETKEY] instruction returns a 128-bit secret key from the processor specific key hierarchy. The
register RBX contains the effective address of a KEYREQUEST structure, which the instruction interprets to deter-
mine the key being requested. The Requesting Keys section below provides a description of the keys that can be
requested. The RCX register contains the effective address where the key will be returned. Both the addresses in
RBX & RCX should be locations inside the enclave.
EGETKEY derives keys using a processor unique value to create a specific key based on a number of possible
inputs. This instruction leaf can only be executed inside an enclave.
EEGETKEY Memory Parameter Semantics
KEYREQUEST
OUTPUTDATA
Enclave read access
Enclave write access
After validating the operands, the instruction determines which key is to be produced and performs the following
actions:
• The instruction assembles the derivation data for the key based on the Table 41-62.
• Computes derived key using the derivation data and package specific value.
• Outputs the calculated key to the address in RCX.
The instruction fails with #GP(0) if the operands are not properly aligned. Successful completion of the instruction
will clear RFLAGS.{ZF, CF, AF, OF, SF, PF}. The instruction returns an error code if the user tries to request a key
based on an invalid CR_CPUSVN or ISVSVN (when the user request is accepted, see the table below), requests a
key for which it has not been granted the attribute to request, or requests a key that is not supported by the hard-
ware. These checks may be performed in any order. Thus, an indication by error number of one cause (for example,
invalid attribute) does not imply that there are not also other errors. Different processors may thus give different
error numbers for the same Enclave. The correctness of software should not rely on the order resulting from the
checks documented in this section. In such cases the ZF flag is set and the corresponding error bit (SGX_IN-
VALID_SVN, SGX_INVALID_ATTRIBUTE, SGX_INVALID_KEYNAME) is set in RAX and the data at the address spec-
ified by RCX is unmodified.
Requesting Keys
The KEYREQUEST structure (see Section 38.18.1) identifies the key to be provided. The Keyrequest.KeyName field
identifies which type of key is requested.
Deriving Keys
Key derivation is based on a combination of the enclave specific values (see Table 41-62) and a processor key.
Depending on the key being requested a field may either be included by definition or the value may be included
from the KeyRequest. A “yes” in Table 41-62 indicates the value for the field is included from its default location,
identified in the source row, and a “request” indicates the values for the field is included from its corresponding
KeyRequest field.
EGETKEY-Retrieves a Cryptographic Key
Vol. 3D
41-99
INTEL® SGX INSTRUCTION REFERENCES
Table 41-62. Key Derivation
Owner
CPU
ISV
ISVEXT
ISVFAM
CONFIG
CONFIGS
Key Name
Attributes
Epoch
SVN
ISV SVN
PRODID
PRODID
ILYID
MRENCLAVE
MRSIGNER
ID
VN
RAND
Key
Y :=
CR_SGX
Y :=
R :=
SECS.
SECS.IS
SECS.IS
SECS.
SECS.
SECS.CO
SECS.CO
Req.
Dependent
SECS.ATTRIBUTES
OWNER
CPUSVN
Req.ISV
ISVID
VEXTPR
VFAMIL
MRENCLAVE
MRSIGNER
NFIGID
NFIGSVN
KEYID
Constant
and
EPOCH
Register;
SVN;
ODID
YID
SECS.MISCSELECT
and
SECS.CET_ATTRIB
UTES;
Source
R := AttribMask &
R :=
SECS.ATTRIBUTES
Req.CPU
and
SVN;
SECS.MISCSELECT
and
SECS.CET_ATTRIB
UTES;
EINITTOKEN
Yes
Request
Yes
Request
Request
Yes
No
No
No
Yes
No
No
Request
Report
Yes
Yes
Yes
Yes
No
No
No
No
Yes
No
Yes
Yes
Request
Seal
Yes
Request
Yes
Request
Request
Request
Request
Request
Request
Request
Request
Request
Request
Provisioning
Yes
Request
No
Request
Request
Yes
No
No
No
Yes
No
No
Yes
Provisioning
Yes
Request
No
Request
Request
Request
Request
Request
No
Yes
Request
Request
Yes
Seal
Keys that permit the specification of a CPU or ISV's code's, or enclave configuration's SVNs have additional require-
ments. The caller may not request a key for an SVN beyond the current CPU, ISV or enclave configuration's SVN,
respectively.
Several keys are access controlled. Access to the Provisioning Key and Provisioning Seal key requires the enclave's
ATTRIBUTES.PROVISIONKEY be set. The EINITTOKEN Key requires ATTRIBUTES.EINITTOKEN_KEY be set and
SECS.MRSIGNER equal IA32_SGXLEPUBKEYHASH.
Some keys are derived based on a hardcode PKCS padding constant (352 byte string):
HARDCODED_PKCS1_5_PADDING[15:0] := 0100H;
HARDCODED_PKCS1_5_PADDING[2655:16] := SignExtend330Byte(-1); // 330 bytes of 0FFH
HARDCODED_PKCS1_5_PADDING[2815:2656] := 2004000501020403650148866009060D30313000H;
The error codes are:
Table 41-63. EGETKEY Return Value in RAX
Error Code (see Table 41-3)
Value
Description
No Error
0
EGETKEY successful.
SGX_INVALID_ATTRIBUTE
The KEYREQUEST contains a KEYNAME for which the enclave is not authorized.
SGX_INVALID_CPUSVN
If KEYREQUEST.CPUSVN is an unsupported platforms CPUSVN value.
SGX_INVALID_ISVSVN
If KEYREQUEST software SVN (ISVSVN or CONFIGSVN) is greater than the
enclave's corresponding SVN.
SGX_INVALID_KEYNAME
If KEYREQUEST.KEYNAME is an unsupported value.
Concurrency Restrictions
Table 41-64. Base Concurrency Restrictions of EGETKEY
Base Concurrency Restrictions
Leaf
Parameter
Access
On Conflict
EGETKEY
KEYREQUEST [DS:RBX]
Concurrent
OUTPUTDATA [DS:RCX]
Concurrent
41-100
Vol.
EGETKEY-Retrieves a Cryptographic Key
INTEL® SGX INSTRUCTION REFERENCES
Table 41-65. Additional Concurrency Restrictions of EGETKEY
Additional Concurrency Restrictions
vs. EACCEPT, EACCEPTCOPY,
Leaf
Parameter
vs. EADD, EEXTEND, EINIT
vs. ETRACK
EMODPE, EMODPR, EMODT
Access
On Conflict
Access
On Conflict
Access
On Conflict
EGETKEY
KEYREQUEST
Concurrent
Concurrent
Concurrent
[DS:RBX]
OUTPUTDATA
Concurrent
Concurrent
Concurrent
[DS:RCX]
Operation
Temp Variables in EGETKEY Operational Flow
Name
Type
Size (Bits)
Description
TMP_CURRENTSECS
Address of the SECS for the currently executing enclave.
TMP_KEYDEPENDENCIES
Temp space for key derivation.
TMP_ATTRIBUTES
128
Temp Space for the calculation of the sealable Attributes.
TMP_ISVEXTPRODID
16 bytes
Temp Space for ISVEXTPRODID.
TMP_ISVPRODID
2 bytes
Temp Space for ISVPRODID.
TMP_ISVFAMILYID
16 bytes
Temp Space for ISVFAMILYID.
TMP_CONFIGID
64 bytes
Temp Space for CONFIGID.
TMP_CONFIGSVN
2 bytes
Temp Space for CONFIGSVN.
TMP_OUTPUTKEY
128
Temp Space for the calculation of the key.
(* Make sure KEYREQUEST is properly aligned and inside the current enclave *)
IF ( (DS:RBX is not 512Byte aligned) or (DS:RBX is not within CR_ELRANGE) )
THEN #GP(0); FI;
(* Make sure DS:RBX is an EPC address and the EPC page is valid *)
IF ( (DS:RBX does not resolve to an EPC address) or (EPCM(DS:RBX).VALID = 0) )
THEN #PF(DS:RBX); FI;
IF (EPCM(DS:RBX).BLOCKED = 1)
THEN #PF(DS:RBX); FI;
(* Check page parameters for correctness *)
IF ( (EPCM(DS:RBX).PT ≠ PT_REG) or (EPCM(DS:RBX).ENCLAVESECS ≠ CR_ACTIVE_SECS) or (EPCM(DS:RBX).PENDING = 1) or
(EPCM(DS:RBX).MODIFIED = 1) or (EPCM(DS:RBX).ENCLAVEADDRESS ≠ (DS:RBX & ~0FFFH) ) or (EPCM(DS:RBX).R = 0) )
THEN #PF(DS:RBX);
FI;
(* Make sure OUTPUTDATA is properly aligned and inside the current enclave *)
IF ( (DS:RCX is not 16Byte aligned) or (DS:RCX is not within CR_ELRANGE) )
THEN #GP(0); FI;
(* Make sure DS:RCX is an EPC address and the EPC page is valid *)
IF ( (DS:RCX does not resolve to an EPC address) or (EPCM(DS:RCX).VALID = 0) )
EGETKEY-Retrieves a Cryptographic Key
Vol. 3D
41-101
INTEL® SGX INSTRUCTION REFERENCES
THEN #PF(DS:RCX); FI;
IF (EPCM(DS:RCX).BLOCKED = 1)
THEN #PF(DS:RCX); FI;
(* Check page parameters for correctness *)
IF ( (EPCM(DS:RCX).PT ≠ PT_REG) or (EPCM(DS:RCX).ENCLAVESECS ≠ CR_ACTIVE_SECS) or (EPCM(DS:RCX).PENDING = 1) or
(EPCM(DS:RCX).MODIFIED = 1) or (EPCM(DS:RCX).ENCLAVEADDRESS ≠ (DS:RCX & ~0FFFH) ) or (EPCM(DS:RCX).W = 0) )
THEN #PF(DS:RCX);
FI;
(* Verify RESERVED spaces in KEYREQUEST are valid *)
IF ( (DS:RBX).RESERVED ≠ 0) or (DS:RBX.KEYPOLICY.RESERVED ≠ 0) )
THEN #GP(0); FI;
TMP_CURRENTSECS := CR_ACTIVE_SECS;
(* Verify that CONFIGSVN & New Policy bits are not used if KSS is not enabled *)
IF ((TMP_CURRENTSECS.ATTRIBUTES.KSS == 0) AND ((DS:RBX.KEYPOLICY & 0x003C ≠ 0) OR (DS:RBX.CONFIGSVN > 0)))
THEN #GP(0); FI;
(* Determine which enclave attributes that must be included in the key. Attributes that must always be include INIT & DEBUG *)
REQUIRED_SEALING_MASK[127:0] := 00000000 00000000 00000000 00000003H;
TMP_ATTRIBUTES := (DS:RBX.ATTRIBUTEMASK | REQUIRED_SEALING_MASK) & TMP_CURRENTSECS.ATTRIBUTES;
(* Compute MISCSELECT fields to be included *)
TMP_MISCSELECT := DS:RBX.MISCMASK & TMP_CURRENTSECS.MISCSELECT
(* Compute CET_ATTRIBUTES fields to be included *)
IF (CPUID.12H.01H:EAX[6] = 1)
THEN TMP_CET_ATTRIBUTES := DS:RBX.CET_ATTRIBUTES_ MASK & TMP_CURRENTSECS.CET_ATTRIBUTES; FI;
TMP_KEYDEPENDENCIES := 0;
CASE (DS:RBX.KEYNAME)
SEAL_KEY:
IF (DS:RBX.CPUSVN is beyond current CPU configuration)
THEN
RFLAGS.ZF := 1;
RAX := SGX_INVALID_CPUSVN;
GOTO EXIT;
FI;
IF (DS:RBX.ISVSVN > TMP_CURRENTSECS.ISVSVN)
THEN
RFLAGS.ZF := 1;
RAX := SGX_INVALID_ISVSVN;
GOTO EXIT;
FI;
IF (DS:RBX.CONFIGSVN > TMP_CURRENTSECS.CONFIGSVN)
THEN
RFLAGS.ZF := 1;
RAX := SGX_INVALID_ISVSVN;
GOTO EXIT;
FI;
(*Include enclave identity?*)
41-102
Vol.
EGETKEY-Retrieves a Cryptographic Key
INTEL® SGX INSTRUCTION REFERENCES
TMP_MRENCLAVE := 0;
IF (DS:RBX.KEYPOLICY.MRENCLAVE = 1)
THEN TMP_MRENCLAVE := TMP_CURRENTSECS.MRENCLAVE;
FI;
(*Include enclave author?*)
TMP_MRSIGNER := 0;
IF (DS:RBX.KEYPOLICY.MRSIGNER = 1)
THEN TMP_MRSIGNER := TMP_CURRENTSECS.MRSIGNER;
FI;
(* Include enclave product family ID? *)
TMP_ISVFAMILYID := 0;
IF (DS:RBX.KEYPOLICY.ISVFAMILYID = 1)
THEN TMP_ISVFAMILYID := TMP_CURRENTSECS.ISVFAMILYID;
FI;
(* Include enclave product ID? *)
TMP_ISVPRODID := 0;
IF (DS:RBX.KEYPOLICY.NOISVPRODID = 0)
TMP_ISVPRODID := TMP_CURRENTSECS.ISVPRODID;
FI;
(* Include enclave Config ID? *)
TMP_CONFIGID := 0;
TMP_CONFIGSVN := 0;
IF (DS:RBX.KEYPOLICY.CONFIGID = 1)
TMP_CONFIGID := TMP_CURRENTSECS.CONFIGID;
TMP_CONFIGSVN := DS:RBX.CONFIGSVN;
FI;
(* Include enclave extended product ID? *)
TMP_ISVEXTPRODID := 0;
IF (DS:RBX.KEYPOLICY.ISVEXTPRODID = 1 )
TMP_ISVEXTPRODID := TMP_CURRENTSECS.ISVEXTPRODID;
FI;
//Determine values key is based on
TMP_KEYDEPENDENCIES.KEYNAME := SEAL_KEY;
TMP_KEYDEPENDENCIES.ISVFAMILYID := TMP_ISVFAMILYID;
TMP_KEYDEPENDENCIES.ISVEXTPRODID := TMP_ISVEXTPRODID;
TMP_KEYDEPENDENCIES.ISVPRODID := TMP_ISVPRODID;
TMP_KEYDEPENDENCIES.ISVSVN := DS:RBX.ISVSVN;
TMP_KEYDEPENDENCIES.SGXOWNEREPOCH := CR_SGXOWNEREPOCH;
TMP_KEYDEPENDENCIES.ATTRIBUTES := TMP_ATTRIBUTES;
TMP_KEYDEPENDENCIES.ATTRIBUTESMASK := DS:RBX.ATTRIBUTEMASK;
TMP_KEYDEPENDENCIES.MRENCLAVE := TMP_MRENCLAVE;
TMP_KEYDEPENDENCIES.MRSIGNER := TMP_MRSIGNER;
TMP_KEYDEPENDENCIES.KEYID := DS:RBX.KEYID;
TMP_KEYDEPENDENCIES.SEAL_KEY_FUSES := CR_SEAL_FUSES;
TMP_KEYDEPENDENCIES.CPUSVN := DS:RBX.CPUSVN;
TMP_KEYDEPENDENCIES.PADDING := TMP_CURRENTSECS.PADDING;
TMP_KEYDEPENDENCIES.MISCSELECT := TMP_MISCSELECT;
TMP_KEYDEPENDENCIES.MISCMASK := ~DS:RBX.MISCMASK;
TMP_KEYDEPENDENCIES.KEYPOLICY := DS:RBX.KEYPOLICY;
TMP_KEYDEPENDENCIES.CONFIGID := TMP_CONFIGID;
EGETKEY-Retrieves a Cryptographic Key
Vol. 3D
41-103
INTEL® SGX INSTRUCTION REFERENCES
TMP_KEYDEPENDENCIES.CONFIGSVN := TMP_CONFIGSVN;
IF CPUID.12H.01H:EAX[6] = 1
THEN
TMP_KEYDEPENDENCIES.CET_ATTRIBUTES := TMP_CET_ATTRIBUTES;
TMP_KEYDEPENDENCIES.CET_ATTRIBUTES _MASK := DS:RBX.CET_ATTRIBUTES _MASK;
FI;
BREAK;
REPORT_KEY:
//Determine values key is based on
TMP_KEYDEPENDENCIES.KEYNAME := REPORT_KEY;
TMP_KEYDEPENDENCIES.ISVFAMILYID := 0;
TMP_KEYDEPENDENCIES.ISVEXTPRODID := 0;
TMP_KEYDEPENDENCIES.ISVPRODID := 0;
TMP_KEYDEPENDENCIES.ISVSVN := 0;
TMP_KEYDEPENDENCIES.SGXOWNEREPOCH := CR_SGXOWNEREPOCH;
TMP_KEYDEPENDENCIES.ATTRIBUTES := TMP_CURRENTSECS.ATTRIBUTES;
TMP_KEYDEPENDENCIES.ATTRIBUTESMASK := 0;
TMP_KEYDEPENDENCIES.MRENCLAVE := TMP_CURRENTSECS.MRENCLAVE;
TMP_KEYDEPENDENCIES.MRSIGNER := 0;
TMP_KEYDEPENDENCIES.KEYID := DS:RBX.KEYID;
TMP_KEYDEPENDENCIES.SEAL_KEY_FUSES := CR_SEAL_FUSES;
TMP_KEYDEPENDENCIES.CPUSVN := CR_CPUSVN;
TMP_KEYDEPENDENCIES.PADDING := HARDCODED_PKCS1_5_PADDING;
TMP_KEYDEPENDENCIES.MISCSELECT := TMP_CURRENTSECS.MISCSELECT;
TMP_KEYDEPENDENCIES.MISCMASK := 0;
TMP_KEYDEPENDENCIES.KEYPOLICY := 0;
TMP_KEYDEPENDENCIES.CONFIGID := TMP_CURRENTSECS.CONFIGID;
TMP_KEYDEPENDENCIES.CONFIGSVN := TMP_CURRENTSECS.CONFIGSVN;
IF (CPUID.12H.01H:EAX[6] = 1)
THEN
TMP_KEYDEPENDENCIES.CET_ATTRIBUTES := TMP_CURRENTSECS.CET_ATTRIBUTES;
TMP_KEYDEPENDENCIES.CET_ATTRIBUTES_MASK := 0;
FI;
BREAK;
EINITTOKEN_KEY:
(* Check ENCLAVE has EINITTOKEN Key capability *)
IF (TMP_CURRENTSECS.ATTRIBUTES.EINITTOKEN_KEY = 0)
THEN
RFLAGS.ZF := 1;
RAX := SGX_INVALID_ATTRIBUTE;
GOTO EXIT;
FI;
IF (DS:RBX.CPUSVN is beyond current CPU configuration)
THEN
RFLAGS.ZF := 1;
RAX := SGX_INVALID_CPUSVN;
GOTO EXIT;
FI;
IF (DS:RBX.ISVSVN > TMP_CURRENTSECS.ISVSVN)
THEN
RFLAGS.ZF := 1;
RAX := SGX_INVALID_ISVSVN;
GOTO EXIT;
FI;
41-104
Vol.
EGETKEY-Retrieves a Cryptographic Key
INTEL® SGX INSTRUCTION REFERENCES
(* Determine values key is based on *)
TMP_KEYDEPENDENCIES.KEYNAME := EINITTOKEN_KEY;
TMP_KEYDEPENDENCIES.ISVFAMILYID := 0;
TMP_KEYDEPENDENCIES.ISVEXTPRODID := 0;
TMP_KEYDEPENDENCIES.ISVPRODID := TMP_CURRENTSECS.ISVPRODID
TMP_KEYDEPENDENCIES.ISVSVN := DS:RBX.ISVSVN;
TMP_KEYDEPENDENCIES.SGXOWNEREPOCH := CR_SGXOWNEREPOCH;
TMP_KEYDEPENDENCIES.ATTRIBUTES := TMP_ATTRIBUTES;
TMP_KEYDEPENDENCIES.ATTRIBUTESMASK := 0;
TMP_KEYDEPENDENCIES.MRENCLAVE := 0;
TMP_KEYDEPENDENCIES.MRSIGNER := TMP_CURRENTSECS.MRSIGNER;
TMP_KEYDEPENDENCIES.KEYID := DS:RBX.KEYID;
TMP_KEYDEPENDENCIES.SEAL_KEY_FUSES := CR_SEAL_FUSES;
TMP_KEYDEPENDENCIES.CPUSVN := DS:RBX.CPUSVN;
TMP_KEYDEPENDENCIES.PADDING := TMP_CURRENTSECS.PADDING;
TMP_KEYDEPENDENCIES.MISCSELECT := TMP_MISCSELECT;
TMP_KEYDEPENDENCIES.MISCMASK := 0;
TMP_KEYDEPENDENCIES.KEYPOLICY := 0;
TMP_KEYDEPENDENCIES.CONFIGID := 0;
TMP_KEYDEPENDENCIES.CONFIGSVN := 0;
IF (CPUID.12H.01H:EAX[6] = 1)
THEN
TMP_KEYDEPENDENCIES.CET_ATTRIBUTES := TMP_CET_ATTRIBUTES;
TMP_KEYDEPENDENCIES.CET_ATTRIBUTES _MASK := 0;
FI;
BREAK;
PROVISION_KEY:
(* Check ENCLAVE has PROVISIONING capability *)
IF (TMP_CURRENTSECS.ATTRIBUTES.PROVISIONKEY = 0)
THEN
RFLAGS.ZF := 1;
RAX := SGX_INVALID_ATTRIBUTE;
GOTO EXIT;
FI;
IF (DS:RBX.CPUSVN is beyond current CPU configuration)
THEN
RFLAGS.ZF := 1;
RAX := SGX_INVALID_CPUSVN;
GOTO EXIT;
FI;
IF (DS:RBX.ISVSVN > TMP_CURRENTSECS.ISVSVN)
THEN
RFLAGS.ZF := 1;
RAX := SGX_INVALID_ISVSVN;
GOTO EXIT;
FI;
(* Determine values key is based on *)
TMP_KEYDEPENDENCIES.KEYNAME := PROVISION_KEY;
TMP_KEYDEPENDENCIES.ISVFAMILYID := 0;
TMP_KEYDEPENDENCIES.ISVEXTPRODID := 0;
TMP_KEYDEPENDENCIES.ISVPRODID := TMP_CURRENTSECS.ISVPRODID;
TMP_KEYDEPENDENCIES.ISVSVN := DS:RBX.ISVSVN;
TMP_KEYDEPENDENCIES.SGXOWNEREPOCH := 0;
TMP_KEYDEPENDENCIES.ATTRIBUTES := TMP_ATTRIBUTES;
EGETKEY-Retrieves a Cryptographic Key
Vol. 3D
41-105
INTEL® SGX INSTRUCTION REFERENCES
TMP_KEYDEPENDENCIES.ATTRIBUTESMASK := DS:RBX.ATTRIBUTEMASK;
TMP_KEYDEPENDENCIES.MRENCLAVE := 0;
TMP_KEYDEPENDENCIES.MRSIGNER := TMP_CURRENTSECS.MRSIGNER;
TMP_KEYDEPENDENCIES.KEYID := 0;
TMP_KEYDEPENDENCIES.SEAL_KEY_FUSES := 0;
TMP_KEYDEPENDENCIES.CPUSVN := DS:RBX.CPUSVN;
TMP_KEYDEPENDENCIES.PADDING := TMP_CURRENTSECS.PADDING;
TMP_KEYDEPENDENCIES.MISCSELECT := TMP_MISCSELECT;
TMP_KEYDEPENDENCIES.MISCMASK := ~DS:RBX.MISCMASK;
TMP_KEYDEPENDENCIES.KEYPOLICY := 0;
TMP_KEYDEPENDENCIES.CONFIGID := 0;
IF (CPUID.12H.01H:EAX[6] = 1)
THEN
TMP_KEYDEPENDENCIES.CET_ATTRIBUTES := TMP_CET_ATTRIBUTES;
TMP_KEYDEPENDENCIES.CET_ATTRIBUTES _MASK := 0;
FI;
BREAK;
PROVISION_SEAL_KEY:
(* Check ENCLAVE has PROVISIONING capability *)
IF (TMP_CURRENTSECS.ATTRIBUTES.PROVISIONKEY = 0)
THEN
RFLAGS.ZF := 1;
RAX := SGX_INVALID_ATTRIBUTE;
GOTO EXIT;
FI;
IF (DS:RBX.CPUSVN is beyond current CPU configuration)
THEN
RFLAGS.ZF := 1;
RAX := SGX_INVALID_CPUSVN;
GOTO EXIT;
FI;
IF (DS:RBX.ISVSVN > TMP_CURRENTSECS.ISVSVN)
THEN
RFLAGS.ZF := 1;
RAX := SGX_INVALID_ISVSVN;
GOTO EXIT;
FI;
(* Include enclave product family ID? *)
TMP_ISVFAMILYID := 0;
IF (DS:RBX.KEYPOLICY.ISVFAMILYID = 1)
THEN TMP_ISVFAMILYID := TMP_CURRENTSECS.ISVFAMILYID;
FI;
(* Include enclave product ID? *)
TMP_ISVPRODID := 0;
IF (DS:RBX.KEYPOLICY.NOISVPRODID = 0)
TMP_ISVPRODID := TMP_CURRENTSECS.ISVPRODID;
FI;
(* Include enclave Config ID? *)
TMP_CONFIGID := 0;
TMP_CONFIGSVN := 0;
IF (DS:RBX.KEYPOLICY.CONFIGID = 1)
TMP_CONFIGID := TMP_CURRENTSECS.CONFIGID;
41-106
Vol.
EGETKEY-Retrieves a Cryptographic Key
INTEL® SGX INSTRUCTION REFERENCES
TMP_CONFIGSVN := DS:RBX.CONFIGSVN;
FI;
(* Include enclave extended product ID? *)
TMP_ISVEXTPRODID := 0;
IF (DS:RBX.KEYPOLICY.ISVEXTPRODID = 1)
TMP_ISVEXTPRODID := TMP_CURRENTSECS.ISVEXTPRODID;
FI;
(* Determine values key is based on *)
TMP_KEYDEPENDENCIES.KEYNAME := PROVISION_SEAL_KEY;
TMP_KEYDEPENDENCIES.ISVFAMILYID := TMP_ISVFAMILYID;
TMP_KEYDEPENDENCIES.ISVEXTPRODID := TMP_ISVEXTPRODID;
TMP_KEYDEPENDENCIES.ISVPRODID := TMP_ISVPRODID;
TMP_KEYDEPENDENCIES.ISVSVN := DS:RBX.ISVSVN;
TMP_KEYDEPENDENCIES.SGXOWNEREPOCH := 0;
TMP_KEYDEPENDENCIES.ATTRIBUTES := TMP_ATTRIBUTES;
TMP_KEYDEPENDENCIES.ATTRIBUTESMASK := DS:RBX.ATTRIBUTEMASK;
TMP_KEYDEPENDENCIES.MRENCLAVE := 0;
TMP_KEYDEPENDENCIES.MRSIGNER := TMP_CURRENTSECS.MRSIGNER;
TMP_KEYDEPENDENCIES.KEYID := 0;
TMP_KEYDEPENDENCIES.SEAL_KEY_FUSES := CR_SEAL_FUSES;
TMP_KEYDEPENDENCIES.CPUSVN := DS:RBX.CPUSVN;
TMP_KEYDEPENDENCIES.PADDING := TMP_CURRENTSECS.PADDING;
TMP_KEYDEPENDENCIES.MISCSELECT := TMP_MISCSELECT;
TMP_KEYDEPENDENCIES.MISCMASK := ~DS:RBX.MISCMASK;
TMP_KEYDEPENDENCIES.KEYPOLICY := DS:RBX.KEYPOLICY;
TMP_KEYDEPENDENCIES.CONFIGID := TMP_CONFIGID;
TMP_KEYDEPENDENCIES.CONFIGSVN := TMP_CONFIGSVN;
IF (CPUID.12H.01H:EAX[6] = 1)
THEN
TMP_KEYDEPENDENCIES.CET_ATTRIBUTES := TMP_CET_ATTRIBUTES;
TMP_KEYDEPENDENCIES.CET_ATTRIBUTES _MASK := 0;
FI;
BREAK;
DEFAULT:
(* The value of KEYNAME is invalid *)
RFLAGS.ZF := 1;
RAX := SGX_INVALID_KEYNAME;
GOTO EXIT:
ESAC;
(* Calculate the final derived key and output to the address in RCX *)
TMP_OUTPUTKEY := derivekey(TMP_KEYDEPENDENCIES);
DS:RCX[15:0] := TMP_OUTPUTKEY;
RAX := 0;
RFLAGS.ZF := 0;
EXIT:
RFLAGS.CF := 0;
RFLAGS.PF := 0;
RFLAGS.AF := 0;
RFLAGS.OF := 0;
RFLAGS.SF := 0;
EGETKEY-Retrieves a Cryptographic Key
Vol. 3D
41-107
INTEL® SGX INSTRUCTION REFERENCES
Flags Affected
ZF is cleared if successful, otherwise ZF is set. CF, PF, AF, OF, SF are cleared.
Protected Mode Exceptions
#GP(0)
If executed outside an enclave.
If a memory operand effective address is outside the current enclave.
If an effective address is not properly aligned.
If an effective address is outside the DS segment limit.
If KEYREQUEST format is invalid.
#PF(error code)
If a page fault occurs in accessing memory.
64-Bit Mode Exceptions
#GP(0)
If executed outside an enclave.
If a memory operand effective address is outside the current enclave.
If an effective address is not properly aligned.
If an effective address is not canonical.
If KEYREQUEST format is invalid.
#PF(error code)
If a page fault occurs in accessing memory operands.
41-108
Vol.
EGETKEY-Retrieves a Cryptographic Key
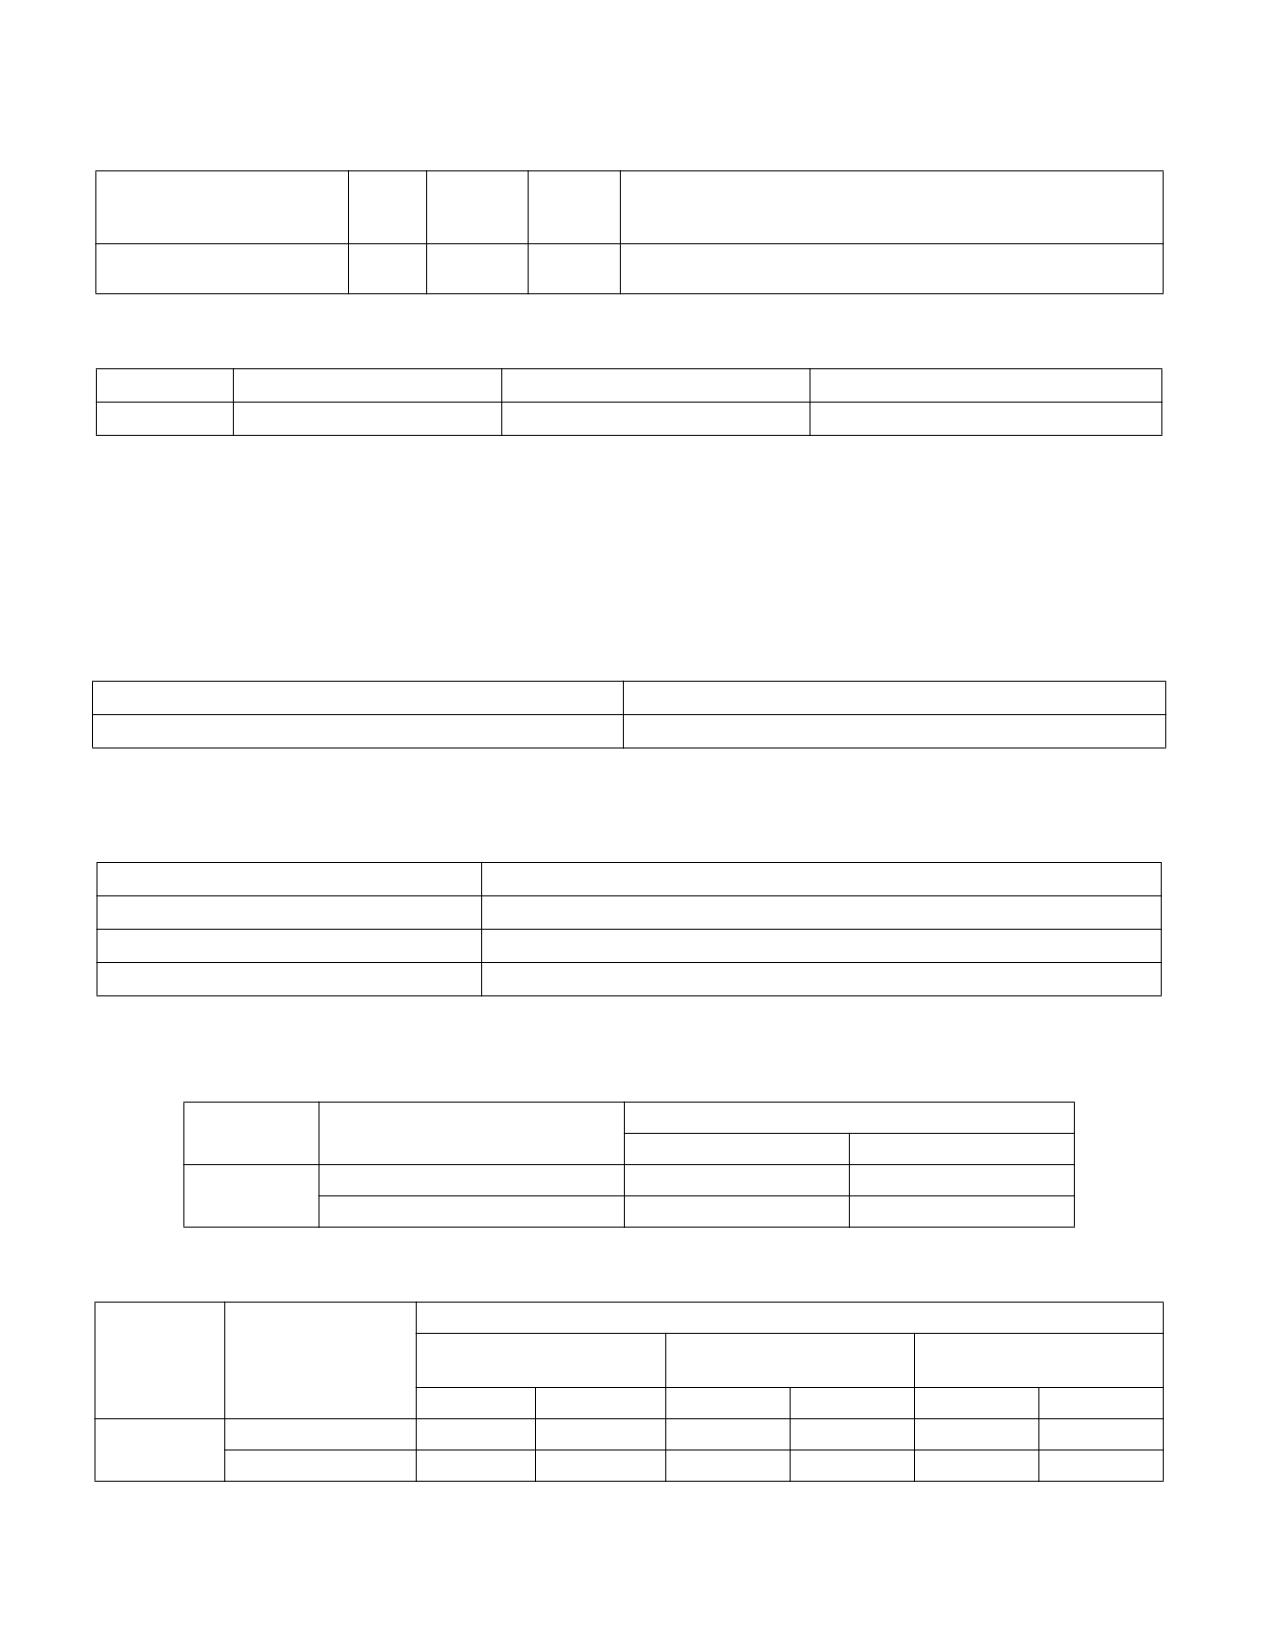
INTEL® SGX INSTRUCTION REFERENCES
EMODPE-Extend an EPC Page Permissions
Opcode/
Op/En
64/32
CPUID
Description
Instruction
bit Mode
Feature
Support
Flag
EAX = 06H
IR
V/V
SGX2
This leaf function extends the access rights of an existing EPC
ENCLU[EMODPE]
page.
Instruction Operand Encoding
Op/En
EAX
RBX
RCX
IR
EMODPE (In)
Address of a SECINFO (In)
Address of the destination EPC page (In)
Description
This leaf function extends the access rights associated with an existing EPC page in the running enclave. THE RWX
bits of the SECINFO parameter are treated as a permissions mask; supplying a value that does not extend the page
permissions will have no effect. This instruction leaf can only be executed when inside the enclave.
RBX contains the effective address of a SECINFO structure while RCX contains the effective address of an EPC
page. The table below provides additional information on the memory parameter of the EMODPE leaf function.
EMODPE Memory Parameter Semantics
SECINFO
EPCPAGE
Read access permitted by Non Enclave
Read access permitted by Enclave
The instruction faults if any of the following:
EMODPE Faulting Conditions
The operands are not properly aligned.
If security attributes of the SECINFO page make the page inaccessible.
The EPC page is locked by another thread.
RBX does not contain an effective address in an EPC page in the running enclave.
The EPC page is not valid.
RCX does not contain an effective address of an EPC page in the running enclave.
SECINFO contains an invalid request.
Concurrency Restrictions
Table 41-66. Base Concurrency Restrictions of EMODPE
Base Concurrency Restrictions
Leaf
Parameter
Access
On Conflict
EMODPE
Target [DS:RCX]
Concurrent
SECINFO [DS:RBX]
Concurrent
Table 41-67. Additional Concurrency Restrictions of EMODPE
Additional Concurrency Restrictions
vs. EACCEPT, EACCEPTCOPY,
Leaf
Parameter
vs. EADD, EEXTEND, EINIT
vs. ETRACK
EMODPE, EMODPR, EMODT
Access
On Conflict
Access
On Conflict
Access
On Conflict
EMODPE
Target [DS:RCX]
Exclusive
#GP
Concurrent
Concurrent
SECINFO [DS:RBX]
Concurrent
Concurrent
Concurrent
EMODPE-Extend an EPC Page Permissions
Vol. 3D
41-109

INTEL® SGX INSTRUCTION REFERENCES
Operation
Temp Variables in EMODPE Operational Flow
Name
Type
Size (bits)
Description
SCRATCH_SECINFO
SECINFO
512
Scratch storage for holding the contents of DS:RBX.
IF (DS:RBX is not 64Byte Aligned)
THEN #GP(0); FI;
IF (DS:RCX is not 4KByte Aligned)
THEN #GP(0); FI;
IF ((DS:RBX is not within CR_ELRANGE) or (DS:RCX is not within CR_ELRANGE) )
THEN #GP(0); FI;
IF (DS:RBX does not resolve within an EPC)
THEN #PF(DS:RBX); FI;
IF (DS:RCX does not resolve within an EPC)
THEN #PF(DS:RCX); FI;
IF ( (EPCM(DS:RBX).VALID = 0) or (EPCM(DS:RBX).R = 0) or (EPCM(DS:RBX).PENDING ≠ 0) or (EPCM(DS:RBX).MODIFIED ≠ 0) or
(EPCM(DS:RBX).BLOCKED ≠ 0) or (EPCM(DS:RBX).PT ≠ PT_REG) or (EPCM(DS:RBX).ENCLAVESECS ≠ CR_ACTIVE_SECS) or
(EPCM(DS:RBX).ENCLAVEADDRESS ≠ (DS:RBX & ~0xFFF)) )
THEN #PF(DS:RBX); FI;
SCRATCH_SECINFO := DS:RBX;
(* Check for misconfigured SECINFO flags*)
IF (SCRATCH_SECINFO reserved fields are not zero )
THEN #GP(0); FI;
(* Check security attributes of the EPC page *)
IF ( (EPCM(DS:RCX).VALID = 0) or (EPCM(DS:RCX).PENDING ≠ 0) or (EPCM(DS:RCX).MODIFIED ≠ 0) or
(EPCM(DS:RCX).BLOCKED ≠ 0) or (EPCM(DS:RCX).PT ≠ PT_REG) or (EPCM(DS:RCX).ENCLAVESECS ≠ CR_ACTIVE_SECS) )
THEN #PF(DS:RCX); FI;
(* Check the EPC page for concurrency *)
IF (EPC page in use by another SGX2 instruction)
THEN #GP(0); FI;
(* Re-Check security attributes of the EPC page *)
IF ( (EPCM(DS:RCX).VALID = 0) or (EPCM(DS:RCX).PENDING ≠ 0) or (EPCM(DS:RCX).MODIFIED ≠ 0) or
(EPCM(DS:RCX).PT ≠ PT_REG) or (EPCM(DS:RCX).ENCLAVESECS ≠ CR_ACTIVE_SECS) or
(EPCM(DS:RCX).ENCLAVEADDRESS ≠ DS:RCX))
THEN #PF(DS:RCX); FI;
(* Check for misconfigured SECINFO flags*)
IF ( (EPCM(DS:RCX).R = 0) and (SCRATCH_SECINFO.FLAGS.R = 0) and (SCRATCH_SECINFO.FLAGS.W ≠ 0) )
THEN #GP(0); FI;
41-110
Vol.
EMODPE-Extend an EPC Page Permissions
INTEL® SGX INSTRUCTION REFERENCES
(* Update EPCM permissions *)
EPCM(DS:RCX).R := EPCM(DS:RCX).R | SCRATCH_SECINFO.FLAGS.R;
EPCM(DS:RCX).W := EPCM(DS:RCX).W | SCRATCH_SECINFO.FLAGS.W;
EPCM(DS:RCX).X := EPCM(DS:RCX).X | SCRATCH_SECINFO.FLAGS.X;
Flags Affected
None
Protected Mode Exceptions
#GP(0)
If executed outside an enclave.
If a memory operand effective address is outside the DS segment limit.
If a memory operand is not properly aligned.
If a memory operand is locked.
#PF(error code)
If a page fault occurs in accessing memory operands.
64-Bit Mode Exceptions
#GP(0)
If executed outside an enclave.
If a memory operand is non-canonical form.
If a memory operand is not properly aligned.
If a memory operand is locked.
#PF(error code)
If a page fault occurs in accessing memory operands.
EMODPE-Extend an EPC Page Permissions
Vol. 3D
41-111
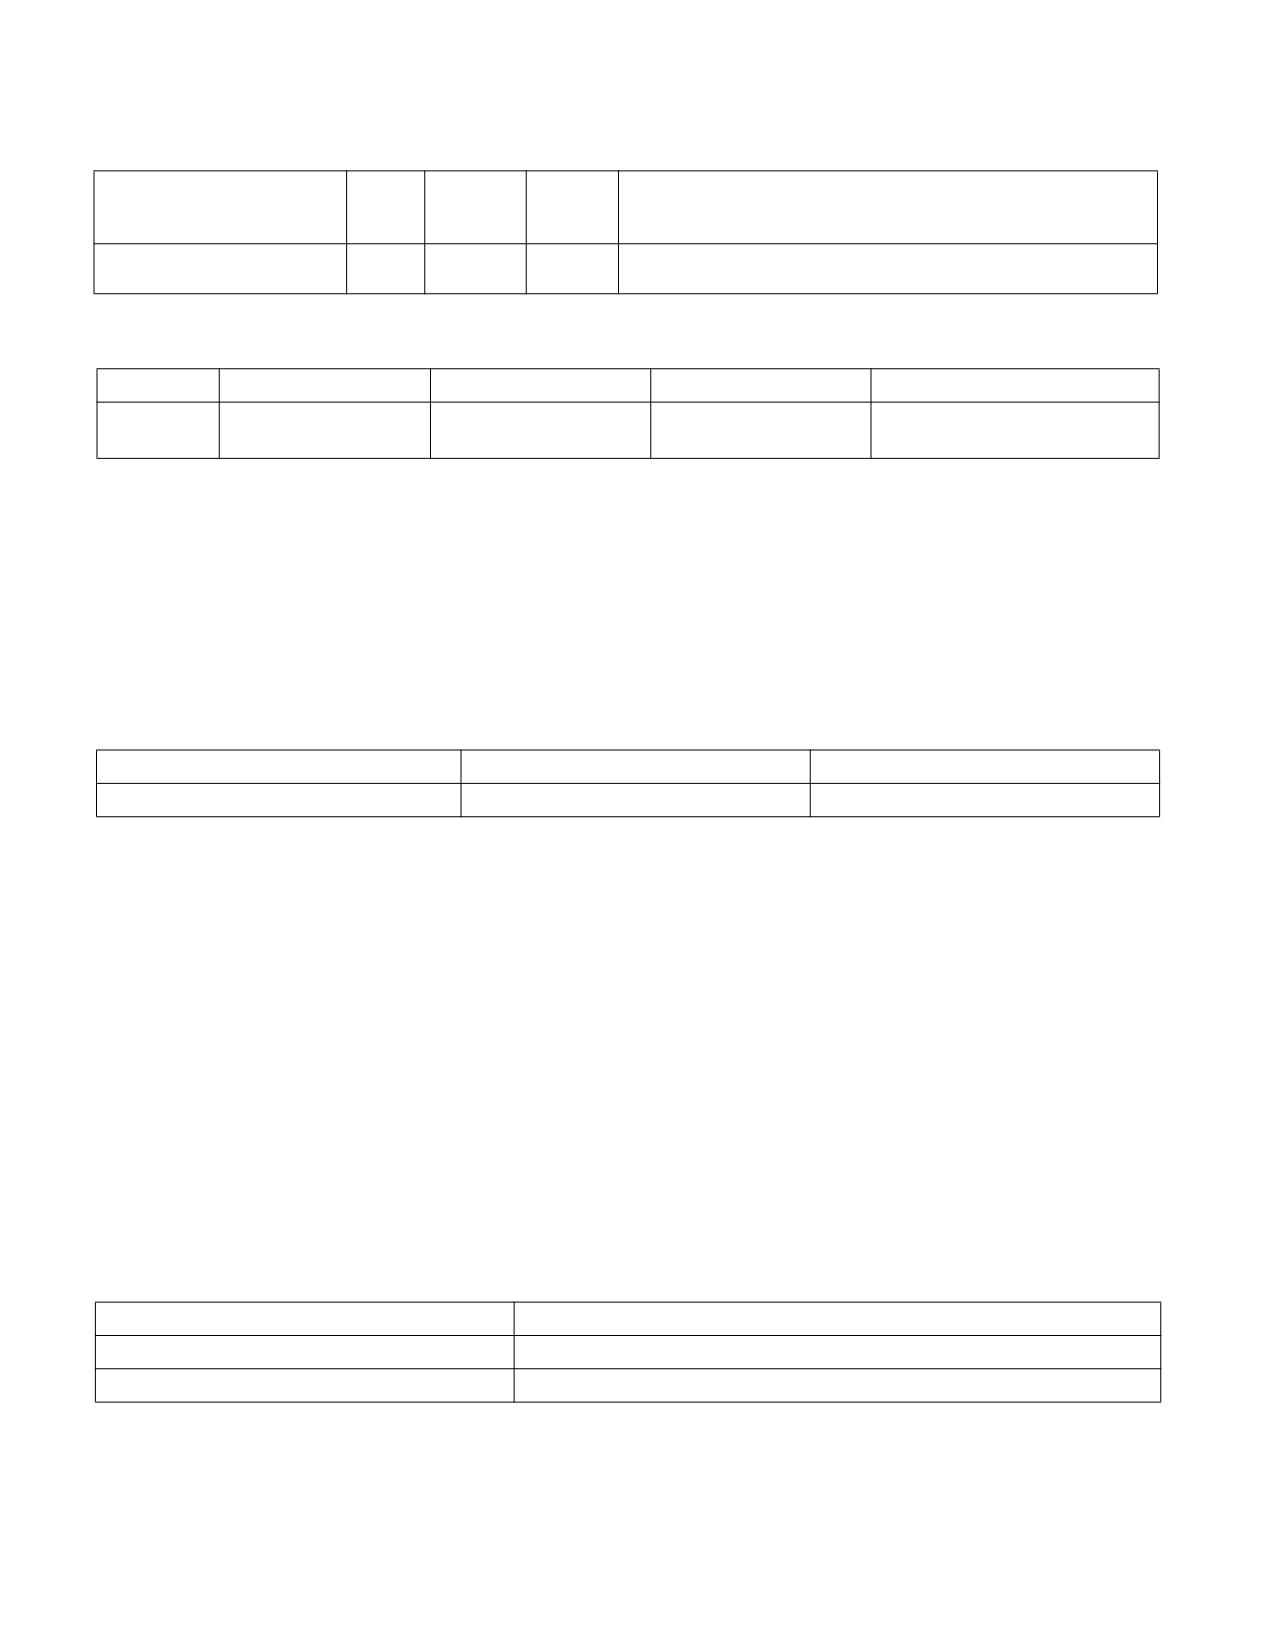
INTEL® SGX INSTRUCTION REFERENCES
EREPORT-Create a Cryptographic Report of the Enclave
Opcode/
Op/En
64/32
CPUID
Description
Instruction
bit Mode
Feature
Support
Flag
EAX = 00H
IR
V/V
SGX1
This leaf function creates a cryptographic report of the enclave.
ENCLU[EREPORT]
Instruction Operand Encoding
Op/En
EAX
RBX
RCX
RDX
Address of TARGETINFO
Address of REPORTDATA
Address where the REPORT is
IR
EREPORT (In)
(In)
(In)
written to in an OUTPUTDATA (In)
Description
This leaf function creates a cryptographic REPORT that describes the contents of the enclave. This instruction leaf
can only be executed when inside the enclave. The cryptographic report can be used by other enclaves to deter-
mine that the enclave is running on the same platform.
RBX contains the effective address of the MRENCLAVE value of the enclave that will authenticate the REPORT
output, using the REPORT key delivered by EGETKEY command for that enclave. RCX contains the effective address
of a 64-byte REPORTDATA structure, which allows the caller of the instruction to associate data with the enclave
from which the instruction is called. RDX contains the address where the REPORT will be output by the instruction.
EREPORT Memory Parameter Semantics
TARGETINFO
REPORTDATA
OUTPUTDATA
Read access by Enclave
Read access by Enclave
Read/Write access by Enclave
This instruction leaf perform the following:
1. Validate the 3 operands (RBX, RCX, RDX) are inside the enclave.
2. Compute a report key for the target enclave, as indicated by the value located in RBX(TARGETINFO).
3. Assemble the enclave SECS data to complete the REPORT structure (including the data provided using the RCX
(REPORTDATA) operand).
4. Computes a cryptographic hash over REPORT structure.
5. Add the computed hash to the REPORT structure.
6. Output the completed REPORT structure to the address in RDX (OUTPUTDATA).
The instruction fails if the operands are not properly aligned.
CR_REPORT_KEYID, used to provide key wearout protection, is populated with a statistically unique value on boot
of the platform by a trusted entity within the SGX TCB.
The instruction faults if any of the following:
EREPORT Faulting Conditions
An effective address not properly aligned.
An memory address does not resolve in an EPC page.
If accessing an invalid EPC page.
If the EPC page is blocked.
May page fault.
41-112
Vol.
EREPORT-Create a Cryptographic Report of the Enclave
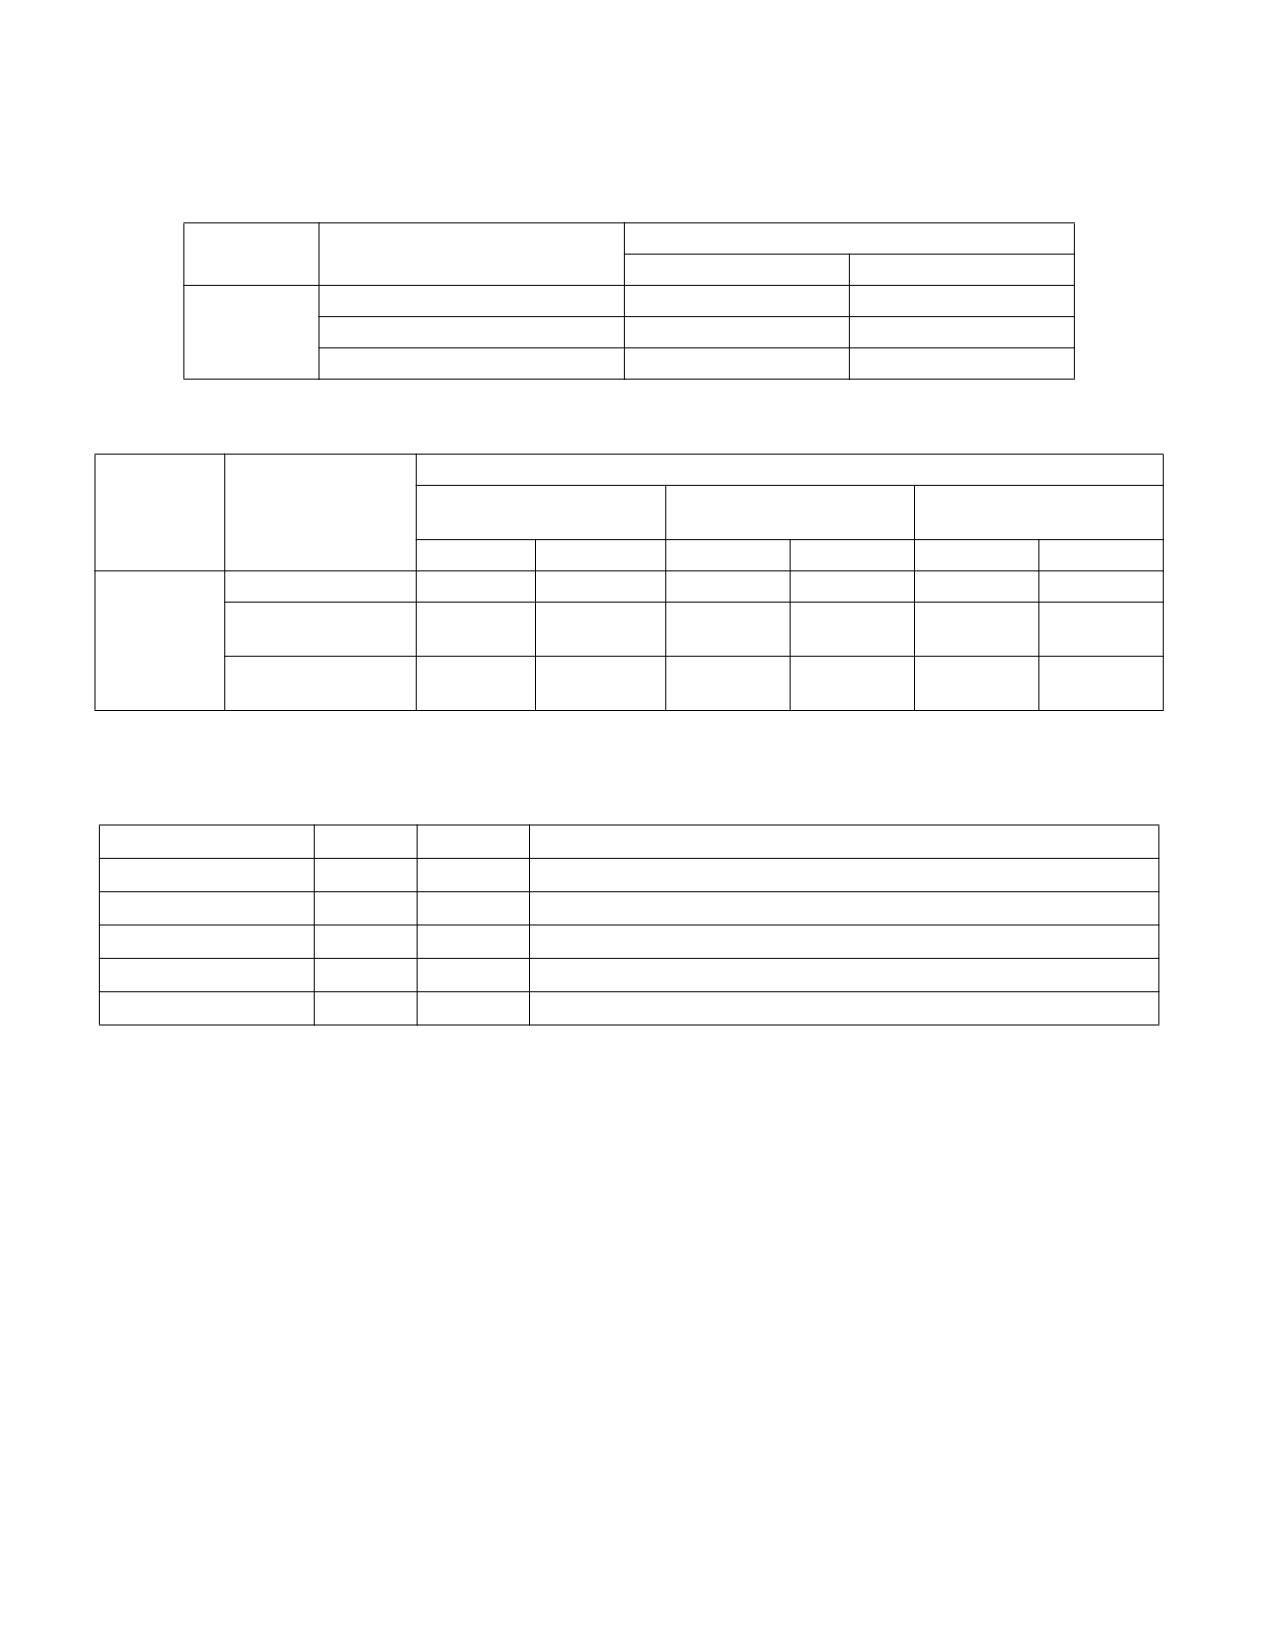
INTEL® SGX INSTRUCTION REFERENCES
Concurrency Restrictions
Table 41-68. Base Concurrency Restrictions of EREPORT
Base Concurrency Restrictions
Leaf
Parameter
Access
On Conflict
EREPORT
TARGETINFO [DS:RBX]
Concurrent
REPORTDATA [DS:RCX]
Concurrent
OUTPUTDATA [DS:RDX]
Concurrent
Table 41-69. Additional Concurrency Restrictions of EREPORT
Additional Concurrency Restrictions
vs. EACCEPT, EACCEPTCOPY,
Leaf
Parameter
vs. EADD, EEXTEND, EINIT
vs. ETRACK
EMODPE, EMODPR, EMODT
Access
On Conflict
Access
On Conflict
Access
On Conflict
EREPORT
TARGETINFO [DS:RBX]
Concurrent
Concurrent
Concurrent
REPORTDATA
Concurrent
Concurrent
Concurrent
[DS:RCX]
OUTPUTDATA
Concurrent
Concurrent
Concurrent
[DS:RDX]
Operation
Temp Variables in EREPORT Operational Flow
Name
Type
Size (bits)
Description
TMP_ATTRIBUTES
32
Physical address of SECS of the enclave to which source operand belongs.
TMP_CURRENTSECS
Address of the SECS for the currently executing enclave.
TMP_KEYDEPENDENCIES
Temp space for key derivation.
TMP_REPORTKEY
128
REPORTKEY generated by the instruction.
TMP_REPORT
3712
TMP_MODE64 := ((IA32_EFER.LMA = 1) && (CS.L = 1));
(* Address verification for TARGETINFO (RBX) *)
IF ( (DS:RBX is not 512Byte Aligned) or (DS:RBX is not within CR_ELRANGE) )
THEN #GP(0); FI;
IF (DS:RBX does not resolve within an EPC)
THEN #PF(DS:RBX); FI;
IF (EPCM(DS:RBX).VALID = 0)
THEN #PF(DS:RBX); FI;
IF (EPCM(DS:RBX).BLOCKED = 1)
THEN #PF(DS:RBX); FI;
(* Check page parameters for correctness *)
IF ( (EPCM(DS:RBX).PT ≠ PT_REG) or (EPCM(DS:RBX).ENCLAVESECS ≠ CR_ACTIVE_SECS) or (EPCM(DS:RBX).PENDING = 1) or
(EPCM(DS:RBX).MODIFIED = 1) or (EPCM(DS:RBX).ENCLAVEADDRESS ≠ (DS:RBX & ~0FFFH) ) or (EPCM(DS:RBX).R = 0) )
EREPORT-Create a Cryptographic Report of the Enclave
Vol. 3D
41-113
INTEL® SGX INSTRUCTION REFERENCES
THEN #PF(DS:RBX);
FI;
(* Verify RESERVED spaces in TARGETINFO are valid *)
IF (DS:RBX.RESERVED != 0)
THEN #GP(0); FI;
(* Address verification for REPORTDATA (RCX) *)
IF ( (DS:RCX is not 128Byte Aligned) or (DS:RCX is not within CR_ELRANGE) )
THEN #GP(0); FI;
IF (DS:RCX does not resolve within an EPC)
THEN #PF(DS:RCX); FI;
IF (EPCM(DS:RCX).VALID = 0)
THEN #PF(DS:RCX); FI;
IF (EPCM(DS:RCX).BLOCKED = 1)
THEN #PF(DS:RCX); FI;
(* Check page parameters for correctness *)
IF ( (EPCM(DS:RCX).PT ≠ PT_REG) or (EPCM(DS:RCX).ENCLAVESECS ≠ CR_ACTIVE_SECS) or (EPCM(DS:RCX).PENDING = 1) or
(EPCM(DS:RCX).MODIFIED = 1) or (EPCM(DS:RCX).ENCLAVEADDRESS ≠ (DS:RCX & ~0FFFH) ) or (EPCM(DS:RCX).R = 0) )
THEN #PF(DS:RCX);
FI;
(* Address verification for OUTPUTDATA (RDX) *)
IF ( (DS:RDX is not 512Byte Aligned) or (DS:RDX is not within CR_ELRANGE) )
THEN #GP(0); FI;
IF (DS:RDX does not resolve within an EPC)
THEN #PF(DS:RDX); FI;
IF (EPCM(DS:RDX).VALID = 0)
THEN #PF(DS:RDX); FI;
IF (EPCM(DS:RDX).BLOCKED = 1)
THEN #PF(DS:RDX); FI;
(* Check page parameters for correctness *)
IF ( (EPCM(DS:RDX).PT ≠ PT_REG) or (EPCM(DS:RDX).ENCLAVESECS ≠ CR_ACTIVE_SECS) or (EPCM(DS:RCX).PENDING = 1) or
(EPCM(DS:RCX).MODIFIED = 1) or (EPCM(DS:RDX).ENCLAVEADDRESS ≠ (DS:RDX & ~0FFFH) ) or (EPCM(DS:RDX).W = 0) )
THEN #PF(DS:RDX);
FI;
(* REPORT MAC needs to be computed over data which cannot be modified *)
TMP_REPORT.CPUSVN := CR_CPUSVN;
TMP_REPORT.ISVFAMILYID := TMP_CURRENTSECS.ISVFAMILYID;
TMP_REPORT.ISVEXTPRODID := TMP_CURRENTSECS.ISVEXTPRODID;
TMP_REPORT.ISVPRODID := TMP_CURRENTSECS.ISVPRODID;
TMP_REPORT.ISVSVN := TMP_CURRENTSECS.ISVSVN;
TMP_REPORT.ATTRIBUTES := TMP_CURRENTSECS.ATTRIBUTES;
TMP_REPORT.REPORTDATA := DS:RCX[511:0];
TMP_REPORT.MRENCLAVE := TMP_CURRENTSECS.MRENCLAVE;
41-114
Vol.
EREPORT-Create a Cryptographic Report of the Enclave
INTEL® SGX INSTRUCTION REFERENCES
TMP_REPORT.MRSIGNER := TMP_CURRENTSECS.MRSIGNER;
TMP_REPORT.MRRESERVED := 0;
TMP_REPORT.KEYID[255:0] := CR_REPORT_KEYID;
TMP_REPORT.MISCSELECT := TMP_CURRENTSECS.MISCSELECT;
TMP_REPORT.CONFIGID := TMP_CURRENTSECS.CONFIGID;
TMP_REPORT.CONFIGSVN := TMP_CURRENTSECS.CONFIGSVN;
IF (CPUID.12H.01H:EAX[6] = 1)
THEN TMP_REPORT.CET_ATTRIBUTES := TMP_CURRENTSECS.CET_ATTRIBUTES; FI;
(* Derive the report key *)
TMP_KEYDEPENDENCIES.KEYNAME := REPORT_KEY;
TMP_KEYDEPENDENCIES.ISVFAMILYID := 0;
TMP_KEYDEPENDENCIES.ISVEXTPRODID := 0;
TMP_KEYDEPENDENCIES.ISVPRODID := 0;
TMP_KEYDEPENDENCIES.ISVSVN := 0;
TMP_KEYDEPENDENCIES.SGXOWNEREPOCH := CR_SGXOWNEREPOCH;
TMP_KEYDEPENDENCIES.ATTRIBUTES := DS:RBX.ATTRIBUTES;
TMP_KEYDEPENDENCIES.ATTRIBUTESMASK := 0;
TMP_KEYDEPENDENCIES.MRENCLAVE := DS:RBX.MEASUREMENT;
TMP_KEYDEPENDENCIES.MRSIGNER := 0;
TMP_KEYDEPENDENCIES.KEYID := TMP_REPORT.KEYID;
TMP_KEYDEPENDENCIES.SEAL_KEY_FUSES := CR_SEAL_FUSES;
TMP_KEYDEPENDENCIES.CPUSVN := CR_CPUSVN;
TMP_KEYDEPENDENCIES.PADDING := TMP_CURRENTSECS.PADDING;
TMP_KEYDEPENDENCIES.MISCSELECT := DS:RBX.MISCSELECT;
TMP_KEYDEPENDENCIES.MISCMASK := 0;
TMP_KEYDEPENDENCIES.KEYPOLICY := 0;
TMP_KEYDEPENDENCIES.CONFIGID := DS:RBX.CONFIGID;
TMP_KEYDEPENDENCIES.CONFIGSVN := DS:RBX.CONFIGSVN;
IF (CPUID.12H.01H:EAX[6] = 1)
THEN
TMP_KEYDEPENDENCIES.CET_ATTRIBUTES := DS:RBX.CET_ATTRIBUTES;
TMP_KEYDEPENDENCIES.CET_ATTRIBUTES _MASK := 0;
FI;
(* Calculate the derived key*)
TMP_REPORTKEY := derivekey(TMP_KEYDEPENDENCIES);
(* call cryptographic CMAC function, CMAC data are not including MAC&KEYID *)
TMP_REPORT.MAC := cmac(TMP_REPORTKEY, TMP_REPORT[3071:0] );
DS:RDX[3455: 0] := TMP_REPORT;
Flags Affected
None
Protected Mode Exceptions
#GP(0)
If executed outside an enclave.
If the address in RCS is outside the DS segment limit.
If a memory operand is not properly aligned.
If a memory operand is not in the current enclave.
#PF(error code)
If a page fault occurs in accessing memory operands.
EREPORT-Create a Cryptographic Report of the Enclave
Vol. 3D
41-115
INTEL® SGX INSTRUCTION REFERENCES
64-Bit Mode Exceptions
#GP(0)
If executed outside an enclave.
If RCX is non-canonical form.
If a memory operand is not properly aligned.
If a memory operand is not in the current enclave.
#PF(error code)
If a page fault occurs in accessing memory operands.
41-116
Vol.
EREPORT-Create a Cryptographic Report of the Enclave
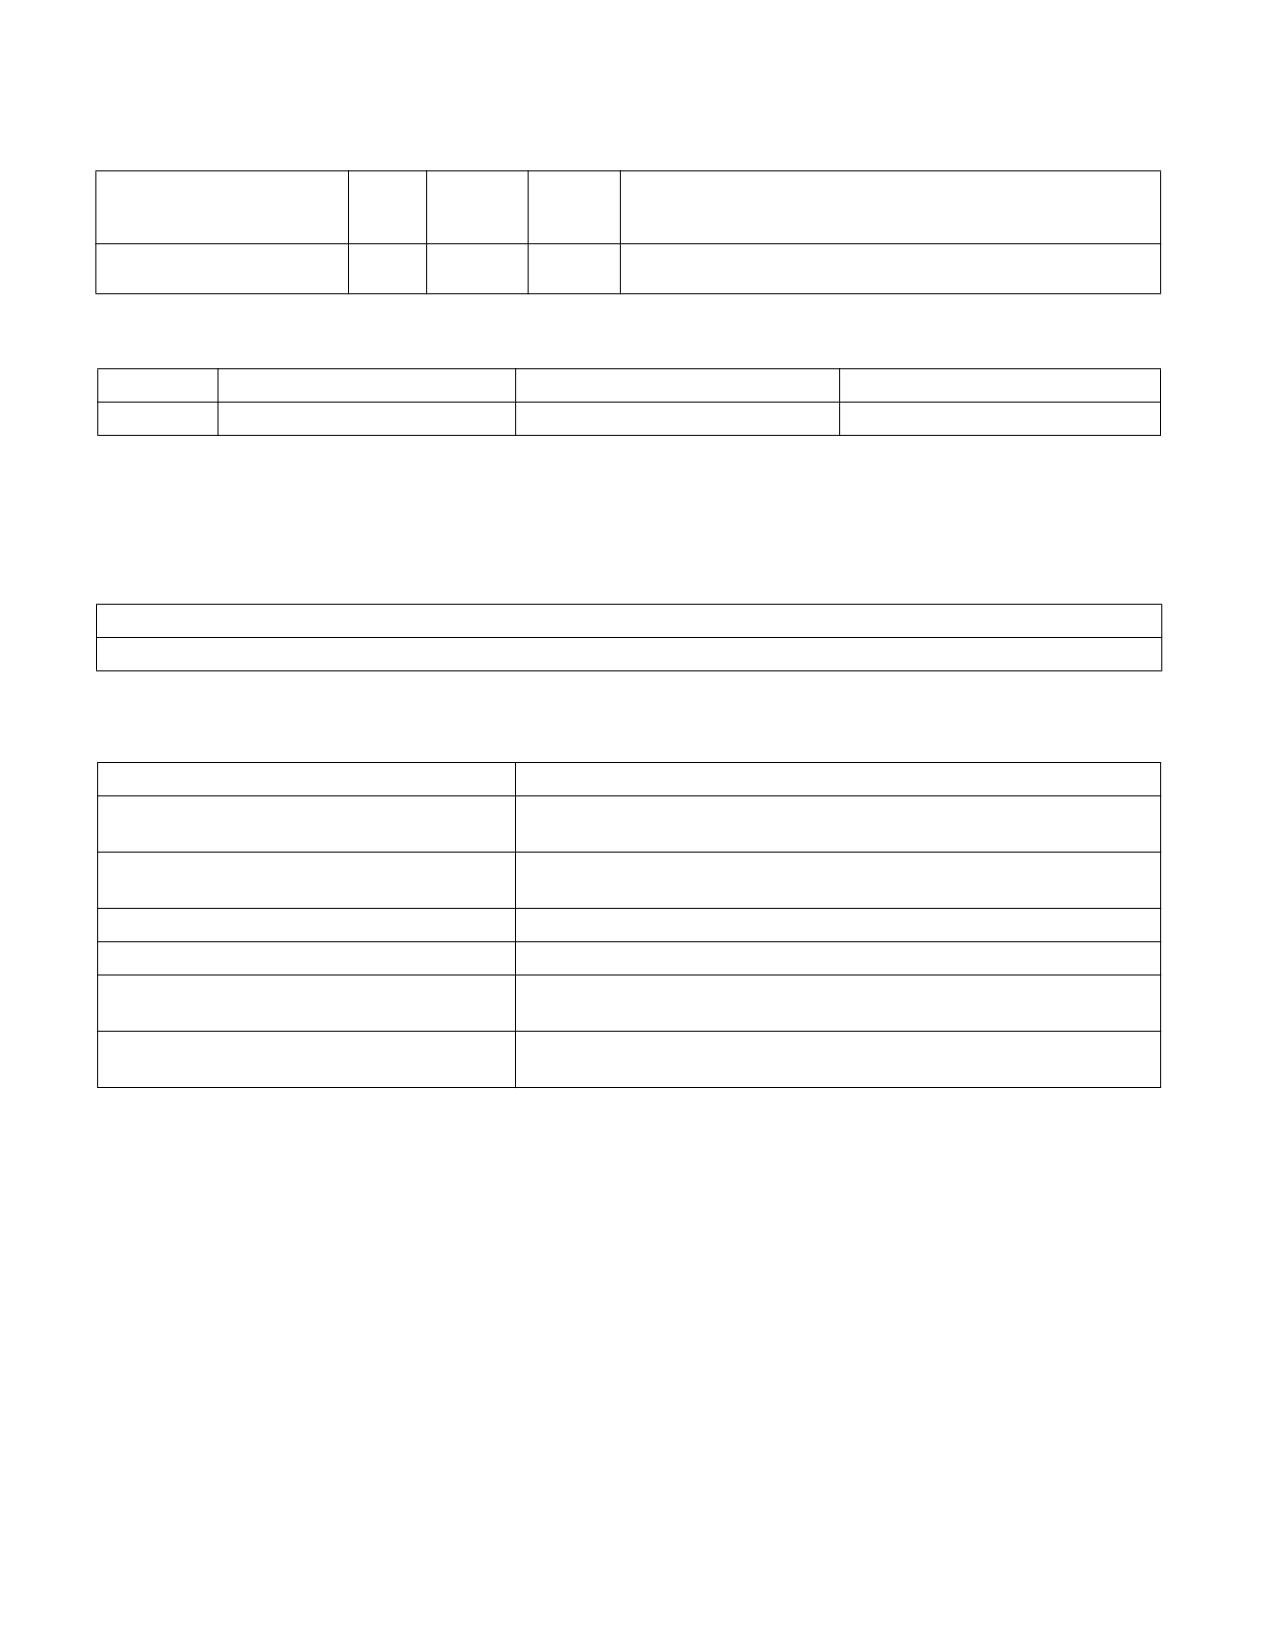
INTEL® SGX INSTRUCTION REFERENCES
ERESUME-Re-Enters an Enclave
Opcode/
Op/En
64/32
CPUID
Description
Instruction
bit Mode
Feature
Support
Flag
EAX = 03H
IR
V/V
SGX1
This leaf function is used to re-enter an enclave after an inter-
ENCLU[ERESUME]
rupt.
Instruction Operand Encoding
Op/En
RAX
RBX
RCX
IR
ERESUME (In)
Address of a TCS (In)
Address of AEP (In)
Description
The ENCLU[ERESUME] instruction resumes execution of an enclave that was interrupted due to an exception or
interrupt, using the machine state previously stored in the SSA.
ERESUME Memory Parameter Semantics
TCS
Enclave read/write access
The instruction faults if any of the following occurs:
Address in RBX is not properly aligned.
Any TCS.FLAGS’s must-be-zero bit is not zero.
TCS pointed to by RBX is not valid or available or
Current 32/64 mode does not match the enclave mode in
locked.
SECS.ATTRIBUTES.MODE64.
The SECS is in use by another enclave.
Either of TCS-specified FS and GS segment is not a subset of the current DS
segment.
Any one of DS, ES, CS, SS is not zero.
If XSAVE available, CR4.OSXSAVE = 0, but SECS.ATTRIBUTES.XFRM ≠ 3.
CR4.OSFXSR ≠ 1.
If CR4.OSXSAVE = 1, SECS.ATTRIBUTES.XFRM is not a subset of XCR0.
Offsets 520-535 of the XSAVE area not 0.
The bit vector stored at offset 512 of the XSAVE area must be a subset of
SECS.ATTRIBUTES.XFRM.
The SSA frame is not valid or in use.
If SECS.ATTRIBUTES.AEXNOTIFY ≠ TCS.FLAGS.AEXNOTIFY and
TCS.FLAGS.DBGOPTIN = 0.
The following operations are performed by ERESUME:
• RSP and RBP are saved in the current SSA frame on EENTER and are automatically restored on EEXIT or an
asynchronous exit due to any Interrupt event.
• The AEP contained in RCX is stored into the TCS for use by AEXs.FS and GS (including hidden portions) are
saved and new values are constructed using TCS.OFSBASE/GSBASE (32 and 64-bit mode) and
TCS.OFSLIMIT/GSLIMIT (32-bit mode only). The resulting segments must be a subset of the DS segment.
• If CR4.OSXSAVE == 1, XCR0 is saved and replaced by SECS.ATTRIBUTES.XFRM. The effect of RFLAGS.TF
depends on whether the enclave entry is opt-in or opt-out (see Section 43.1.2):
- On opt-out entry, TF is saved and cleared (it is restored on EEXIT or AEX). Any attempt to set TF via a POPF
instruction while inside the enclave clears TF (see Section 43.2.5).
- On opt-in entry, a single-step debug exception is pended on the instruction boundary immediately after
EENTER (see Section 43.2.3).
• All code breakpoints that do not overlap with ELRANGE are also suppressed. If the entry is an opt-out entry, all
code and data breakpoints that overlap with the ELRANGE are suppressed.
ERESUME-Re-Enters an Enclave
Vol. 3D
41-117
INTEL® SGX INSTRUCTION REFERENCES
• On opt-out entry, a number of performance monitoring counters and behaviors are modified or suppressed (see
Section 43.2.3):
- All performance monitoring activity on the current thread is suppressed except for incrementing and firing
of FIXED_CTR1 and FIXED_CTR2.
- PEBS is suppressed.
- AnyThread counting on other threads is demoted to MyThread mode and IA32_PERF_GLOBAL_STATUS[60]
on that thread is set.
- If the opt-out entry on a hardware thread results in suppression of any performance monitoring, then the
processor sets IA32_PERF_GLOBAL_STATUS[60] and IA32_PERF_GLOBAL_STATUS[63].
Concurrency Restrictions
Table 41-70. Base Concurrency Restrictions of ERESUME
Base Concurrency Restrictions
Leaf
Parameter
Access
On Conflict
ERESUME
TCS [DS:RBX]
Shared
#GP
Table 41-71. Additional Concurrency Restrictions of ERESUME
Additional Concurrency Restrictions
vs. EACCEPT, EACCEPTCOPY,
Leaf
Parameter
vs. EADD, EEXTEND, EINIT
vs. ETRACK
EMODPE, EMODPR, EMODT
Access
On Conflict
Access
On Conflict
Access
On Conflict
ERESUME
TCS [DS:RBX]
Concurrent
Concurrent
Concurrent
Operation
Temp Variables in ERESUME Operational Flow
Name
Type
Size
Description
TMP_FSBASE
Effective Address
32/64
Proposed base address for FS segment.
TMP_GSBASE
Effective Address
32/64
Proposed base address for FS segment.
TMP_FSLIMIT
Effective Address
32/64
Highest legal address in proposed FS segment.
TMP_GSLIMIT
Effective Address
32/64
Highest legal address in proposed GS segment.
TMP_TARGET
Effective Address
32/64
Address of first instruction inside enclave at which execution is to resume.
TMP_SECS
Effective Address
32/64
Physical address of SECS for this enclave.
TMP_SSA
Effective Address
32/64
Address of current SSA frame.
TMP_XSIZE
integer
64
Size of XSAVE area based on SECS.ATTRIBUTES.XFRM.
TMP_SSA_PAGE
Effective Address
32/64
Pointer used to iterate over the SSA pages in the current frame.
TMP_GPR
Effective Address
32/64
Address of the GPR area within the current SSA frame.
TMP_BRANCH_RECORD
LBR Record
From/to addresses to be pushed onto the LBR stack.
TMP_NOTIFY
Boolean
1
When set to 1, deliver an AEX notification.
TMP_MODE64 := ((IA32_EFER.LMA = 1) && (CS.L = 1));
(* Make sure DS is usable, expand up *)
IF (TMP_MODE64 = 0 and (DS not usable or DS[bits 11:9] != 001B))
41-118
Vol.
ERESUME-Re-Enters an Enclave
INTEL® SGX INSTRUCTION REFERENCES
THEN #GP(0); FI;
(* Check that CS, SS, DS, ES.base is 0 *)
IF (TMP_MODE64 = 0)
THEN
IF(CS.base ≠ 0 or DS.base ≠ 0) #GP(0); FI;
IF(ES usable and ES.base ≠ 0) #GP(0); FI;
IF(SS usable and SS.base ≠ 0) #GP(0); FI;
IF(SS usable and SS.B = 0) #GP(0); FI;
FI;
IF (DS:RBX is not 4KByte Aligned)
THEN #GP(0); FI;
IF (DS:RBX does not resolve within an EPC)
THEN #PF(DS:RBX); FI;
(* Check AEP is canonical*)
IF (TMP_MODE64 = 1 and (CS:RCX is not canonical))
THEN #GP(0); FI;
(* Check concurrency of TCS operation*)
IF (Other Intel SGX instructions are operating on TCS)
THEN #GP(0); FI;
(* TCS verification *)
IF (EPCM(DS:RBX).VALID = 0)
THEN #PF(DS:RBX); FI;
IF (EPCM(DS:RBX).BLOCKED = 1)
THEN #PF(DS:RBX); FI;
IF ((EPCM(DS:RBX).PENDING = 1) or (EPCM(DS:RBX).MODIFIED = 1))
THEN #PF(DS:RBX); FI;
IF ( (EPCM(DS:RBX).ENCLAVEADDRESS ≠ DS:RBX) or (EPCM(DS:RBX).PT ≠ PT_TCS))
THEN #PF(DS:RBX); FI;
IF ( (DS:RBX).OSSA is not 4KByte Aligned)
THEN #GP(0); FI;
(* Check proposed FS and GS *)
IF ( ( (DS:RBX).OFSBASE is not 4KByte Aligned) or ( (DS:RBX).OGSBASE is not 4KByte Aligned))
THEN #GP(0); FI;
(* Get the SECS for the enclave in which the TCS resides *)
TMP_SECS := Address of SECS for TCS;
(* Make sure that the FLAGS field in the TCS does not have any reserved bits set *)
IF ( ( (DS:RBX).FLAGS & FFFFFFFFFFFFFFFCH) ≠ 0)
THEN #GP(0); FI;
(* SECS must exist and enclave must have previously been EINITted *)
IF (the enclave is not already initialized)
ERESUME-Re-Enters an Enclave
Vol. 3D
41-119
INTEL® SGX INSTRUCTION REFERENCES
THEN #GP(0); FI;
(* make sure the logical processor's operating mode matches the enclave *)
IF ( (TMP_MODE64 ≠ TMP_SECS.ATTRIBUTES.MODE64BIT))
THEN #GP(0); FI;
IF (CR4.OSFXSR = 0)
THEN #GP(0); FI;
(* Check for legal values of SECS.ATTRIBUTES.XFRM *)
IF (CR4.OSXSAVE = 0)
THEN
IF (TMP_SECS.ATTRIBUTES.XFRM ≠ 03H) THEN #GP(0); FI;
ELSE
IF ( (TMP_SECS.ATTRIBUTES.XFRM & XCR0) ≠ TMP_SECS.ATTRIBUTES.XFRM) THEN #GP(0); FI;
FI;
IF ( (DS:RBX).CSSA.FLAGS.DBGOPTIN = 0) and (DS:RBX).CSSA.FLAGS.AEXNOTIFY ≠ TMP_SECS.ATTRIBUTES.AEXNOTIFY))
THEN #GP(0); FI;
(* Make sure the SSA contains at least one active frame *)
IF ( (DS:RBX).CSSA = 0)
THEN #GP(0); FI;
(* Compute linear address of SSA frame *)
TMP_SSA := (DS:RBX).OSSA + TMP_SECS.BASEADDR + 4096 * TMP_SECS.SSAFRAMESIZE * ( (DS:RBX).CSSA - 1);
TMP_XSIZE := compute_XSAVE_frame_size(TMP_SECS.ATTRIBUTES.XFRM);
FOR EACH TMP_SSA_PAGE = TMP_SSA to TMP_SSA + TMP_XSIZE
(* Check page is read/write accessible *)
Check that DS:TMP_SSA_PAGE is read/write accessible;
If a fault occurs, release locks, abort and deliver that fault;
IF (DS:TMP_SSA_PAGE does not resolve to EPC page)
THEN #PF(DS:TMP_SSA_PAGE); FI;
IF (EPCM(DS:TMP_SSA_PAGE).VALID = 0)
THEN #PF(DS:TMP_SSA_PAGE); FI;
IF (EPCM(DS:TMP_SSA_PAGE).BLOCKED = 1)
THEN #PF(DS:TMP_SSA_PAGE); FI;
IF ((EPCM(DS:TMP_SSA_PAGE).PENDING = 1) or (EPCM(DS:TMP_SSA_PAGE_.MODIFIED = 1))
THEN #PF(DS:TMP_SSA_PAGE); FI;
IF ( ( EPCM(DS:TMP_SSA_PAGE).ENCLAVEADDRESS ≠ DS:TMPSSA_PAGE) or (EPCM(DS:TMP_SSA_PAGE).PT ≠ PT_REG) or
(EPCM(DS:TMP_SSA_PAGE).ENCLAVESECS ≠ EPCM(DS:RBX).ENCLAVESECS) or
(EPCM(DS:TMP_SSA_PAGE).R = 0) or (EPCM(DS:TMP_SSA_PAGE).W = 0) )
THEN #PF(DS:TMP_SSA_PAGE); FI;
CR_XSAVE_PAGE_n := Physical_Address(DS:TMP_SSA_PAGE);
ENDFOR
(* Compute address of GPR area*)
TMP_GPR := TMP_SSA + 4096 * DS:TMP_SECS.SSAFRAMESIZE - sizeof(GPRSGX_AREA);
Check that DS:TMP_SSA_PAGE is read/write accessible;
If a fault occurs, release locks, abort and deliver that fault;
IF (DS:TMP_GPR does not resolve to EPC page)
THEN #PF(DS:TMP_GPR); FI;
IF (EPCM(DS:TMP_GPR).VALID = 0)
41-120
Vol.
ERESUME-Re-Enters an Enclave
INTEL® SGX INSTRUCTION REFERENCES
THEN #PF(DS:TMP_GPR); FI;
IF (EPCM(DS:TMP_GPR).BLOCKED = 1)
THEN #PF(DS:TMP_GPR); FI;
IF ((EPCM(DS:TMP_GPR).PENDING = 1) or (EPCM(DS:TMP_GPR).MODIFIED = 1))
THEN #PF(DS:TMP_GPR); FI;
IF ( ( EPCM(DS:TMP_GPR).ENCLAVEADDRESS ≠ DS:TMP_GPR) or (EPCM(DS:TMP_GPR).PT ≠ PT_REG) or
(EPCM(DS:TMP_GPR).ENCLAVESECS ≠ EPCM(DS:RBX).ENCLAVESECS) or
(EPCM(DS:TMP_GPR).R = 0) or (EPCM(DS:TMP_GPR).W = 0))
THEN #PF(DS:TMP_GPR); FI;
IF (TMP_MODE64 = 0)
THEN
IF (TMP_GPR + (GPR_SIZE -1) is not in DS segment) THEN #GP(0); FI;
FI;
CR_GPR_PA := Physical_Address (DS: TMP_GPR);
IF ((DS:RBX).FLAGS.AEXNOTIFY = 1) and (DS:TMP_GPR.AEXNOTIFY[0] = 1))
THEN
TMP_NOTIFY := 1;
ELSE
TMP_NOTIFY := 0;
FI;
IF (TMP_NOTIFY = 1)
THEN
(* Make sure the SSA contains at least one more frame *)
IF ((DS:RBX).CSSA ≥ (DS:RBX).NSSA)
THEN #GP(0); FI;
TMP_SSA := TMP_SSA + 4096 * TMP_SECS.SSAFRAMESIZE;
TMP_XSIZE := compute_XSAVE_frame_size(TMP_SECS.ATTRIBUTES.XFRM);
FOR EACH TMP_SSA_PAGE = TMP_SSA to TMP_SSA + TMP_XSIZE
(* Check page is read/write accessible *)
Check that DS:TMP_SSA_PAGE is read/write accessible;
If a fault occurs, release locks, abort and deliver that fault;
IF (DS:TMP_SSA_PAGE does not resolve to EPC page)
THEN #PF(DS:TMP_SSA_PAGE); FI;
IF (EPCM(DS:TMP_SSA_PAGE).VALID = 0)
THEN #PF(DS:TMP_SSA_PAGE); FI;
IF (EPCM(DS:TMP_SSA_PAGE).BLOCKED = 1)
THEN #PF(DS:TMP_SSA_PAGE); FI;
IF ((EPCM(DS:TMP_SSA_PAGE).PENDING = 1) or
(EPCM(DS:TMP_SSA_PAGE).MODIFIED = 1))
THEN #PF(DS:TMP_SSA_PAGE); FI;
IF ((EPCM(DS:TMP_SSA_PAGE).ENCLAVEADDRESS ≠ DS:TMP_SSA_PAGE) or
(EPCM(DS:TMP_SSA_PAGE).PT ≠ PT_REG) or
(EPCM(DS:TMP_SSA_PAGE).ENCLAVESECS ≠ EPCM(DS:RBX).ENCLAVESECS) or
(EPCM(DS:TMP_SSA_PAGE).R = 0) or (EPCM(DS:TMP_SSA_PAGE).W = 0))
THEN #PF(DS:TMP_SSA_PAGE); FI;
CR_XSAVE_PAGE_n := Physical_Address(DS:TMP_SSA_PAGE);
ENDFOR
ERESUME-Re-Enters an Enclave
Vol. 3D
41-121
INTEL® SGX INSTRUCTION REFERENCES
(* Compute address of GPR area*)
TMP_GPR := TMP_SSA + 4096 * DS:TMP_SECS.SSAFRAMESIZE - sizeof(GPRSGX_AREA);
If a fault occurs; release locks, abort and deliver that fault;
IF (DS:TMP_GPR does not resolve to EPC page)
THEN #PF(DS:TMP_GPR); FI;
IF (EPCM(DS:TMP_GPR).VALID = 0)
THEN #PF(DS:TMP_GPR); FI;
IF (EPCM(DS:TMP_GPR).BLOCKED = 1)
THEN #PF(DS:TMP_GPR); FI;
IF ((EPCM(DS:TMP_GPR).PENDING = 1) or (EPCM(DS:TMP_GPR).MODIFIED = 1))
THEN #PF(DS:TMP_GPR); FI;
IF ((EPCM(DS:TMP_GPR).ENCLAVEADDRESS ≠ DS:TMP_GPR) or
(EPCM(DS:TMP_GPR).PT ≠ PT_REG) or
(EPCM(DS:TMP_GPR).ENCLAVESECS EPCM(DS:RBX).ENCLAVESECS) or
(EPCM(DS:TMP_GPR).R = 0) or (EPCM(DS:TMP_GPR).W = 0))
THEN #PF(DS:TMP_GPR); FI;
IF (TMP_MODE64 = 0)
THEN
IF (TMP_GPR + (GPR_SIZE -1) is not in DS segment) THEN #GP(0); FI;
FI;
CR_GPR_PA := Physical_Address (DS: TMP_GPR);
TMP_TARGET := (DS:RBX).OENTRY + TMP_SECS.BASEADDR;
ELSE
TMP_TARGET := (DS:TMP_GPR).RIP;
FI;
IF (TMP_MODE64 = 1)
THEN
IF (TMP_TARGET is not canonical) THEN #GP(0); FI;
ELSE
IF (TMP_TARGET > CS limit) THEN #GP(0); FI;
FI;
(* Check proposed FS/GS segments fall within DS *)
IF (TMP_MODE64 = 0)
THEN
TMP_FSBASE := (DS:RBX).OFSBASE + TMP_SECS.BASEADDR;
TMP_FSLIMIT := (DS:RBX).OFSBASE + TMP_SECS.BASEADDR + (DS:RBX).FSLIMIT;
TMP_GSBASE := (DS:RBX).OGSBASE + TMP_SECS.BASEADDR;
TMP_GSLIMIT := (DS:RBX).OGSBASE + TMP_SECS.BASEADDR + (DS:RBX).GSLIMIT;
(* if FS wrap-around, make sure DS has no holes*)
IF (TMP_FSLIMIT < TMP_FSBASE)
THEN
IF (DS.limit < 4GB) THEN #GP(0); FI;
ELSE
IF (TMP_FSLIMIT > DS.limit) THEN #GP(0); FI;
FI;
(* if GS wrap-around, make sure DS has no holes*)
IF (TMP_GSLIMIT < TMP_GSBASE)
THEN
41-122
Vol.
ERESUME-Re-Enters an Enclave
INTEL® SGX INSTRUCTION REFERENCES
IF (DS.limit < 4GB) THEN #GP(0); FI;
ELSE
IF (TMP_GSLIMIT > DS.limit) THEN #GP(0); FI;
FI;
ELSE
IF (TMP_NOTIFY = 1)
THEN
TMP_FSBASE := (DS:RBX).OFSBASE + TMP_SECS.BASEADDR;
TMP_GSBASE := (DS:RBX).OGSBASE + TMP_SECS.BASEADDR;
ELSE
TMP_FSBASE := DS:TMP_GPR.FSBASE;
TMP_GSBASE := DS:TMP_GPR.GSBASE;
FI;
IF ((TMP_FSBASE is not canonical) or (TMP_GSBASE is not canonical))
THEN #GP(0); FI;
FI;
(* Ensure the enclave is not already active and this thread is the only one using the TCS*)
IF (DS:RBX.STATE = ACTIVE))
THEN #GP(0); FI;
TMP_IA32_U_CET := 0
TMP_SSP := 0
IF (CPUID.12H.01H:EAX[6] = 1)
THEN
IF ( CR4.CET = 0 )
THEN
(* If part does not support CET or CET has not been enabled and enclave requires CET then fail *)
IF (TMP_SECS.CET_ATTRIBUTES ≠ 0 OR TMP_SECS.CET_LEG_BITMAP_OFFSET ≠ 0) #GP(0); FI;
FI;
(* If indirect branch tracking or shadow stacks enabled but CET state save area is not 16B aligned then fail ERESUME *)
IF (TMP_SECS.CET_ATTRIBUTES.SH_STK_EN = 1 OR TMP_SECS.CET_ATTRIBUTES.ENDBR_EN = 1)
THEN
IF (DS:RBX.OCETSSA is not 16B aligned) #GP(0); FI;
FI;
IF (TMP_SECS.CET_ATTRIBUTES.SH_STK_EN OR TMP_SECS.CET_ATTRIBUTES.ENDBR_EN)
THEN
(* Setup CET state from SECS, note tracker goes to IDLE *)
TMP_IA32_U_CET = TMP_SECS.CET_ATTRIBUTES;
IF (TMP_IA32_U_CET.LEG_IW_EN = 1 AND TMP_IA32_U_CET.ENDBR_EN = 1)
THEN
TMP_IA32_U_CET := TMP_IA32_U_CET + TMP_SECS.BASEADDR;
TMP_IA32_U_CET := TMP_IA32_U_CET + TMP_SECS.CET_LEG_BITMAP_BASE;
FI;
(* Compute linear address of what will become new CET state save area and cache its PA *)
IF (TMP_NOTIFY = 1)
THEN
TMP_CET_SAVE_AREA = DS:RBX.OCETSSA + TMP_SECS.BASEADDR + (DS:RBX.CSSA) * 16;
ELSE
TMP_CET_SAVE_AREA = DS:RBX.OCETSSA + TMP_SECS.BASEADDR + (DS:RBX.CSSA - 1) * 16;
FI;
ERESUME-Re-Enters an Enclave
Vol. 3D
41-123
INTEL® SGX INSTRUCTION REFERENCES
TMP_CET_SAVE_PAGE = TMP_CET_SAVE_AREA & ~0xFFF;
Check the TMP_CET_SAVE_PAGE page is read/write accessible
If fault occurs release locks, abort and deliver fault
(* read the EPCM VALID, PENDING, MODIFIED, BLOCKED and PT fields atomically *)
IF ((DS:TMP_CET_SAVE_PAGE Does NOT RESOLVE TO EPC PAGE) OR
(EPCM(DS:TMP_CET_SAVE_PAGE).VALID = 0) OR
(EPCM(DS:TMP_CET_SAVE_PAGE).PENDING = 1) OR
(EPCM(DS:TMP_CET_SAVE_PAGE).MODIFIED = 1) OR
(EPCM(DS:TMP_CET_SAVE_PAGE).BLOCKED = 1) OR
(EPCM(DS:TMP_CET_SAVE_PAGE).R = 0) OR
(EPCM(DS:TMP_CET_SAVE_PAGE).W = 0) OR
(EPCM(DS:TMP_CET_SAVE_PAGE).ENCLAVEADDRESS ≠ DS:TMP_CET_SAVE_PAGE) OR
(EPCM(DS:TMP_CET_SAVE_PAGE).PT ≠ PT_SS_REST) OR
(EPCM(DS:TMP_CET_SAVE_PAGE).ENCLAVESECS ≠ EPCM(DS:RBX).ENCLAVESECS))
THEN
#PF(DS:TMP_CET_SAVE_PAGE);
FI;
CR_CET_SAVE_AREA_PA := Physical address(DS:TMP_CET_SAVE_AREA)
IF (TMP_NOTIFY = 1)
THEN
IF TMP_IA32_U_CET.SH_STK_EN = 1
THEN TMP_SSP = TCS.PREVSSP; FI;
ELSE
TMP_SSP = CR_CET_SAVE_AREA_PA.SSP
TMP_IA32_U_CET.TRACKER = CR_CET_SAVE_AREA_PA.TRACKER;
TMP_IA32_U_CET.SUPPRESS = CR_CET_SAVE_AREA_PA.SUPPRESS;
IF ( (TMP_MODE64 = 1 AND TMP_SSP is not canonical) OR
(TMP_MODE64 = 0 AND (TMP_SSP & 0xFFFFFFFF00000000) ≠ 0) OR
(TMP_SSP is not 4 byte aligned) OR
(TMP_IA32_U_CET.TRACKER = WAIT_FOR_ENDBRANCH AND TMP_IA32_U_CET.SUPPRESS = 1) OR
(CR_CET_SAVE_AREA_PA.Reserved ≠ 0) ) #GP(0); FI;
FI;
FI;
FI;
IF (TMP_NOTIFY = 0)
THEN
(* SECS.ATTRIBUTES.XFRM selects the features to be saved. *)
(* CR_XSAVE_PAGE_n: A list of 1 or more physical address of pages that contain the XSAVE area. *)
XRSTOR(TMP_MODE64, SECS.ATTRIBUTES.XFRM, CR_XSAVE_PAGE_n);
IF (XRSTOR failed with #GP)
THEN
DS:RBX.STATE := INACTIVE;
#GP(0);
FI;
FI;
CR_ENCLAVE_MODE := 1;
CR_ACTIVE_SECS := TMP_SECS;
CR_ELRANGE := (TMP_SECS.BASEADDR, TMP_SECS.SIZE);
41-124
Vol.
ERESUME-Re-Enters an Enclave
INTEL® SGX INSTRUCTION REFERENCES
(* Save sate for possible AEXs *)
CR_TCS_PA := Physical_Address (DS:RBX);
CR_TCS_LA := RBX;
CR_TCS_LA.AEP := RCX;
(* Save the hidden portions of FS and GS *)
CR_SAVE_FS_selector := FS.selector;
CR_SAVE_FS_base := FS.base;
CR_SAVE_FS_limit := FS.limit;
CR_SAVE_FS_access_rights := FS.access_rights;
CR_SAVE_GS_selector := GS.selector;
CR_SAVE_GS_base := GS.base;
CR_SAVE_GS_limit := GS.limit;
CR_SAVE_GS_access_rights := GS.access_rights;
IF (TMP_NOTIFY = 1)
THEN
(* If XSAVE is enabled, save XCR0 and replace it with SECS.ATTRIBUTES.XFRM*)
IF (CR4.OSXSAVE = 1)
THEN
CR_SAVE_XCR0 := XCR0;
XCR0 := TMP_SECS.ATTRIBUTES.XFRM;
FI;
FI;
RIP := TMP_TARGET;
IF (TMP_NOTIFY = 1)
THEN
RCX := RIP;
RAX := (DS:RBX).CSSA;
(* Save the outside RSP and RBP so they can be restored on interrupt or EEXIT *)
DS:TMP_SSA.U_RSP := RSP;
DS:TMP_SSA.U_RBP := RBP;
ELSE
Restore_GPRs from DS:TMP_GPR;
(*Restore the RFLAGS values from SSA*)
RFLAGS.CF := DS:TMP_GPR.RFLAGS.CF;
RFLAGS.PF := DS:TMP_GPR.RFLAGS.PF;
RFLAGS.AF := DS:TMP_GPR.RFLAGS.AF;
RFLAGS.ZF := DS:TMP_GPR.RFLAGS.ZF;
RFLAGS.SF := DS:TMP_GPR.RFLAGS.SF;
RFLAGS.DF := DS:TMP_GPR.RFLAGS.DF;
RFLAGS.OF := DS:TMP_GPR.RFLAGS.OF;
RFLAGS.NT := DS:TMP_GPR.RFLAGS.NT;
RFLAGS.AC := DS:TMP_GPR.RFLAGS.AC;
RFLAGS.ID := DS:TMP_GPR.RFLAGS.ID;
RFLAGS.RF := DS:TMP_GPR.RFLAGS.RF;
RFLAGS.VM := 0;
IF (RFLAGS.IOPL = 3)
THEN RFLAGS.IF := DS:TMP_GPR.RFLAGS.IF; FI;
IF (TCS.FLAGS.OPTIN = 0)
ERESUME-Re-Enters an Enclave
Vol. 3D
41-125
INTEL® SGX INSTRUCTION REFERENCES
THEN RFLAGS.TF := 0; FI;
(* If XSAVE is enabled, save XCR0 and replace it with SECS.ATTRIBUTES.XFRM*)
IF (CR4.OSXSAVE = 1)
THEN
CR_SAVE_XCR0 := XCR0;
XCR0 := TMP_SECS.ATTRIBUTES.XFRM;
FI;
(* Pop the SSA stack*)
(DS:RBX).CSSA := (DS:RBX).CSSA -1;
FI;
(* Do the FS/GS swap *)
FS.base := TMP_FSBASE;
FS.limit := DS:RBX.FSLIMIT;
FS.type := 0001b;
FS.W := DS[bit 9];
FS.S := 1;
FS.DPL := DS.DPL;
FS.G := 1;
FS.B := 1;
FS.P := 1;
FS.AVL := DS.AVL;
FS.L := DS[bit 21];
FS.unusable := 0;
FS.selector := 0BH;
GS.base := TMP_GSBASE;
GS.limit := DS:RBX.GSLIMIT;
GS.type := 0001b;
GS.W := DS[bit 9];
GS.S := 1;
GS.DPL := DS.DPL;
GS.G := 1;
GS.B := 1;
GS.P := 1;
GS.AVL := DS.AVL;
GS.L := DS[bit 21];
GS.unusable := 0;
GS.selector := 0BH;
CR_DBGOPTIN := TCS.FLAGS.DBGOPTIN;
Suppress all code breakpoints that are outside ELRANGE;
IF (CR_DBGOPTIN = 0)
THEN
Suppress all code breakpoints that overlap with ELRANGE;
CR_SAVE_TF := RFLAGS.TF;
RFLAGS.TF := 0;
Suppress any MTF VM exits during execution of the enclave;
Clear all pending debug exceptions;
Clear any pending MTF VM exit;
ELSE
41-126
Vol.
ERESUME-Re-Enters an Enclave
INTEL® SGX INSTRUCTION REFERENCES
IF (TMP_NOTIFY = 1)
THEN
IF RFLAGS.TF = 1
THEN pend a single-step #DB at the end of ERESUME; FI;
IF the “monitor trap flag” VM-execution control is set
THEN pend an MTF VM exit at the end of ERESUME; FI;
ELSE
Clear all pending debug exceptions;
Clear pending MTF VM exits;
FI;
FI;
IF ((CPUID.07H.00H:EDX.CET_IBT = 1) OR (CPUID.07H.00H:ECX.CET_SS = 1)
THEN
(* Save enclosing application CET state into save registers *)
CR_SAVE_IA32_U_CET := IA32_U_CET
(* Setup enclave CET state *)
IF CPUID.07H.00H:ECX.CET_SS = 1
THEN
CR_SAVE_SSP := SSP
SSP := TMP_SSP;
FI;
IA32_U_CET := TMP_IA32_U_CET;
FI;
(* Assure consistent translations *)
Flush_linear_context;
Clear_Monitor_FSM;
Allow_front_end_to_begin_fetch_at_new_RIP;
Flags Affected
RFLAGS.TF is cleared on opt-out entry
Protected Mode Exceptions
#GP(0)
If DS:RBX is not page aligned.
If the enclave is not initialized.
If the thread is not in the INACTIVE state.
If CS, DS, ES or SS bases are not all zero.
If executed in enclave mode.
If part or all of the FS or GS segment specified by TCS is outside the DS segment.
If any reserved field in the TCS FLAG is set.
If the target address is not within the CS segment.
If CR4.OSFXSR = 0.
If CR4.OSXSAVE = 0 and SECS.ATTRIBUTES.XFRM ≠ 3.
If CR4.OSXSAVE = 1and SECS.ATTRIBUTES.XFRM is not a subset of XCR0.
If SECS.ATTRIBUTES.AEXNOTIFY ≠ TCS.FLAGS.AEXNOTIFY and TCS.FLAGS.DBGOPTIN = 0.
#PF(error code)
If a page fault occurs in accessing memory.
If DS:RBX does not point to a valid TCS.
If one or more pages of the current SSA frame are not readable/writable, or do not resolve to
a valid PT_REG EPC page.
ERESUME-Re-Enters an Enclave
Vol. 3D
41-127
INTEL® SGX INSTRUCTION REFERENCES
64-Bit Mode Exceptions
#GP(0)
If DS:RBX is not page aligned.
If the enclave is not initialized.
If the thread is not in the INACTIVE state.
If CS, DS, ES or SS bases are not all zero.
If executed in enclave mode.
If part or all of the FS or GS segment specified by TCS is outside the DS segment.
If any reserved field in the TCS FLAG is set.
If the target address is not canonical.
If CR4.OSFXSR = 0.
If CR4.OSXSAVE = 0 and SECS.ATTRIBUTES.XFRM ≠ 3.
If CR4.OSXSAVE = 1and SECS.ATTRIBUTES.XFRM is not a subset of XCR0.
If SECS.ATTRIBUTES.AEXNOTIFY ≠ TCS.FLAGS.AEXNOTIFY and TCS.FLAGS.DBGOPTIN = 0.
#PF(error code)
If a page fault occurs in accessing memory operands.
If DS:RBX does not point to a valid TCS.
If one or more pages of the current SSA frame are not readable/writable, or do not resolve to
a valid PT_REG EPC page.
41-128
Vol.
ERESUME-Re-Enters an Enclave
INTEL® SGX INSTRUCTION REFERENCES
EVERIFYREPORT2-Verify a Cryptographic Report Created by SEAMREPORT
Opcode/
Op/En
64/32
CPUID
Description
Instruction
bit Mode
Feature
Support
Flag
EAX = 08H
IR
V/V
EVERI-
This leaf function verifies a cryptographic report of the TD. RBX
ENCLU[EVERIFYREPORT2]
FYRE-
holds the address of a REPORTMACSTRUCT.
PORT2
EVERIFYREPORT2 Instruction Layout
Instruction
EAX
RBX
RCX
RDX
REPORTMACSTRUCT
EVERIFYREPORT2
08H
effective address.
Description
This instruction verifies REPORTMACSTRUCT, which is part of a cryptographic report of a TDX trust domain (TD),
created by execution of the SEAMREPORT operation of the SEAMOPS instruction (see Section 35.5 of Intel® 64 and
IA-32 Architectures Software Developer’s Manual, Volume 3C).
REPORTMACSTRUCT is a 256-byte data structure at the effective address provided in RBX. The first 224 bytes
contain information about the TD being reported, including the value of CR_CPUSVN when the report was created
(bytes 31:16). The last 32 bytes (bytes 255:224) contain the 256-bit MAC value. The MAC is computed over the
first 224 bytes using HMAC-SHA-256 algorithm with CR_REPORT_MAC_KEY (see Section 41.1.4).
For more details about REPORTMACSTRUCT, see Section “Report MAC Structure (REPORTMACSTRUCT)” in the
Intel® Architecture Instruction Set Extensions and Future Features Programming Reference.
Operation
Temp Variables in EVERIFYREPORT2 Operational Flow
Name
Type
Size
Description
TMP_CURRENTSECS
Effective Address
32/64 Bytes
The address of the SECS for the currently executing enclave.
TMP_REPORTMACSTRUCT
REPORTMACSTRUCT
256 Bytes
Cryptographic Report of the TEE.
TMP_MAC
MAC
32 Bytes
MAC over REPORT calculated by instruction.
RFLAGS.ZF,CF,PF,AF,OF,SF := 0;
RAX := 0;
(* verify REPORTMACSTRUCT address (RBX) *)
IF ((DS:RBX is not 4KB-aligned) or (DS:RBX is not within CR_ELRANGE))
THEN #GP(0); FI;
(* check page parameters for correctness *)
IF (DS:RBX does not resolve within an EPC)
or (EPCM(DS:RBX).VALID = 0)
or (EPCM(DS:RBX).BLOCKED = 1))
or (EPCM(DS:RBX).PENDING = 1)
or (EPCM(DS:RBX).MODIFIED = 1)
or (EPCM(DS:RBX).PT ≠ PT_REG)
or (EPCM(DS:RBX).ENCLAVESECS ≠ CR_ACTIVE_SECS)
or (EPCM(DS:RBX).ENCLAVEADDRESS ≠ (DS:RBX & ~0FFFH))
or (EPCM(DS:RBX).R = 0))
EVERIFYREPORT2-Verify a Cryptographic Report Created by SEAMREPORT
Vol. 3D
41-129
INTEL® SGX INSTRUCTION REFERENCES
THEN #PF(DS:RBX);
FI;
(* get a temp copy of input REPORTMACSTRUCT *)
TMP_REPORTMACSTRUCT[255:0B] = DS:RBX[255:0B];
(* verify CPUSVN *)
IF (TMP_REPORTMACSTRUCT[31:16B] ≠ CR_CPUSVN)
THEN
RFLAGS.ZF := 1;
RAX := SGX_INVALID_CPUSVN;
GOTO ERROR_EXIT;
FI;
(* verify MAC *)
TMP_MAC = HMAC-SHA256(CR_REPORT_MAC_KEY, TMP_REPORTMACSTRUCT[223:0B], 224);
IF (TMP_REPORTMACSTRUCT[255:224B] ≠ TMP_MAC)
THEN
RFLAGS.ZF := 1;
RAX := SGX_INVALID_REPORTMACSTRUCT;
FI;
ERROR_EXIT:
Flags Affected
None.
Protected Mode Exceptions
#GP(0)
If a memory operand effective address is outside the DS segment limit.
If DS segment is unusable.
If a memory operand is not properly aligned.
#PF(fault-code)
If a page fault occurs in accessing memory operands, including EPCM-induced faults.
64-Bit Mode Exceptions
#GP(0)
If a memory address is in a non-canonical form.
If a memory operand is not properly aligned.
#PF(fault-code)
If a page fault occurs in accessing memory operands, including EPCM-induced faults.
Error Codes
• SGX_INVALID_CPUSVN (32): If REPOSRTMACSTRUC.CPUSVN is an unsupported value.
• SGX_INVALID_REPORTMACSTRUCT (28): MAC verification failed.
41-130
Vol.
EVERIFYREPORT2-Verify a Cryptographic Report Created by SEAMREPORT
INTEL® SGX INTERACTIONS WITH IA32 AND INTEL® 64 ARCHITECTURE
CHAPTER 42
INTEL® SGX INTERACTIONS WITH IA32 AND INTEL® 64 ARCHITECTURE
Intel® SGX provides Intel® Architecture with a collection of enclave instructions for creating protected execution
environments on processors supporting IA32 and Intel® 64 architectures. These Intel SGX instructions are
designed to work with legacy software and the various IA32 and Intel 64 modes of operation.
42.1
INTEL® SGX AVAILABILITY IN VARIOUS PROCESSOR MODES
The Intel SGX extensions (see Table 37-1) are available only when the processor is executing in protected mode of
operation. Additionally, the extensions are not available in System Management Mode (SMM) of operation or in
Virtual 8086 (VM86) mode of operation. Finally, all leaf functions of ENCLU and ENCLS require CR0.PG enabled.
The exact details of exceptions resulting from illegal modes and their priority are listed in the reference pages of
ENCLS and ENCLU.
42.2
IA32_FEATURE_CONTROL
IA32_FEATURE_CONTROL MSR provides two new bits related to two aspects of Intel SGX: using the instruction
extensions and launch control configuration.
42.2.1 Availability of Intel SGX
IA32_FEATURE_CONTROL[bit 18] allows BIOS to control the availability of Intel SGX extensions. For Intel SGX
extensions to be available on a logical processor, bit 18 in the IA32_FEATURE_CONTROL MSR on that logical
processor must be set, and IA32_FEATURE_CONTROL MSR on that logical processor must be locked (bit 0 must be
set). See Section 37.7.1 for additional details. OS is expected to examine the value of bit 18 prior to enabling Intel
SGX on the thread, as the settings of bit 18 is not reflected by CPUID.
42.2.2 Intel SGX Launch Control Configuration
The IA32_SGXLEPUBKEYHASHn MSRs used to configure authorized launch enclaves' MRSIGNER digest value. They
are present on logical processors that support the collection of SGX1 leaf functions (i.e., CPUID.12H.00H:EAX[0] =
1) and that CPUID.07H.00H:ECX[30] = 1. IA32_FEATURE_CONTROL[bit 17] allows to BIOS to enable write access
to these MSRs. If IA32_FEATURE_CONTROL.LE_WR (bit 17) is set to 1 and IA32_FEATURE_CONTROL is locked on
that logical processor, IA32_SGXLEPUBKEYHASH MSRs on that logical processor are writeable. If this bit 17 is not
set or IA32_FEATURE_CONTROL is not locked, IA32_SGXLEPUBKEYHASH MSRs are read only. See Section 39.1.4
for additional details.
42.3
INTERACTIONS WITH SEGMENTATION
42.3.1 Scope of Interaction
Intel SGX extensions are available only when the processor is executing in a protected mode operation (see Section
42.1 for Intel SGX availability in various processor modes). Enclaves abide by all the segmentation policies set up
by the OS, but they can be more restrictive than the OS.
Intel SGX interacts with segmentation at two levels:
• The Intel SGX instruction (see the enclave instruction in Table 37-1).
Vol. 3D
42-1
INTEL® SGX INTERACTIONS WITH IA32 AND INTEL® 64 ARCHITECTURE
• While executing inside an enclave (legacy instructions and enclave instructions permitted inside an enclave).
42.3.2 Interactions of Intel® SGX Instructions with Segment, Operand, and Addressing
Prefixes
All the memory operands used by the Intel SGX instructions are interpreted as offsets within the data segment
(DS). The segment-override prefix on Intel SGX instructions is ignored.
Operand size is fixed for each enclave instruction. The operand-size prefix is reserved, and results in a #UD excep-
tion if used.
All address sizes are determined by the operating mode of the processor. The address-size prefix is ignored. This
implies that while operating in 64-bit mode of operation, the address size is always 64 bits, and while operating in
32-bit mode of operation, the address size is always 32 bits. Additionally, when operating in 16-bit addressing,
memory operands used by enclave instructions use 32 bit addressing; the value of CS.D is ignored.
42.3.3 Interaction of Intel® SGX Instructions with Segmentation
All leaf functions of ENCLU and ENCLS instructions require that the DS segment be usable, and be an expand-up
segment. Failing this check results in generation of a #GP(0) exception.
The Intel SGX leaf functions used for entering the enclave (ENCLU[EENTER] and ENCLU[ERESUME]) operate as
follows:
• All usable segment registers except for FS and GS have a zero base.
• The contents of the FS/GS segment registers (including the hidden portion) is saved in the processor.
• New FS and GS values compatible with enclave security are loaded from the TCS
• The linear ranges and access rights available under the newly-loaded FS and GS must abide to OS policies by
ensuring they are subsets of the linear-address range and access rights available for the DS segment.
• The CS segment mode (64-bit, compatible, or 32 bit modes) must be consistent with the segment mode for
which the enclave was created, as indicated by the SECS.ATTRIBUTES.MODE64 bit, and that the CPL of the
logical processor is 3
An exit from the enclave either via ENCLU[EEXIT] or via an AEX restores the saved values of FS/GS segment regis-
ters.
42.3.4 Interactions of Enclave Execution with Segmentation
During the course of execution, enclave code abides by all segmentation policies as dictated by IA32 and Intel 64
Architectures, and generates appropriate exceptions on violations.
Additionally, any attempt by software executing inside an enclave to modify the processor's segmentation state
(e.g., via MOV seg register, POP seg register, LDS, far jump, etc; excluding WRFSBASE/WRGSBASE) results in the
generation of a #UD. See Section 39.6.1 for more information.
Upon enclave entry via the EENTER leaf function, FS is loaded from the (TCS.OFSBASE + SECS.BASEADDR) and
TCS.FSLIMIT fields and GS is loaded from the (TCS.OGSBASE + SECS.BASEADDR) and TCS.GSLIMIT fields.
Execution of WRFSBASE and WRGSBASE from inside a 64-bit enclave is allowed. The processor will save the new
values into the current SSA frame on an asynchronous exit (AEX) and restore them back on enclave entry via
ENCLU[ERESUME] instruction.
42.4
INTERACTIONS WITH PAGING
Intel SGX instructions are available only when the processor is executing in a protected mode of operation. Addi-
tionally, all Intel SGX leaf functions except for EDBGRD and EDBGWR are available only if paging is enabled. Any
attempt to execute these leaf functions with paging disabled results in an invalid-opcode exception (#UD). As with
42-2
Vol. 3D
INTEL® SGX INTERACTIONS WITH IA32 AND INTEL® 64 ARCHITECTURE
segmentation, enclaves abide by all the paging policies set up by the OS, but they can be more restrictive than the
OS.
All the memory operands passed into Intel SGX instructions are interpreted as offsets within the DS segment, and
the linear addresses generated by combining these offsets with DS segment register are subject to paging-based
access control if paging is enabled at the time of the execution of the leaf function.
Since the ENCLU[EENTER] and ENCLU[ERESUME] can only be executed when paging is enabled, and since paging
cannot be disabled by software running inside an enclave (recall that enclaves always run with CPL = 3), enclave
execution is always subject to paging-based access control. The Intel SGX access control itself is implemented as
an extension to the existing paging modes. See Section 38.5 for details.
Execution of Intel SGX instructions may set accessed and dirty flags on accesses to EPC pages that do not fault
even if the instruction later causes a fault for some other reason.
42.5
INTERACTIONS WITH VMX
Intel SGX functionality (including SGX1 and SGX2) can be made available to software running in either VMX root
operation or VMX non-root operation, as long as the processor is using a legal mode of operation (see Section
42.1).
A VMM has the flexibility to configure a VMCS to permit a guest to use any subset of the ENCLS leaf functions. Avail-
ability of the ENCLU leaf functions in VMX non-root operation has the same requirement as ENCLU leaf functions
outside of a virtualized environment.
Details of the VMCS control to allow VMM to configure support of Intel SGX in VMX non-root operation is described
in Section 42.5.1
42.5.1 VMM Controls to Configure Guest Support of Intel® SGX
Intel SGX capabilities are primarily exposed to the software via the CPUID instruction. VMMs can virtualize CPUID
instruction to expose/hide this capability to/from guests.
Some of Intel SGX resources are exposed/controlled via model-specific registers (see Section 37.7). VMMs can
virtualize these MSRs for the guests using the MSR bitmaps referenced by pointers in the VMCS.
The VMM can partition the Enclave Page Cache, and assign various partitions to (a subset of) its guests via the
usual memory-virtualization techniques such as paging or the extended page table mechanism (EPT).
The VMM can set the “enable ENCLS exiting” VM-execution controls to cause a VM exit when the ENCLS instruction
is executed in VMX non-root operation. If the “enable ENCLS exiting” control is 0, all of the ENCLS leaf functions are
permitted in VMX non-root operation. If the “enable ENCLS exiting” control is 1, execution of ENCLS leaf functions
in VMX non-root operation is governed by consulting the bits in a new 64-bit VM-execution control field called the
ENCLS-exiting bitmap (Each bit in the bitmap corresponds to an ENCLS leaf function with an EAX value that is iden-
tical to the bit’s position). When bits in the “ENCLS-exiting bitmap” are set, attempts to execute the corresponding
ENCLS leaf functions in VMX non-root operation causes VM exits. The checking for these VM exits occurs immedi-
ately after checking that CPL = 0.
42.5.2 Interactions with the Extended Page Table Mechanism (EPT)
Intel SGX instructions are fully compatible with the extended page-table mechanism (EPT; see Section 31.3).
All the memory operands passed into Intel SGX instructions are interpreted as offsets within the DS segment, and
the linear addresses generated by combining these offsets with DS segment register are subject to paging and EPT.
As with paging, enclaves abide by all the policies set up by the VMM.
The Intel SGX access control itself is implemented as an extension to paging and EPT, and may be more restrictive.
See Section 42.4 for details of this extension.
An execution of an Intel SGX instruction may set accessed and dirty flags for EPT (when enabled; see Section
31.3.5) on accesses to EPC pages that do not fault or cause VM exits even if the instruction later causes a fault or
VM exit for some other reason.
Vol. 3D
42-3
INTEL® SGX INTERACTIONS WITH IA32 AND INTEL® 64 ARCHITECTURE
42.5.3 Interactions with APIC Virtualization
This section applies to Intel SGX in VMX non-root operation when the “virtualize APIC accesses” VM-execution
control is 1.
A memory access by an enclave instruction that implicitly uses a cached physical address is never checked for
overlap with the APIC-access page. Such accesses never cause APIC-access VM exits and are never redirected to
the virtual-APIC page. Implicit memory accesses can only be made to the SECS, the TCS, or the SSA of an enclave
(see Section 38.5.3.2).
An explicit Enclave Access (a linear memory access which is either from within an enclave into its ELRANGE, or an
access by an Intel SGX instruction that is expected to be in the EPC) that overlaps with the APIC-access page
causes a #PF exception (APIC page is expected to be outside of EPC).
Non-Enclave accesses made either by an Intel SGX instruction or by a logical processor inside an enclave to an
address that without SGX would have caused redirection to the virtual-APIC page instead cause an APIC-access
VM exit.
Other than implicit accesses made by Intel SGX instructions, guest-physical and physical accesses are not consid-
ered “enclave accesses”; consequently, such accesses result in undefined behavior if these accesses eventually
reach EPC. This applies to any non-enclave physical accesses.
While a logical processor is executing inside an enclave, an attempt to execute an instruction outside of ELRANGE
results in a #GP(0), even if the linear address would translate to a physical address that overlaps the APIC-access
page.
42.6
INTEL® SGX INTERACTIONS WITH ARCHITECTURALLY-VISIBLE EVENTS
All architecturally visible events (exceptions, interrupts, SMI, NMI, INIT, VM exit) can be detected while inside an
enclave and will cause an asynchronous enclave exit if they are not blocked. Additionally, INT3, and the SignalTX-
TMsg[SENTER] (i.e., GETSEC[SENTER]’s rendezvous event message) events also cause asynchronous enclave
exits. Note that SignalTXTMsg[SEXIT] (i.e., GETSEC[SEXIT]’s teardown message) does not cause an AEX.
On an AEX, information about the event causing the AEX is stored in the SSA (see Section 40.4 for details of AEX).
The information stored in the SSA only describes the first event that triggered the AEX. If parsing/delivery of the
first event results in detection of further events (e.g., VM exit, double fault, etc.), then the event information in the
SSA is not updated to reflect these subsequently detected events.
42.7
INTERACTIONS WITH THE PROCESSOR EXTENDED STATE AND
MISCELLANEOUS STATE
42.7.1 Requirements and Architecture Overview
Processor extended states are the ISA features that are enabled by the settings of CR4.OSXSAVE and the XCR0
register. Processor extended states are normally saved/restored by software via XSAVE/XRSTOR instructions.
Details of discovery of processor extended states and management of these states are described in Chapter 13 of
Intel® 64 and IA-32 Architectures Software Developer’s Manual, Volume 1.
Additionally, the following requirements apply to Intel SGX:
• On an AEX, the Intel SGX architecture must protect the processor extended state and miscellaneous state by
saving them in the enclave’s state-save area (SSA), and clear the secrets from the processor extended state
that is used by an enclave.
• Intel SGX architecture must verify that the SSA frame size is large enough to contain all the processor extended
states and miscellaneous state used by the enclave.
• Intel SGX architecture must ensure that enclaves can only use processor extended state that is enabled by
system software in XCR0.
42-4
Vol. 3D
INTEL® SGX INTERACTIONS WITH IA32 AND INTEL® 64 ARCHITECTURE
• Enclave software should be able to discover only those processor extended state and miscellaneous state for
which such protection is enabled.
• The processor extended states that are enabled inside the enclave must be approved by the enclave developer:
- Certain processor extended state (e.g., Memory Protection Extensions, see Appendix E, “Intel® Memory
Protection Extensions,” of the Intel® 64 and IA-32 Architectures Software Developer’s Manual, Volume 1)
modify the behavior of the legacy ISA software. If such features are enabled for enclaves that do not
understand those features, then such a configuration could lead to a compromise of the enclave's security.
• The processor extended states that are enabled inside the enclave must form an integral part of the enclave's
identity. This requirement has two implications:
- Service providers may decide to assign different trust level to the same enclave depending on the ISA
features the enclave is using.
To meet these requirements, the Intel SGX architecture defines a sub-field called X-Feature Request Mask (XFRM)
in the ATTRIBUTES field of the SECS. On enclave creation (ENCLS[ECREATE] leaf function), the required SSA frame
size is calculated by the processor from the list of enabled extended and miscellaneous states and verified against
the actual SSA frame size defined by SECS.SSAFRAMESIZE.
On enclave entry, after verifying that XFRM is only enabling features that are already enabled in XCR0, the value in
the XCR0 is saved internally by the processor, and is replaced by the XFRM. On enclave exit, the original value of
XCR0 is restored. Consequently, while inside the enclave, the processor extended states enabled in XFRM are in
enabled state, and those that are disabled in XFRM are in disabled state.
The entire ATTRIBUTES field, including the XFRM subfield is integral part of enclave's identity (i.e., its value is
included in reports generated by ENCLU[EREPORT], and select bits from this field can be included in key-derivation
for keys obtained via the ENCLU[EGETKEY] leaf function).
Enclave developers can create their enclave to work with certain features and fallback to another code path in case
those features aren't available (e.g., optimize for AVX and fallback to SSE). For this purpose Intel SGX provides the
following fields in SIGSTRUCT: ATTRIBUTES, ATTRIBUTESMASK, MISCSELECT, and MISCMASK. EINIT ensures that
the final SECS.ATTRIBUTES and SECS.MISCSELECT comply with the enclave developer's requirements as follows:
SIGSTRUCT.ATTRIBUTES & SIGSTRUCT.ATTRIBUTEMASK = SECS.ATTRIBUTES & SIGSTRUCT.ATTRIBUTEMASK
SIGSTRUCT.MISCSELECT & SIGSTRUCT.MISCMASK = SECS.MISCSELECT & SIGSTRUCT.MISCMASK.
On an asynchronous enclave exit, the processor extended states enabled by XFRM are saved in the current SSA
frame, and overwritten by synthetic state (see Section 40.3 for the definition of the synthetic state). When the
interrupted enclave is resumed via the ENCLU[ERESUME] leaf function, the saved state for processor extended
states enabled by XFRM is restored.
42.7.2 Relevant Fields in Various Data Structures
42.7.2.1 SECS.ATTRIBUTES.XFRM
The ATTRIBUTES field of the SECS data structure (see Section 38.7) contains a sub-field called XSAVE-Feature
Request Mask (XFRM). Software populates this field at the time of enclave creation according to the features that
are enabled by the operating system and approved by the enclave developer.
Intel SGX architecture guarantees that during enclave execution, the processor extended state configuration of the
processor is identical to what is required by the XFRM sub-field. All the processor extended states enabled in XFRM
are saved on AEX from the enclave and restored on ERESUME.
The XFRM sub-field has the same layout as XCR0, and has consistency requirements that are similar to those for
XCR0. Specifically, the consistency requirements on XFRM values depend on the processor implementation and the
set of features enabled in CR4.
Legal values for SECS.ATTRIBUTES.XFRM conform to these requirements:
• XFRM[1:0] must be set to 0x3.
• If the processor does not support XSAVE, or if the system software has not enabled XSAVE, then XFRM[63:2]
must be zero.
• If the processor does support XSAVE, XFRM must contain a value that would be legal if loaded into XCR0.
Vol. 3D
42-5
INTEL® SGX INTERACTIONS WITH IA32 AND INTEL® 64 ARCHITECTURE
The various consistency requirements are enforced at different times in the enclave's life cycle, and the exact
enforcement mechanisms are elaborated in Section 42.7.3 through Section 42.7.6.
On processors not supporting XSAVE, software should initialize XFRM to 0x3. On processors supporting XSAVE,
software should initialize XFRM to be a subset of XCR0 that would be present at the time of enclave execution.
Because bits 0 and 1 of XFRM must always be set, the use of Intel SGX requires that SSE be enabled (CR4.OSFXSR
= 1).
42.7.2.2 SECS.SSAFRAMESIZE
The SSAFRAMESIZE field in the SECS data structure specifies the number of pages which software allocated1 for
each SSA frame, including both the GPRSGX area, MISC area, the XSAVE area (x87 and XMM states are stored in
the latter area), and optionally padding between the MISC and XSAVE area. The GPRSGX area must hold all the
general-purpose registers and additional Intel SGX specific information. The MISC area must hold the Miscella-
neous state as specified by SECS.MISCSELECT, the XSAVE area holds the set of processor extended states specified
by SECS.ATTRIBUTES.XFRM (see Section 38.9 for the layout of SSA and Section 42.7.3 for ECREATE's consistency
checks). The SSA is always in non-compacted format.
If the processor does not support XSAVE, the XSAVE area will always be 576 bytes; a copy of XFRM (which will be
set to 0x3) is saved at offset 512 on an AEX.
If the processor does support XSAVE, the length of the XSAVE area depends on SECS.ATTRIBUTES.XFRM. The
length would be equal to what CPUID.0DH.00H:EBX would return if XCR0 were set to XFRM. The following pseudo
code illustrates how software can calculate this length using XFRM as the input parameter without modifying XCR0:
offset = 576;
size_last_x = 0;
For x=2 to 63
IF (XFRM[x] != 0) Then
tmp_offset = CPUID.0DH.x:EBX[31:0];
IF (tmp_offset >= offset + size_last_x) Then
offset = tmp_offset;
size_last_x = CPUID.0DH.x:EAX[31:0];
FI;
FI;
EndFor
return (offset + size_last_x); (* compute_xsave_size(XFRM), see “ECREATE-Create an SECS page in the Enclave
Page Cache”*)
Where the non-zero bits in XFRM are a subset of non-zero bit fields in XCR0.
The size of the MISC region depends on the setting of SECS.MISCSELECT and can be calculated using the layout
information described in Section 38.9.2
42.7.2.3 XSAVE Area in SSA
The XSAVE area of an SSA frame begins at offset 0 of the frame.
42.7.2.4 MISC Area in SSA
The MISC area of an SSA frame is positioned immediately before the GPRSGX region.
42.7.2.5 SIGSTRUCT Fields
Intel SGX provides the flexibility for an enclave developer to choose the enclave's code path according to the
features that are enabled on the platform (e.g., optimize for AVX and fallback to SSE). See Section 42.7.1 for
details.
1. It is the responsibility of the enclave to actually allocate this memory.
42-6
Vol. 3D
INTEL® SGX INTERACTIONS WITH IA32 AND INTEL® 64 ARCHITECTURE
SIGSTRUCT includes the following fields:
SIGSTRUCT.ATTRIBUTES, SIGSTRUCT.ATTRIBUTEMASK, SIGSTRUCT.MISCSELECT, SIGSTRUCT.MISCMASK.
42.7.2.6 REPORT.ATTRIBUTES.XFRM and REPORT.MISCSELECT
The processor extended states and miscellaneous states that are enabled inside the enclave form an integral part
of the enclave's identity and are therefore included in the enclave's report, as provided by the ENCLU[EREPORT]
leaf function. The REPORT structure includes the enclave's XFRM and MISCSELECT configurations.
42.7.2.7 KEYREQUEST
An enclave developer can specify which bits out of XFRM and MISCSELECT ENCLU[EGETKEY] should include in the
derivation of the sealing key by specifying ATTRIBUTESMASK and MISCMASK in the KEYREQUEST structure.
42.7.3 Processor Extended States and ENCLS[ECREATE]
The ECREATE leaf function of the ENCLS instruction enforces a number of consistency checks described earlier. The
execution of ENCLS[ECREATE] leaf function results in a #GP(0) in any of the following cases:
• SECS.ATTRIBUTES.XFRM[1:0] is not 3.
• The processor does not support XSAVE and any of the following is true:
- SECS.ATTRIBUTES.XFRM[63:2] is not 0.
- SECS.SSAFRAMESIZE is 0.
• The processor supports XSAVE and any of the following is true:
- XSETBV would fault on an attempt to load XFRM into XCR0.
- XFRM[63]=1.
- The SSAFRAME is too small to hold required, enabled states (see Section 42.7.2.2).
42.7.4 Processor Extended States and ENCLU[EENTER]
42.7.4.1 Fault Checking
The EENTER leaf function of the ENCLU instruction enforces a number of consistency requirements described
earlier. The execution of the ENCLU[EENTER] leaf function results in a #GP(0) in any of the following cases:
• If CR4.OSFXSR=0.
• If The processor supports XSAVE and either of the following is true:
- CR4.OSXSAVE=0 and SECS.ATTRIBUTES.XFRM is not 3.
- (SECS.ATTRIBUTES.XFRM & XCR0) != SECS.ATTRIBUTES.XFRM
42.7.4.2 State Loading
If ENCLU[EENTER] is successful, the current value of XCR0 is saved internally by the processor and replaced by
SECS.ATTRIBUTES.XFRM.
Vol. 3D
42-7
INTEL® SGX INTERACTIONS WITH IA32 AND INTEL® 64 ARCHITECTURE
42.7.5 Processor Extended States and AEX
42.7.5.1 State Saving
On an AEX, processor extended states are saved into the XSAVE area of the SSA frame in a compatible format with
XSAVE that was executed with EDX:EAX = SECS.ATTRIBUTES.XFRM, with the memory operand being the XSAVE
area, and (for 64-bit enclaves) as if REX.W=1. The XSTATE_BV part of the XSAVE header is saved with 0 for every
bit that is 0 in XFRM. Other bits may be saved as 0 if the state saved is initialized.
Note that enclave entry ensures that if CR4.OSXSAVE is set to 0, then SECS.ATTRIBUTES.XFRM is set to 3. It
should also be noted that it is not possible to enter an enclave with FXSAVE disabled.
42.7.5.2 State Synthesis
After saving the extended state, the processor restores XCR0 to the value it held at the time of the most recent
enclave entry.
The state of features corresponding to bits set in XFRM is synthesized. In general, these states are initialized.
Details of state synthesis on AEX are documented in Section 40.3.1.
42.7.6 Processor Extended States and ENCLU[ERESUME]
42.7.6.1 Fault Checking
The ERESUME leaf function of the ENCLU instruction enforces a number of consistency requirements described
earlier. Specifically, the ENCLU[ERESUME] leaf function results in a #GP(0) in any of the following cases:
• CR4.OSFXSR=0.
• The processor supports XSAVE and either of the following is true:
- CR4.OSXSAVE=0 and SECS.ATTRIBUTES.XFRM is not 3.
- (SECS.ATTRIBUTES.XFRM & XCR0) != SECS.ATTRIBUTES.XFRM.
A successful execution of ENCLU[ERESUME] loads state from the XSAVE area of the SSA frame in a fashion similar
to that used by the XRSTOR instruction. Data in the XSAVE area that would cause the XRSTOR instruction to fault
will cause the ENCLU[ERESUME] leaf function to fault. Examples include, but are not restricted to the following:
• A bit is set in the XSTATE_BV field and clear in XFRM.
• The required bytes in the header are not clear.
• Loading data would set a reserved bit in MXCSR.
Any of these conditions will cause ERESUME to fault, even if CR4.OSXSAVE=0.
42.7.6.2 State Loading
If ENCLU[ERESUME] is successful, the current value of XCR0 is saved internally by the processor and replaced by
SECS.ATTRIBUTES.XFRM.
State is loaded from the XSAVE area of the SSA frame as if the XRSTOR instruction were executed with
XCR0=XFRM, EDX:EAX = XFRM, with the memory operand being the XSAVE area, and (for 64-bit enclaves) as if
REX.W=1.
ENCLU[ERESUME] ensures that a subsequent execution of XSAVEOPT inside the enclave will operate properly (e.g.,
by marking all state as modified).
42.7.7 Processor Extended States and ENCLU[EEXIT]
The ENCLU[EEXIT] leaf function does not perform any X-feature specific consistency checks, nor performs any
state synthesis. It is the responsibility of enclave software to clear any sensitive data from the registers before
42-8
Vol. 3D
INTEL® SGX INTERACTIONS WITH IA32 AND INTEL® 64 ARCHITECTURE
executing EEXIT. However, successful execution of the ENCLU[EEXIT] leaf function restores XCR0 to the value it
held at the time of the most recent enclave entry.
42.7.8 Processor Extended States and ENCLU[EREPORT]
The ENCLU[EREPORT] leaf function creates the MAC-protected REPORT structure that reports on the enclave’s
identity. ENCLU[EREPORT] includes in the report the values of SECS.ATTRIBUTES.XFRM and SECS.MISCSELECT.
42.7.9 Processor Extended States and ENCLU[EGETKEY]
The ENCLU[EGETKEY] leaf function returns a cryptographic key based on the information provided by the KEYRE-
QUEST structure. Intel SGX provides the means for isolation between different operating conditions by allowing an
enclave developer to select which bits out of XFRM and MISCSELECT need to be included in the derivation of the
keys.
42.8
INTERACTIONS WITH SMM
42.8.1 Availability of Intel® SGX instructions in SMM
Enclave instructions are not available in SMM, and any attempt to execute ENCLS or ENCLU instructions inside SMM
results in an invalid-opcode exception (#UD).
42.8.2 SMI while Inside an Enclave
If the logical processor executing inside an enclave receives an SMI, the logical processor exits the enclave asyn-
chronously. The response to an SMI received while executing inside an enclave depends on whether the dual-
monitor treatment is enabled. For detailed discussion of transfer to SMM, see Chapter 34, “System Management
Mode‚” of the Intel® 64 and IA-32 Architectures Software Developer’s Manual, Volume 3C.
If the logical processor executing inside an enclave receives an SMI when dual-monitor treatment is not enabled,
the logical processor exits the enclave asynchronously, and transfers the control to the SMM handler. In addition to
saving the synthetic architectural state to the SMRAM State Save Map (SSM), the logical processor also sets the
“incident to enclave mode” bit in the SMRAM SSM (bit position 1 in SMRAM field at offset 7EE0H). RSM reads this
bit to ensure proper treatment of any VM exit due to an event pending following RSM (see Section 30.2.1 for
details).
If the logical processor executing inside an enclave receives an SMI when dual-monitor treatment is enabled, the
logical processor exits the enclave asynchronously, and transfers the control to the SMM monitor via SMM VM exit.
The SMM VM exit sets the “Enclave Interruption” bit in the Exit Reason (see Table 42-1) and in the Guest Interrupt-
ibility State field (see Table 42-2) of the SMM VMCS.
42.8.3 SMRAM Synthetic State of AEX Triggered by SMI
All processor registers saved in the SMRAM have the same synthetic values listed in Section 40.3. Additional
SMRAM fields that are treated specially on SMI are:
Table 42-1. SMRAM Synthetic States on Asynchronous Enclave Exit
Position
Field
Value
Writable
SMRAM Offset 07EE0H.Bit 1
ENCLAVE_INTERRUPTION
Set to 1 if exit occurred in enclave mode
No
Vol. 3D
42-9
INTEL® SGX INTERACTIONS WITH IA32 AND INTEL® 64 ARCHITECTURE
42.9
INTERACTIONS OF INIT, SIPI, AND WAIT-FOR-SIPI WITH INTEL® SGX
INIT received inside an enclave, while the logical processor is not in VMX operation, causes the logical processor to
exit the enclave asynchronously. After the AEX, the processor's architectural state is initialized to “Power-on” state
(Table 9.1 in Intel® 64 and IA-32 Architectures Software Developer’s Manual, Volume 3A). If the logical processor
is BSP, then it proceeds to execute the BIOS initialization code. If the logical processor is an AP, it enters wait-for-
SIPI state.
INIT received inside an enclave, while the logical processor (LP) is in VMX root operation, follows regular Intel
Architecture behavior and is blocked.
INIT received inside an enclave, while the logical processor is in VMX non-root operation, causes an AEX. Subse-
quent to the AEX, the INIT causes a VM exit with the Enclave Interruption bit in the exit-reason field in the VMCS.
A processor cannot be inside an enclave in the wait-for-SIPI state. Consequently, a SIPI received while inside an
enclave is lost.
Intel SGX does not change the behavior of the processor in the wait-for-SIPI state.
The SGX-related processor states after INIT-SIPI-SIPI is as follows:
• EPC Settings: Unchanged
• EPCM: Unchanged
• CPUID.12H.*: Unchanged
• ENCLAVE_MODE: 0 (LP exits enclave asynchronously)
• MEE state: Unchanged
Software should be aware that following INIT-SIPI-SIPI, the EPC might contain valid pages and should take appro-
priate measures such as initialize the EPC with the EREMOVE leaf function.
42.10 INTERACTIONS WITH DMA
DMA is not allowed to access any Processor Reserved Memory.
42.11 INTERACTIONS WITH TXT
42.11.1 Enclaves Created Prior to Execution of GETSEC
Enclaves which have been created before the GETSEC[SENTER] leaf function are available for execution after the
successful completion of GETSEC[SENTER] and the corresponding SINIT ACM. Actions that a TXT Launched Envi-
ronment performs in preparation to execute code in the Launched Environment, also applies to enclave code that
would run after GETSEC[SENTER].
42.11.2 Interaction of GETSEC with Intel® SGX
All leaf functions of the GETSEC instruction are illegal inside an enclave, and results in an invalid-opcode exception
(#UD).
Responding Logical Processors (RLP) which are executing inside an enclave at the time a GETSEC[SENTER] event
occurs perform an AEX from the enclave and then enter the Wait-for-SIPI state.
RLP executing inside an enclave at the time of GETSEC[SEXIT], behave as defined for GETSEC[SEXIT]-that is, the
RLPs pause during execution of SEXIT and resume after the completion of SEXIT.
The execution of a TXT launch does not affect Intel SGX configuration or security parameters.
42-10
Vol. 3D
INTEL® SGX INTERACTIONS WITH IA32 AND INTEL® 64 ARCHITECTURE
42.11.3 Interactions with Authenticated Code Modules (ACMs)
Intel SGX only allows launching ACMs with an Intel SGX SVN that is at the same level or higher than the expected
Intel SGX SVN. The expected Intel SGX SVN is specified by BIOS and locked down by the processor on the first
successful execution of an Intel SGX instruction that doesn’t return an error code. Intel SGX provides interfaces for
system software to discover whether a non faulting Intel SGX instruction has been executed, and evaluate the suit-
ability of the Intel SGX SVN value of any ACM that is expected to be launched by the OS or the VMM.
These interfaces are provided through a read-only MSR called the IA32_SGX_SVN_STATUS MSR (MSR address
500h). The IA32_SGX_SVN_STATUS MSR has the format shown in Table 42-2.
Table 42-2. Layout of the IA32_SGX_SVN_STATUS MSR
Bit Position
Name
ACM Module ID
Value
0
Lock
N.A.
• If 1, indicates that a non-faulting Intel SGX instruction has been
executed, consequently, launching a properly signed ACM but with Intel
SGX SVN value less than the BIOS specified Intel SGX SVN threshold
would lead to an TXT shutdown.
• If 0, indicates that the processor will allow a properly signed ACM to
launch irrespective of the Intel SGX SVN value of the ACM.
15:1
RSVD
N.A.
0
23:16
SGX_SVN_SINIT
SINIT ACM
• If CPUID.01H:ECX.SMX =1, this field reflects the expected threshold of
Intel SGX SVN for the SINIT ACM.
• If CPUID.01H:ECX.SMX =0, this field is reserved (0).
63:24
RSVD
N.A.
0
OS/VMM that wishes to launch an architectural ACM such as SINIT is expected to read the IA32_SGX_SVN_STATUS
MSR to determine whether the ACM can be launched or a new ACM is needed:
• If either the Intel SGX SVN of the ACM is greater than the value reported by IA32_SGX_SVN_STATUS, or the
lock bit in the IA32_SGX_SVN_STATUS is not set, then the OS/VMM can safely launch the ACM.
• If the Intel SGX SVN value reported in the corresponding component of the IA32_SGX_SVN_STATUS is greater
than the Intel SGX SVN value in the ACM's header, and if bit 0 of IA32_SGX_SVN_STATUS is 1, then the
OS/VMM should not launch that version of the ACM. It should obtain an updated version of the ACM either from
the BIOS or from an external resource.
However, OSVs/VMMs are strongly advised to update their version of the ACM any time they detect that the Intel
SGX SVN of the ACM carried by the OS/VMM is lower than that reported by IA32_SGX_SVN_STATUS MSR, irre-
spective of the setting of the lock bit.
42.12 INTERACTIONS WITH CACHING OF LINEAR-ADDRESS TRANSLATIONS
Entering and exiting an enclave causes the logical processor to flush all the global linear-address context as well as
the linear-address context associated with the current VPID and PCID. The MONITOR FSM is also cleared.
42.13 INTERACTIONS WITH INTEL® TRANSACTIONAL SYNCHRONIZATION
EXTENSIONS (INTEL® TSX)
1. ENCLU or ENCLS instructions inside an HLE region will cause the flow to be aborted and restarted non-specula-
tively. ENCLU or ENCLS instructions inside an RTM region will cause the flow to be aborted and transfer control to
the fallback handler.
2. If XBEGIN is executed inside an enclave, the processor does NOT check whether the address of the fallback
handler is within the enclave.
3. If an RTM transaction is executing inside an enclave and there is an attempt to fetch an instruction outside the
enclave, the transaction is aborted and control is transferred to the fallback handler. No #GP is delivered.
Vol. 3D
42-11
INTEL® SGX INTERACTIONS WITH IA32 AND INTEL® 64 ARCHITECTURE
4. If an RTM transaction is executing inside an enclave and there is a data access to an address within the enclave
that denied due to EPCM content (e.g., to a page belonging to a different enclave), the transaction is aborted and
control is transferred to the fallback handler. No #GP is delivered.
5. If an RTM transaction executing inside an enclave aborts and the address of the fallback handler is outside the
enclave, a #GP is delivered after the abort (EIP reported is that of the fallback handler).
42.13.1 HLE and RTM Debug
RTM debug will be suppressed on opt-out enclave entry. After opt-out entry, the logical processor will behave as if
IA32_DEBUG_CTL[15]=0. Any #DB detected inside an RTM transaction region will just cause an abort with no
exception delivered.
After opt-in entry, if either DR7[11] = 0 OR IA32_DEBUGCTL[15] = 0, any #DB or #BP detected inside an RTM
transaction region will just cause an abort with no exception delivered.
After opt-in entry, if DR7[11] = 1 AND IA32_DEBUGCTL[15] = 1, any #DB or #BP detected inside an RTM transla-
tion will
• terminate speculative execution,
• set RIP to the address of the XBEGIN instruction, and
• be delivered as #DB (implying an Intel SGX AEX; any #BP is converted to #DB).
• DR6[16] will be cleared, indicating RTM debug (if the #DB causes a VM exit, DR6 is not modified but bit 16 of
the pending debug exceptions field in the VMCS will be set).
42.14 INTEL® SGX INTERACTIONS WITH S STATES
Whenever an Intel SGX enabled processor enters S3-S5 state, enclaves are destroyed. This is due to the EPC being
destroyed when power down occurs. It is the application runtime’s responsibility to re-instantiate an enclave after
a power transition for which the enclaves were destroyed.
42.15 INTEL® SGX INTERACTIONS WITH MACHINE CHECK ARCHITECTURE (MCA)
42.15.1 Interactions with MCA Events
All architecturally visible machine check events (#MC and CMCI) that are detected while inside an enclave cause an
asynchronous enclave exit.
Any machine check exception (#MC) that occurs after Intel SGX is first enables causes Intel SGX to be disabled,
(CPUID.12H.00H:EAX.SGX1 == 0). It cannot be enabled until after the next reset.
42.15.2 Machine Check Enables (IA32_MCi_CTL)
All supported IA32_MCi_CTL bits for all the machine check banks must be set for Intel SGX to be available
(CPUID.12H.00H:EAX.SGX1 == 1). Any act of clearing bits from '1 to '0 in any of the IA32_MCi_CTL register may
disable Intel SGX (set CPUID.12H.00H:EAX.SGX1 to 0) until the next reset.
42.15.3 CR4.MCE
CR4.MCE can be set or cleared with no interactions with Intel SGX.
42-12
Vol. 3D
INTEL® SGX INTERACTIONS WITH IA32 AND INTEL® 64 ARCHITECTURE
42.16 INTEL® SGX INTERACTIONS WITH PROTECTED MODE VIRTUAL
INTERRUPTS
ENCLS[EENTER] modifies neither EFLAGS.VIP nor EFLAGS.VIF.
ENCLS[ERESUME] loads EFLAGS in a manner similar to that of an execution of IRET with CPL = 3. This means that
ERESUME modifies neither EFLAGS.VIP nor EFLAGS.VIF regardless of the value of the EFLAGS image in the SSA
frame.
AEX saves EFLAGS.VIP and EFLAGS.VIF unmodified into the EFLAGS image in the SSA frame. AEX modifies neither
EFLAGS.VIP nor EFLAGS.VIF after saving EFLAGS.
If CR4.PVI = 1, CPL = 3, EFLAGS.VM = 0, IOPL < 3, EFLAGS.VIP = 1, and EFLAGS.VIF = 0, execution of STI causes
a #GP fault. In this case, STI modifies neither EFLAGS.IF nor EFLAGS.VIF. This behavior applies without change
within an enclave (where CPL is always 3). Note that, if IOPL = 3, STI always sets EFLAGS.IF without fault;
CR4.PVI, EFLAGS.VIP, and EFLAGS.VIF are neither consulted nor modified in this case.
42.17 INTEL SGX INTERACTION WITH PROTECTION KEYS
SGX interactions with PKRU are as follows:
• CPUID.12H.01H:ECX.PKRU indicates whether SECS.ATTRIBUTES.XFRM.PKRU can be set. If SECS.ATTRI-
BUTES.XFRM.PKRU is set, then PKRU is saved and cleared as part of AEX and is restored as part of ERESUME.
If CR4.PKE is set, an enclave can execute RDPKRU and WRKRU independent of whether SECS.ATTRI-
BUTES.XFRM.PKRU is set.
SGX interactions with domain permission checks are as follows:
1) If CR4.PKE is not set, then legacy and SGX permission checks are not effected.
2) If CR4.PKE is set, then domain permission checks are applied to all non-enclave access and
enclave accesses to user pages in addition to legacy and SGX permission checks at a higher
priority than SGX permission checks.
3) Implicit accesses aren't subject to domain permission checks.
Vol. 3D
42-13
INTEL® SGX INTERACTIONS WITH IA32 AND INTEL® 64 ARCHITECTURE
42-14
Vol. 3D
ENCLAVE CODE DEBUG AND PROFILING
CHAPTER 43
ENCLAVE CODE DEBUG AND PROFILING
Intel® SGX is architected to provide protection for production enclaves and permit enclave code developers to use
an SGX-aware debugger to effectively debug a non-production enclave (debug enclave). Intel SGX also allows a
non-SGX-aware debugger to debug non-enclave portions of the application without getting confused by enclave
instructions.
43.1
CONFIGURATION AND CONTROLS
43.1.1 Debug Enclave vs. Production Enclave
The SECS of each enclave provides a bit, SECS.ATTRIBUTES.DEBUG, indicating whether the enclave is a debug
enclave (if set) or a production enclave (if 0). If this bit is set, software outside the enclave can use
EDBGRD/EDBGWR to access the EPC memory of the enclave. The value of DEBUG is not included in the measure-
ment of the enclave and therefore doesn't require an alternate SIGSTRUCT to be generated to debug the enclave.
The ATTRIBUTES field in the SECS is reported in the enclave's attestation, and is included in the key derivation.
Enclave secrets that were protected by the enclave using Intel SGX keys when it ran as a production enclave will
not be accessible by the debug enclave. A debugger needs to be aware that special debug content might be
required for a debug enclave to run in a meaningful way.
EPC memory belonging to a debug enclave can be accessed via the EDBGRD/EDBGWR leaf functions (see Section
41.4), while that belonging to a non-debug enclave cannot be accessed by these leaf functions.
43.1.2 Tool-Chain Opt-in
The TCS.FLAGS.DBGOPTIN bit controls interactions of certain debug and profiling features with enclaves, including
code/data breakpoints, TF, RF, monitor trap flag, BTF, LBRs, BTM, BTS, Intel Processor Trace, and performance
monitoring. This bit is forced to zero when EPC pages are added via EADD. A debugger can set this bit via EDBGWR
to the TCS of a debug enclave.
An enclave entry through a TCS with the TCS.FLAGS.DBGOPTIN set to 0 is called an opt-out entry. Conversely, an
enclave entry through a TCS with TCS.FLAGS.DBGOPTIN set to 1 is called an opt-in entry.
43.1.3 Debugging an Enclave That Uses Asynchronous Enclave Exit Notify
Whenever an opt-in enclave entry is used to perform enclave code debugging or profiling, the debugger or profiling
tool may clear TCS.FLAGS.AEXNOTIFY to prevent AEX notifications from being delivered at each interrupt, break-
point, trap, or other exception.
43.2
SINGLE STEP DEBUG
43.2.1 Single Stepping ENCLS Instruction Leafs
If the RFLAGS.TF bit is set at the beginning of ENCLS, then a single-step debug exception is pending as a trap-class
exception on the instruction boundary immediately after the ENCLS instruction. Additionally, if the instruction is
executed in VMX non-root operation and the “monitor trap flag” VM-execution control is 1, an MTF VM exit is
pending on the instruction boundary immediately after the instruction if the instruction does not fault.
Vol. 3D
43-1
ENCLAVE CODE DEBUG AND PROFILING
43.2.2 Single Stepping ENCLU Instruction Leafs
The interactions of the unprivileged Intel SGX instruction ENCLU are leaf dependent.
An enclave entry via EENTER/ERESUME leaf functions of the ENCLU, in certain cases, may mask the RFLAGS.TF bit,
and mask the setting of the “monitor trap flag” VM-execution control. In such situations, an exit from the enclave,
either via the EEXIT leaf function or via an AEX unmasks the RFLAGS.TF bit and the “monitor trap flag” VM-execu-
tion control. The details of this masking/unmasking and the pending of single stepping events across
EENTER/ERESUME/EEXIT/AEX are covered in detail in Section 43.2.3.
If the EFLAGS.TF bit is set at the beginning of EREPORT or EGETKEY leafs, and if the EFLAGS.TF is not masked by
the preceding enclave entry, then a single-step debug exception is pending on the instruction boundary immedi-
ately after the ENCLU instruction. Additionally, if the instruction is executed in VMX non-root operation and the
“monitor trap flag” VM-execution control is 1, and if the monitor trap flag is not masked by the preceding enclave
entry, then an MTF VM exit is pending on the instruction boundary immediately after the instruction.
If the instruction under consideration results in a fault, then the control flow goes to the fault handler, and no
single-step debug exception is asserted. In such a situation, if the instruction is executed in VMX non-root opera-
tion and the “monitor trap flag” VM-execution control is 1, an MTF VM exit is pending after the delivery of the fault
(or any nested exception). No MTF VM exit occurs if another VM exit occurs before reaching that boundary on which
an MTF VM exit would be pending.
43.2.3 Single-Stepping Enclave Entry with Opt-out Entry
43.2.3.1 Single Stepping without AEX
Figure 43-1 shows the most common case for single-stepping after an opt-out entry.
EENTER
ERESUME
Inst1
Inst2
Inst3
EEXIT
Inst4
TF/MTF
Handler
SMI
INIT
RFLAGS.TF
Single-Step #DB Pending
#MC
Higher Priority
VMCS.MTF
MTF VM Exit Pending
Handler
Figure 43-1. Single Stepping with Opt-out Entry - No AEX
In this scenario, if the RFLAGS.TF bit is set at the time of the enclave entry, then a single step debug exception is
pending on the instruction boundary after EEXIT. Additionally, if the enclave is executing in VMX non-root operation
and the “monitor trap flag” VM-execution control is 1, an MTF VM exit is pending on the instruction boundary after
EEXIT.
The value of the RFLAGS.TF bit at the end of EEXIT is the same as the value of RFLAGS.TF at the time of the enclave
entry.
43.2.3.2 Single Step Preempted by AEX Due to Non-SMI Event
Figure 43-2 shows the interaction of single stepping with AEX due to a non-SMI event after an opt-out entry.
43-2
Vol. 3D
ENCLAVE CODE DEBUG AND PROFILING
EENTER
ERESUME
Inst1
Inst2
Inst3
EEXIT
Inst4
TF/MTF
Event Inside Enclave
AEX
Handler
Higher Priority
Single-Step #DB Pending
Handler
RFLAGS.TF
AEX
MTF VM Exit Pending
Handler
VMCS.MTF
Figure 43-2. Single Stepping with Opt-out Entry -AEX Due to Non-SMI Event Before Single-Step Boundary
In this scenario, if the enclave is executing in VMX non-root operation and the “monitor trap flag” VM-execution
control is 1, an MTF VM exit is pending on the instruction boundary after the AEX. No MTF VM exit occurs if another
VM exit happens before reaching that instruction boundary.
The value of the RFLAGS.TF bit at the end of AEX is the same as the value of RFLAGS.TF at the time of the enclave
entry.
43.2.4 RFLAGS.TF Treatment on AEX
The value of EFLAGS.TF at the end of AEX from an opt-out enclave is same as the value of EFLAGS.TF at the time
of the enclave entry. The value of EFLAGS.TF at the end of AEX from an opt-in enclave is unmodified. The
EFLAGS.TF saved in GPR portion of the SSA on an AEX is 0. For more detail see EENTER and ERESUME in Chapter 5.
43.2.5 Restriction on Setting of TF after an Opt-Out Entry
Enclave entered through an opt-out entry is not allowed to set EFLAGS.TF. The POPF instruction forces RFLAGS.TF
to 0 if the enclave was entered through opt-out entry.
43.2.6 Trampoline Code Considerations
Any AEX from the enclave which results in the RFLAGS.TF =1 on the reporting stack will result in a single-step #DB
after the first instruction of the trampoline code if the trampoline is entered using the IRET instruction.
43.3
CODE AND DATA BREAKPOINTS
43.3.1 Breakpoint Suppression
Following an opt-out entry:
• Instruction breakpoints are suppressed during execution in an enclave.
• Data breakpoints are not triggered on accesses to the address range defined by ELRANGE.
• Data breakpoints are triggered on accesses to addresses outside the ELRANGE
Vol. 3D
43-3
ENCLAVE CODE DEBUG AND PROFILING
Following an opt-in entry instruction and data breakpoints are not suppressed.
The processor does not report any matches on debug breakpoints that are suppressed on enclave entry. However,
the processor does not clear any bits in DR6 that were already set at the time of the enclave entry.
43.3.2 Reporting of Instruction Breakpoint on Next Instruction on a Debug Trap
A debug exception caused by the single-step execution mode or when a data breakpoint condition was met causes
the processor to perform an AEX. Following such an AEX, the processor reports in the debug status register (DR6)
matches of the new instruction pointer (the AEP address) in a breakpoint address register setup to detect instruc-
tion execution.
43.3.3 RF Treatment on AEX
RF flag value saved in SSA is the same as what would have been pushed on stack if the exception or event causing
the AEX occurred when executing outside an enclave (see Section 20.3.1.1). Following an AEX, the RF flag is 0 in
the synthetic state.
43.3.4 Breakpoint Matching in Intel® SGX Instruction Flows
Implicit accesses made by Intel SGX instructions to EPC regions do not trigger data breakpoints. Explicit accesses
made by ENCLS[ECREATE], ENCLS[EADD], ENCLS[EEXTEND], ENCLS[EINIT], ENCLS[EREMOVE],
ENCLS[ETRACK], ENCLS[EBLOCK], ENCLS[EPA], ENCLS[EWB], ENCLS[ELD], ENCLS[EDBGRD], ENCLS[EDBGWR],
ENCLU[EENTER], and ENCLU[ERESUME] to the EPC operands do not trigger data breakpoints.
Explicit accesses made by the Intel SGX instructions (ENCLU[EGETKEY] and ENCLU[EREPORT]) executed by an
enclave following an opt-in entry, trigger data breakpoints on accesses to their EPC operands. All Intel SGX instruc-
tions trigger data breakpoints on accesses to their non-EPC operands.
43.4
CONSIDERATION OF THE INT1 AND INT3 INSTRUCTIONS
This section considers the operation of the INT1 and INT3 instructions when executed inside an enclave. These are
the instructions with opcodes F1 and CC, respectively, and not INT n (with opcode CD) with value 1 or 3 for n.
43.4.1 Behavior of INT1 and INT3 Inside an Enclave
An execution of either INT1 or INT3 inside an enclave results in a fault-class exception. Following an opt-out entry,
execution of either instruction results in an invalid-opcode exception (#UD). Following opt-in entry, INT1 results in
a debug exception (#DB) and INT3 delivers a breakpoint exception (#BP). The normal requirement for INT3 (that
the CPL not be greater than the DPL of descriptor 3 in the IDT) is not enforced.
Because execution of INT1 or INT3 inside an enclave results in a fault, the RIP saved in the SSA on AEX references
the INT1 or INT3 instruction (and not the following instruction). The RIP value saved on the stack (or in the TSS or
VMCS) is that of the AEP.
If execution of INT1 or INT3 inside an enclave causes a VM exit, the event type in the VM-exit interruption informa-
tion field indicates a hardware exception (type 3),1 and the VM-exit instruction length field is saved as zero.
43.4.2 Debugger Considerations
A debugger using INT3 inside an enclave should account for the modified behavior described in Section 43.4.1.
Because INT3 is fault-like inside an enclave, the RIP saved in the SSA on AEX is that of the INT3 instruction. Conse-
1. INT1 would normally indicate a privileged software exception (type 5), and INT3 would normally indicate a software exception (type
6).
43-4
Vol. 3D
ENCLAVE CODE DEBUG AND PROFILING
quently, the debugger must not decrement SSA.RIP for #BP coming from an enclave to re-execute the instruction
at the RIP of the INT3 instruction on a subsequent enclave entry.
43.4.3 VMM Considerations
As described in Section 43.4.1, execution of INT3 inside an enclave delivers #BP with “interruption type” of 3. A
VMM that re-injects #BP into the guest should establish the VM-entry interruption information field using data
saved into the appropriate VMCS fields by the VM exit incident to the #BP (as recommended in the Intel® 64 and
IA-32 Architectures Software Developer’s Manual, Volume 3C).
VMMs that create the VM-entry interruption information based solely on the exception vector should take care to
use event type 3 (instead of 6) when they detect a VM exit incident to enclave mode that is due to an exception
with vector 3.
43.5
BRANCH TRACING
43.5.1 BTF Treatment
When software enables single-stepping on branches then:
• Following an opt-in entry using EENTER the processor generates a single step debug exception.
• Following an EEXIT the processor generates a single-step debug exception
Enclave entry using ERESUME (opt-in or opt-out) and an AEX from the enclave do not cause generation of the
single-step debug exception.
43.5.2 LBR Treatment
43.5.2.1 LBR Stack on Opt-in Entry
Following an opt-in entry into an enclave, last branch recording facilities if enabled continued to store branch
records in the LBR stack MSRs as follows:
• On enclave entry using EENTER/ERESUME, the processor push the address of EENTER/ERESUME instruction
into MSR_LASTBRANCH_n_FROM_IP, and the destination address of the EENTER/ERESUME into MSR_LAST-
BRANCH_n_TO_IP.
• On EEXIT, the processor pushes the address of EEXIT instruction into MSR_LASTBRANCH_n_FROM_IP, and the
address of EEXIT destination into MSR_LASTBRANCH_n_TO_IP.
• On AEX, the processor pushes RIP saved in the SSA into MSR_LASTBRANCH_n_FROM_IP, and the address of
AEP into MSR_LASTBRANCH_n_TO_IP.
• For every branch inside the enclave, a branch record is pushed on the LBR stack.
Figure 43-3 shows an example of LBR stack manipulation after an opt-in entry. Every arrow in this picture indicates
a branch record pushed on the LBR stack. The “From IP” of the branch record contains the linear address of the
instruction located at the start of the arrow, while the “To IP” of the branch record contains the linear address of
the instruction at the end of the arrow.
Vol. 3D
43-5